ISO 31000, ISO 37001, ISO 55001 and Specialist ISO Training

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

Our ISO 31000 training, alongside courses on ISO 37001, ISO 37301, ISO 55001, ISO 41001, ISO 50001 and ISO 22000, helps specialist teams manage risk, integrity, assets, facilities, energy and food safety with the same management system discipline. SSC delivers Foundation, Internal Auditor and Lead Auditor courses for each certifiable standard, and a practitioner course for ISO 31000, live online or on-site.
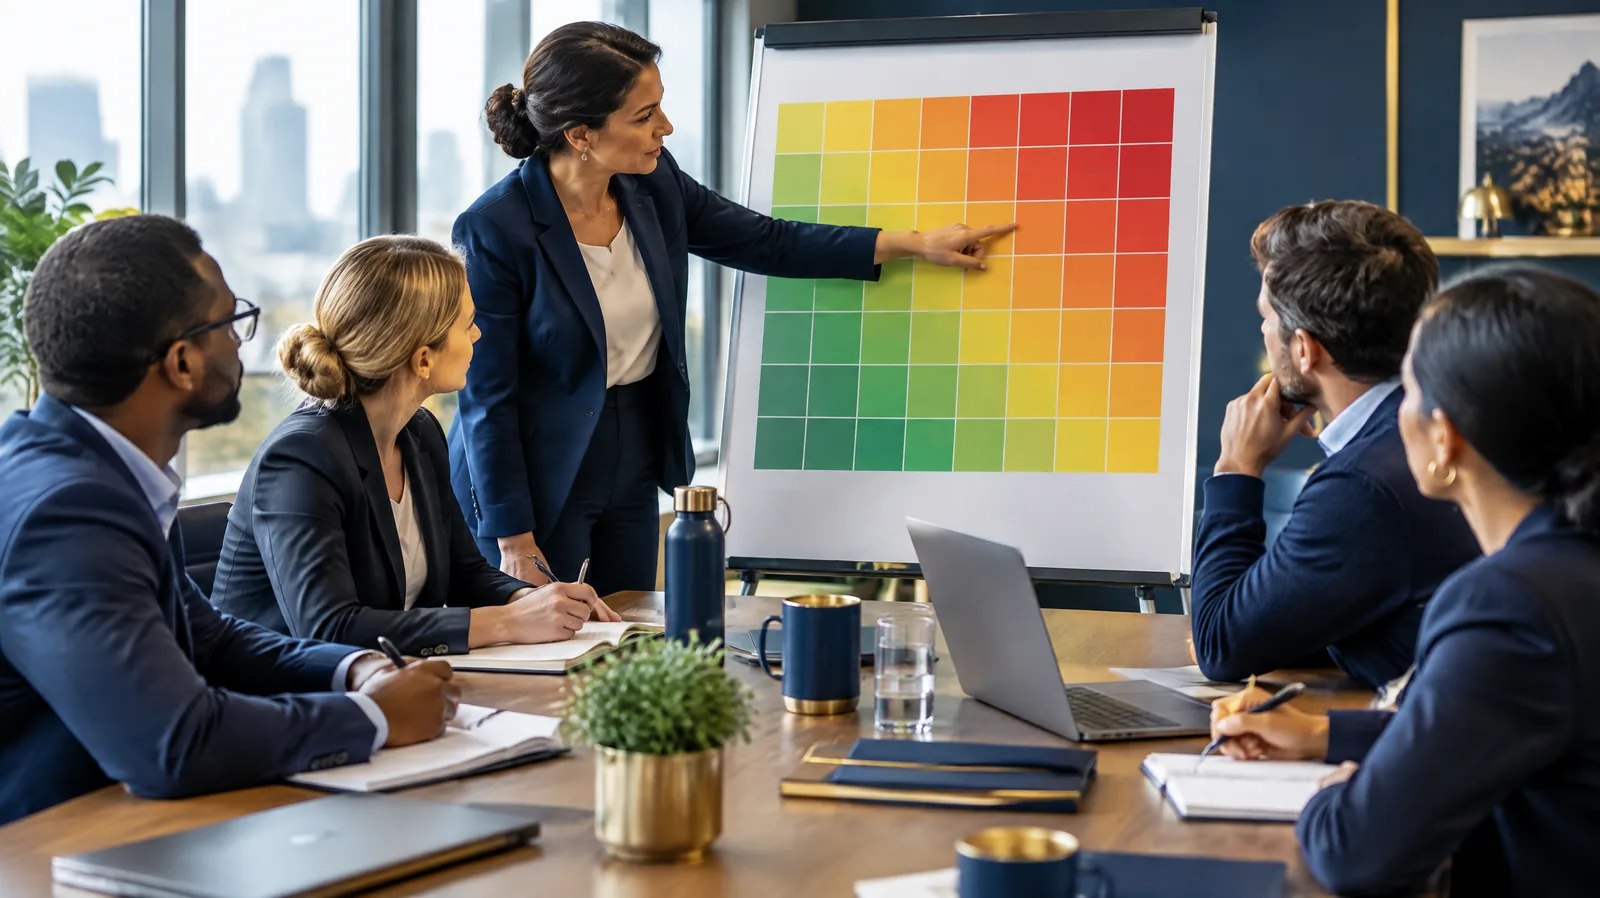
Participants studying a risk heat map poster while the instructor points to a square, representing ISO 31000 risk management training
Specialist standards share one structure, so skills transfer from one system to the next.

Courses at a glance

StandardWhat it coversCourses available
ISO 31000 Risk managementPrinciples, framework and process for managing any type of risk. Guidance, not certifiable.Foundation (1 day), Risk Management Practitioner (3 days)
ISO 37001 Anti-bribery management systemsPreventing, detecting and responding to bribery. Current edition ISO 37001:2025.Foundation, Internal Auditor, Lead Auditor
ISO 37301 Compliance management systemsIdentifying obligations and managing compliance risk across the organisation.Foundation, Internal Auditor, Lead Auditor
ISO 55001 Asset managementGetting value from physical and other assets across their life. Current edition ISO 55001:2024.Foundation, Internal Auditor, Lead Auditor
ISO 41001 Facility managementManaging facilities services to support the organisation’s core activities.Foundation, Internal Auditor, Lead Auditor
ISO 50001 Energy managementImproving energy performance, efficiency and consumption.Foundation, Internal Auditor, Lead Auditor
ISO 22000 Food safety managementHazard control and food safety across the food chain.Foundation, Internal Auditor, Lead Auditor

Typical durations are 2 days for Foundation, 3 days for Internal Auditor and 5 days for Lead Auditor. Several of these standards are being revised; our trainers teach the edition your organisation is certified to and explain upcoming changes.

ISO 31000 risk management training

ISO 31000:2018 provides principles, a framework and a process for managing risk of any kind. Because it is guidance rather than a set of requirements, organisations cannot be certified to it, so instead of auditor courses we offer a Foundation course and a three-day Risk Management Practitioner course. Participants learn to set risk criteria, run identification workshops, analyse likelihood and consequence, choose treatments and report to the board. Read our guide to the enterprise risk management process to see the method we teach.

ISO 31000 training suits risk managers, chief risk officers and their teams, internal auditors, project and program managers, and executives who approve risk appetite. It also gives a strong foundation for sector rules that build on the same process, such as APRA CPS 220 and CPS 230, and the SOCI Act Critical Infrastructure Risk Management Program.
Risk Management Practitioner course outline

  1. Day 1: principles, framework design, risk appetite, criteria and taxonomy.
  2. Day 2: facilitating identification workshops, analysis and evaluation, inherent and residual risk, and control effectiveness.
  3. Day 3: treatment planning, key risk indicators, reporting to the board, and continual improvement.

ISO 37001 anti-bribery and ISO 37301 compliance training

Hand pushing back an envelope across a desk beside a contract, representing ISO 37001 anti-bribery training
Anti-bribery controls protect people and organisations from decisions they cannot take back.

ISO 37001:2025, published in February 2025, replaced the 2016 edition with new requirements on conflicts of interest, an anti-bribery compliance culture and climate considerations, and aligned its wording with related standards such as ISO 37002 for whistleblowing. Our courses cover bribery risk assessment, due diligence on business associates, gifts and hospitality controls, financial and non-financial controls, raising concerns, and investigation. ISO 37301 courses take the same approach to all compliance obligations and pair well with our compliance risk management services.
ISO 55001, ISO 41001 and ISO 50001 training

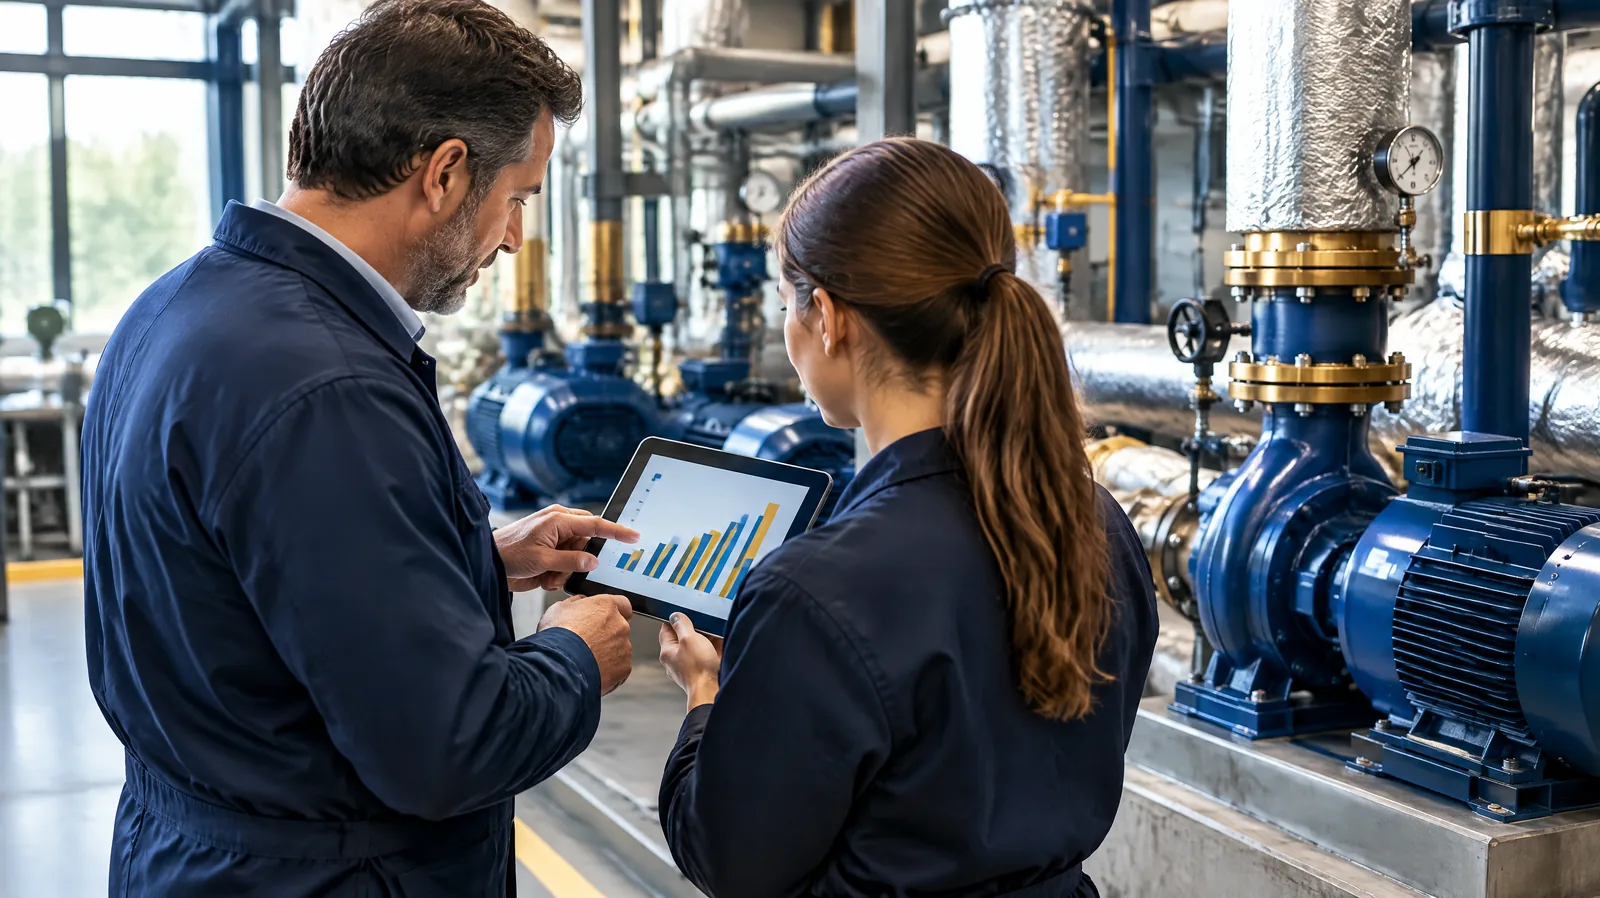
Facility manager and trainee checking an energy chart on a tablet in a plant room, representing ISO 55001, ISO 41001 and ISO 50001 training
Asset, facility and energy management all depend on good data and clear decisions.
  • ISO 55001:2024 asset management: asset management policy and strategy, the strategic asset management plan, life cycle decision making, asset data and information, and performance evaluation.
  • ISO 41001 facility management: understanding the needs of the organisation and its occupants, service delivery, outsourced providers and performance measurement.
  • ISO 50001 energy management: energy review, significant energy uses, energy baselines and performance indicators, action plans and measurement.
  • ISO 22000 food safety: prerequisite programmes, hazard analysis and HACCP principles, operational controls and traceability.

How the specialist ISO training is delivered

  • Live online. Instructor-led virtual classes over Microsoft Teams or Zoom, with breakout exercises, shared workbooks and the option to split longer courses into half-day sessions across a week or two.
  • On-site at your premises. Private training for your team at your office, delivered by a consultant who can use your own policies, systems and examples in the exercises.
  • Private and tailored. Every course can be run for a single organisation, with case studies drawn from your sector and the depth adjusted to your team’s experience.

What participants receive

  • A course workbook and the slides used in class
  • Reusable templates and checklists, such as audit checklists, risk registers and report formats, depending on the course
  • A case study pack and practice questions
  • A certificate of completion from Security Solution Consultants

Certificates and accredited exams

Every participant who completes a course receives a certificate of completion from Security Solution Consultants. Lead Auditor and Lead Implementer courses can include an accredited certification exam through our accredited training partner, for standards where the partner offers one. Your quote confirms the exam body, exam format and certificate for each course, so there are no surprises on the day.

Why train with SSC

  • Taught by practitioners. Our trainers are working consultants and auditors who design risk, compliance and management systems and audit them against international standards, so examples come from real engagements rather than slides.
  • We hold ourselves to the same standard. SSC is certified to ISO/IEC 27001 and follows a Secure by Design approach. See our Trust Centre.
  • Hands-on with real tools. Exercises can use GRCLens, the GRC platform built by SSC, so participants practise with risk registers, control libraries and evidence the way they will at work.
  • Training that connects to delivery. If your team needs help after the course, the same people can support implementation, internal audits and certification readiness.

Related: enterprise risk management services and certification and accreditation services. See all training courses.
Frequently asked questions

No. ISO 31000 provides guidelines, not requirements, so it is not certifiable. That is why we offer Foundation and Practitioner courses for ISO 31000 rather than auditor courses.

The 2025 edition, published in February 2025, added requirements on conflicts of interest and an anti-bribery compliance culture, introduced climate considerations and aligned wording with related standards such as ISO 37002.

ISO 55001:2024, which replaced the 2014 edition. Our asset management courses teach the 2024 edition.

Yes. Because these standards share the harmonised structure, we can design an integrated internal auditor course covering the standards your organisation uses.

Every participant receives a certificate of completion. Lead Auditor courses can include an accredited exam through our accredited training partner where one is offered for that standard; your quote confirms the details.

Plan specialist ISO training for your team

Tell us how many people need training, which courses interest you, and whether you prefer live online or on-site delivery. We will come back with a tailored proposal and quote.

Prefer email? Write to info@secsolutionshub.com