PCI DSS Compliance Advisory in Australia and New Zealand

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

PCI DSS compliance is required of every business that stores, processes or transmits payment card data, and of service providers that can affect the security of that data. Security Solution Consultants (SSC) provides PCI DSS compliance advisory for merchants, payment providers, fintechs and SaaS platforms across Australia and New Zealand, from scoping and gap assessment to remediation, Self-Assessment Questionnaires and readiness for an on-site assessment by a Qualified Security Assessor (QSA).
Hand tapping a plain payment card on a modern card terminal, representing PCI DSS compliance for card payments
PCI DSS protects card data wherever it is stored, processed or transmitted.

The current version is PCI DSS v4.0.1. Version 4.0 was retired at the end of 2024, and the requirements that were future-dated in version 4.0 became mandatory on 31 March 2025. If your last assessment was against version 3.2.1 or an early 4.0 baseline, expect new work on targeted risk analysis, authentication, e-commerce payment pages and documentation.

What is PCI DSS?

The Payment Card Industry Data Security Standard is published by the PCI Security Standards Council, founded by the major card brands. It sets twelve requirements, grouped into six goals, for protecting account data:

GoalRequirements
Build and maintain a secure network and systems1. Network security controls. 2. Secure configurations.
Protect account data3. Protect stored account data. 4. Protect cardholder data with strong cryptography during transmission.
Maintain a vulnerability management program5. Protect systems from malicious software. 6. Develop and maintain secure systems and software.
Implement strong access control measures7. Restrict access by business need to know. 8. Identify users and authenticate access. 9. Restrict physical access.
Regularly monitor and test networks10. Log and monitor all access. 11. Test security of systems and networks regularly.
Maintain an information security policy12. Support information security with organisational policies and programs.

PCI compliance in Australia and New Zealand works differently from many other obligations: PCI DSS is not a law. It is a contractual obligation that flows from the card brands through your acquiring bank or payment provider. A card data breach can also trigger notification obligations under the Australian Privacy Act 1988 or the New Zealand Privacy Act 2020.
Our PCI DSS compliance services

  • Scoping and data flow mapping. We trace exactly where card data enters, moves through and leaves your environment, and define the cardholder data environment (CDE) and connected systems.
  • Scope reduction. Tokenisation, point-to-point encryption, hosted payment pages and network segmentation can remove large parts of your environment from scope. We recommend the options that make sense for your business.
  • Gap assessment against PCI DSS v4.0.1. Requirement-by-requirement assessment with evidence, including the requirements that became mandatory in March 2025.
  • Remediation support. Policies, procedures, technical controls and evidence, working with your IT team, developers and payment providers.
  • SAQ completion support. Choosing the right Self-Assessment Questionnaire and completing it accurately with supporting evidence.
  • QSA readiness. A mock assessment before your Report on Compliance (ROC), and support during the QSA’s fieldwork.
  • Service provider compliance. For payment, hosting and SaaS providers whose customers need your Attestation of Compliance (AOC).
  • Ongoing compliance. A compliance calendar for quarterly scans, penetration tests, reviews and training, tracked in GRCLens.

Reduce your PCI DSS scope first

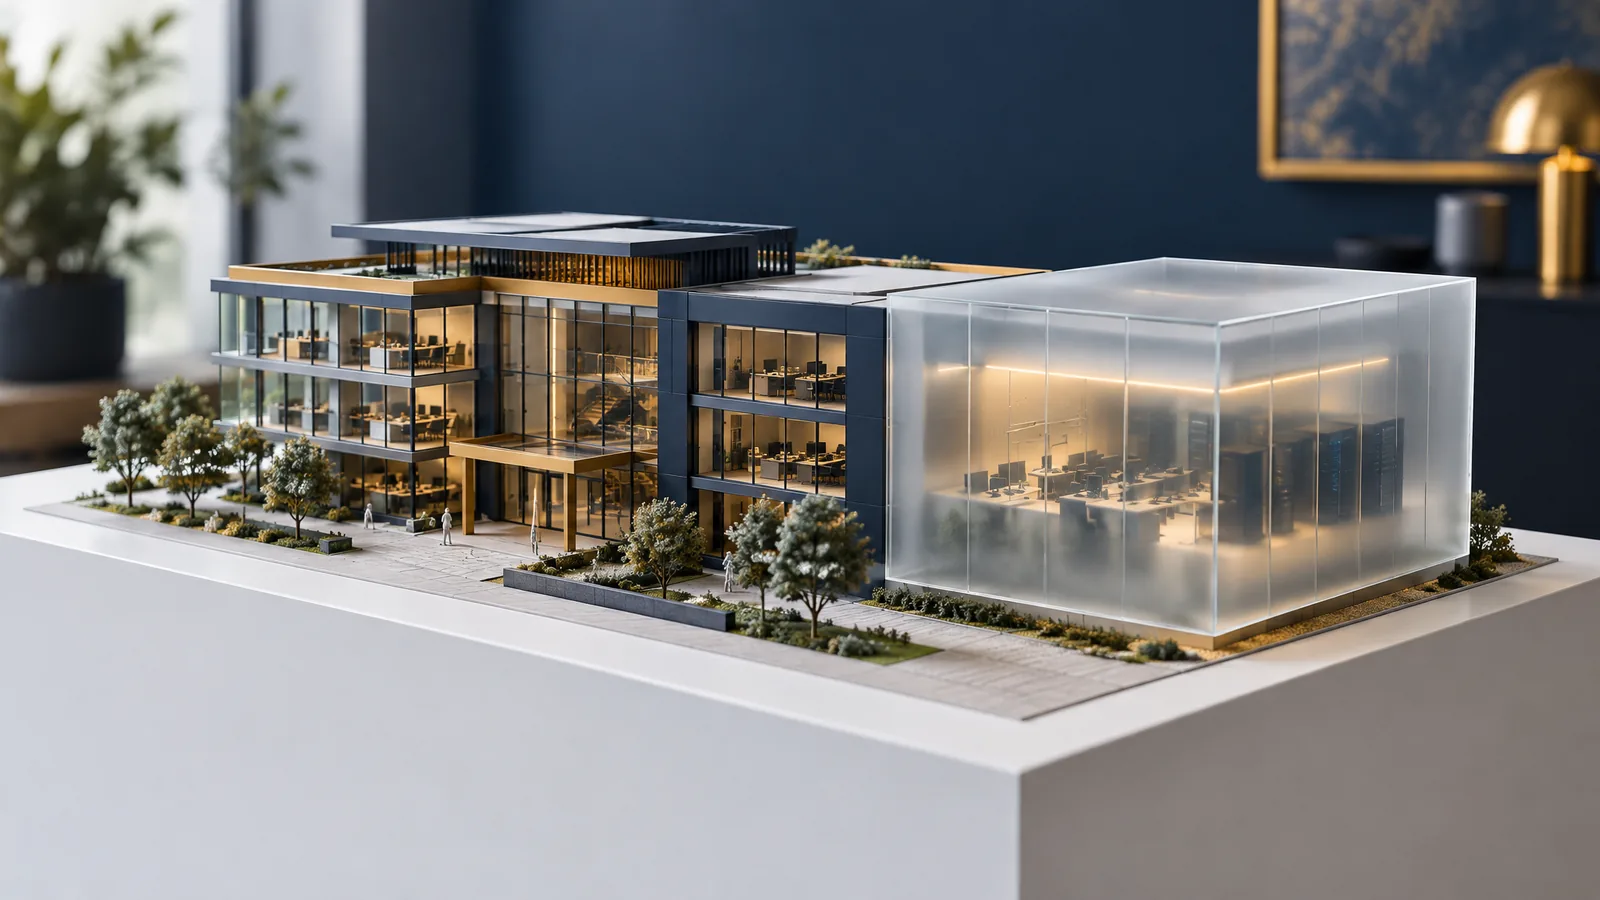
Architectural model with one wing enclosed in a frosted glass box, representing reducing PCI DSS scope through segmentation
The smaller your cardholder data environment, the easier it is to secure and assess.

The most effective PCI DSS project starts by asking how much card data you really need to touch. Every system that stores, processes or transmits card data, and every system that can affect its security, is in scope. Reducing that footprint lowers both risk and assessment effort.

  • Use a PCI DSS compliant payment provider for hosted payment pages or embedded payment fields, so card numbers never reach your servers.
  • Tokenise stored cards for recurring payments instead of keeping primary account numbers.
  • Use validated point-to-point encryption for card-present terminals where available.
  • Segment the network so systems in the CDE are isolated from the rest of the business, and test that segmentation regularly.
  • Remove card data you do not need, including old exports, call recordings and email attachments.

Our article on why PCI DSS scope is everything explains the approach in more detail.
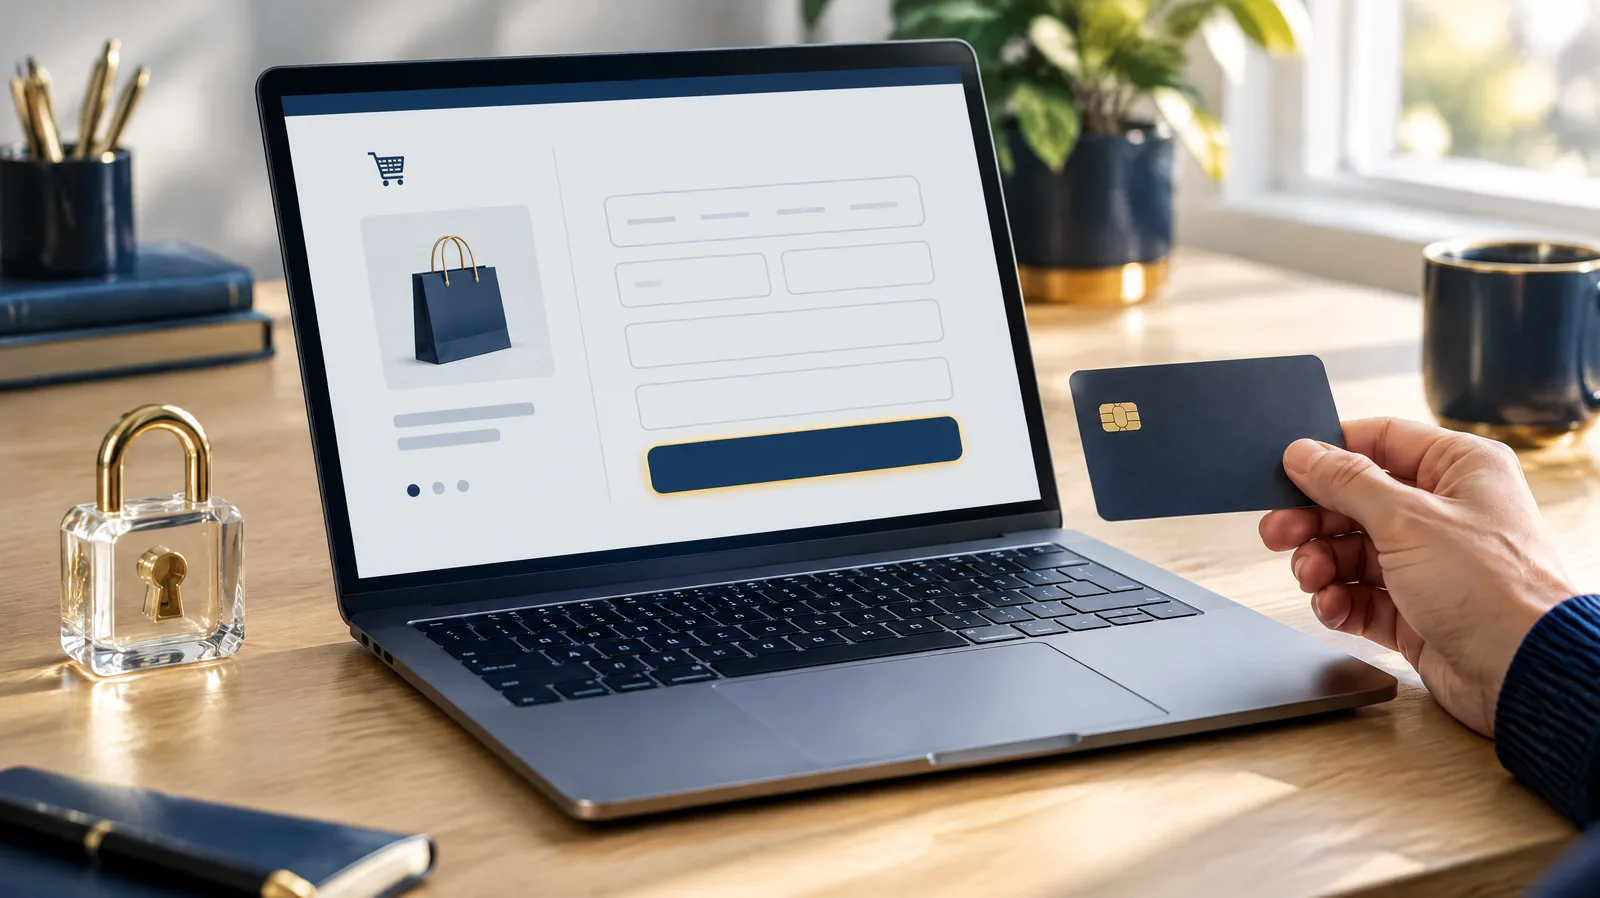
Securing e-commerce payment pages

Laptop showing a blank online checkout form next to a payment card and a glass padlock, representing e-commerce payment page security
Script attacks on checkout pages are one of the most common causes of card data theft online.

Attackers increasingly steal card data by injecting malicious scripts into checkout pages, a technique often called digital skimming. PCI DSS v4.0.1 responds with requirement 6.4.3, which requires an inventory, authorisation and integrity checking of scripts on payment pages, and requirement 11.6.1, which requires a mechanism to detect unauthorised changes to payment pages. Both have applied since 31 March 2025.

In January 2025 the PCI Security Standards Council updated SAQ A for merchants that fully outsource payment pages: those two requirements were removed from SAQ A and replaced with an eligibility criterion that the merchant confirms its site is not susceptible to attacks from scripts that could affect its e-commerce systems. In practice, you still need to protect the pages that load or redirect to the payment form. We help you choose the right SAQ and put proportionate script controls in place.

Merchant levels and how you validate compliance

How you prove compliance depends on your transaction volume and the rules of the card brands and your acquirer. Larger merchants and service providers usually need an annual Report on Compliance from a QSA; smaller merchants usually complete a Self-Assessment Questionnaire. For example, Visa treats merchants processing more than six million transactions a year as Level 1. Your acquiring bank confirms which level and validation method applies to you.

Common SAQTypically suits
SAQ ACard-not-present merchants that fully outsource all payment pages to a PCI DSS compliant provider
SAQ A-EPE-commerce merchants whose website controls or affects the payment page, for example with direct post or JavaScript forms
SAQ B and B-IPMerchants using standalone or IP-connected payment terminals with no electronic card data storage
SAQ C and C-VTMerchants with payment application systems connected to the internet, or manual entry through a virtual terminal
SAQ P2PEMerchants using a validated point-to-point encryption solution
SAQ DAll other merchants, and all service providers eligible to self-assess

Recurring PCI DSS activities

  • Quarterly external vulnerability scans by an Approved Scanning Vendor (ASV), and quarterly internal scans
  • Internal and external penetration testing at least every twelve months and after significant changes
  • Segmentation testing to confirm the CDE is isolated
  • Confirmation of PCI DSS scope at least every twelve months (every six months for service providers)
  • Targeted risk analyses for requirements that allow flexible frequencies
  • Security awareness training, including phishing and social engineering
  • Review of logs, access rights and third-party service provider compliance

Why choose SSC for PCI DSS compliance

  • Scope-first advice that reduces cost and risk before any remediation starts.
  • Practical help with v4.0.1 changes, including payment page script controls, MFA into the CDE and targeted risk analysis.
  • We prepare you for the assessment and work alongside your QSA, keeping adviser and assessor roles separate.
  • One control set that also supports ISO/IEC 27001 and SOC 2, through our security compliance services.
  • PCI compliance support for clients in Sydney, Melbourne, Brisbane, Auckland and Wellington.

Further reading: PCI DSS v4 compliance guide, common PCI compliance challenges and payment security compliance in the age of AI. To scope your PCI DSS project, contact our team.
Achieve PCI DSS Compliance Today!

Ensure secure transactions, prevent data breaches, and maintain compliance with expert PCI DSS advisory services. Contact us today to get started!

Frequently asked questions

PCI DSS is not a law in either country, but it is mandatory under the agreements merchants and service providers have with the card brands, acquiring banks and payment providers. Non-compliance can lead to fines from your acquirer, higher fees or loss of the ability to accept cards.

PCI DSS v4.0.1. Version 4.0 was retired at the end of 2024, and the requirements that were future-dated in version 4.0 became mandatory on 31 March 2025.

It depends on how you accept cards. Merchants that fully outsource payment pages may qualify for SAQ A, e-commerce merchants that control part of the payment page usually need SAQ A-EP, and service providers use SAQ D. Your acquirer confirms the validation method, and we help you choose correctly.

It reduces your scope significantly but does not remove your obligations. You still need to validate compliance, usually with a shorter SAQ, and protect the website pages that load or redirect to the payment form.

For a merchant with a well-scoped environment, readiness for an SAQ can take a few weeks. Larger environments preparing for a QSA Report on Compliance typically need several months, depending on how much remediation is required.

A Qualified Security Assessor is certified by the PCI Security Standards Council to assess and report on compliance. SSC is your advisory partner: we scope, assess gaps, help remediate and prepare evidence, then work alongside your QSA during the assessment.

Yes. Any service provider that stores, processes or transmits card data, or can affect its security, such as hosting, payment or SaaS providers, needs to validate compliance, and its customers will usually ask for an Attestation of Compliance.