Our SOC 2 consulting helps SaaS and technology companies get ready for a SOC 2 Type 1 or Type 2 examination: scoping the system, choosing the Trust Services Criteria, designing controls auditors can test, and collecting evidence without stopping engineering. Security Solution Consultants (SSC) works with companies in Australia, New Zealand and the Middle East that need a SOC 2 report to win and keep customers, especially in North America.
SOC 2 is an attestation framework from the American Institute of Certified Public Accountants (AICPA). A licensed CPA firm examines your controls against the Trust Services Criteria and issues a report with an opinion. Security is always in scope; Availability, Processing Integrity, Confidentiality and Privacy are added when customers rely on them.
| Report | What it shows | Typical use |
|---|---|---|
| Type 1 | Controls are suitably designed at a point in time | A first report to unblock sales while Type 2 evidence builds |
| Type 2 | Controls operated effectively over a period, typically 3 to 12 months | The report most enterprise customers ask for |
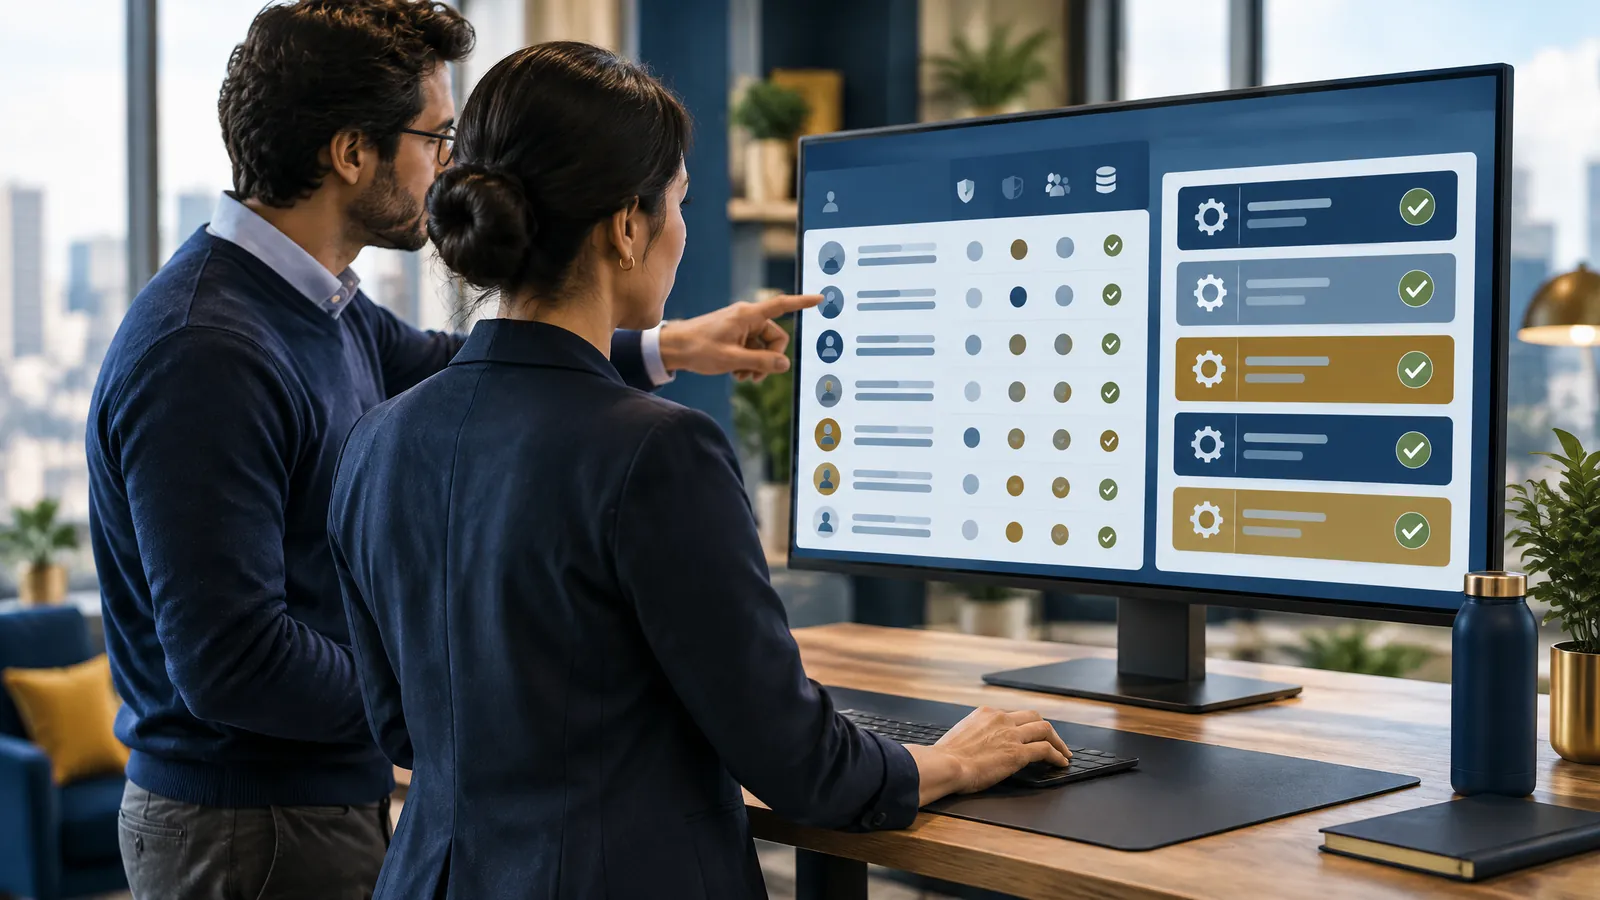
In a Type 2 examination the auditor samples instances across the observation period: access reviews, joiners and leavers, change approvals, backups, vulnerability fixes and incident tickets. Missing one instance can create an exception in the report. We set up evidence routines and, if you use it, the GRCLens SOC 2 module to track each control and its evidence so nothing is missed.
A clean SOC 2 report answers most of a customer’s security questionnaire in one document. We help you present it well, with a short bridge letter process between reports and a plan for the next observation period.
Related: security compliance services, SOC 2 training for your team, SOC 1, 2 and 3 explained and ISO 27001 certification.