Security Solution Consultants (SSC) provides cyber security compliance and consulting in Melbourne for organisations that supply the Victorian public sector, run critical infrastructure, operate under APRA or simply need to prove their security posture to customers, insurers and auditors. We are based in Tarneit, in Melbourne’s west, and work to the Australian and Victorian instruments that actually bind you, not a generic checklist.
The first job is usually working out what applies. Most organisations are subject to more than one obligation at once, and the cheapest way to comply is to evidence each control once and reuse it for every requirement that asks for it.
Which cyber security obligations apply to you in Victoria?
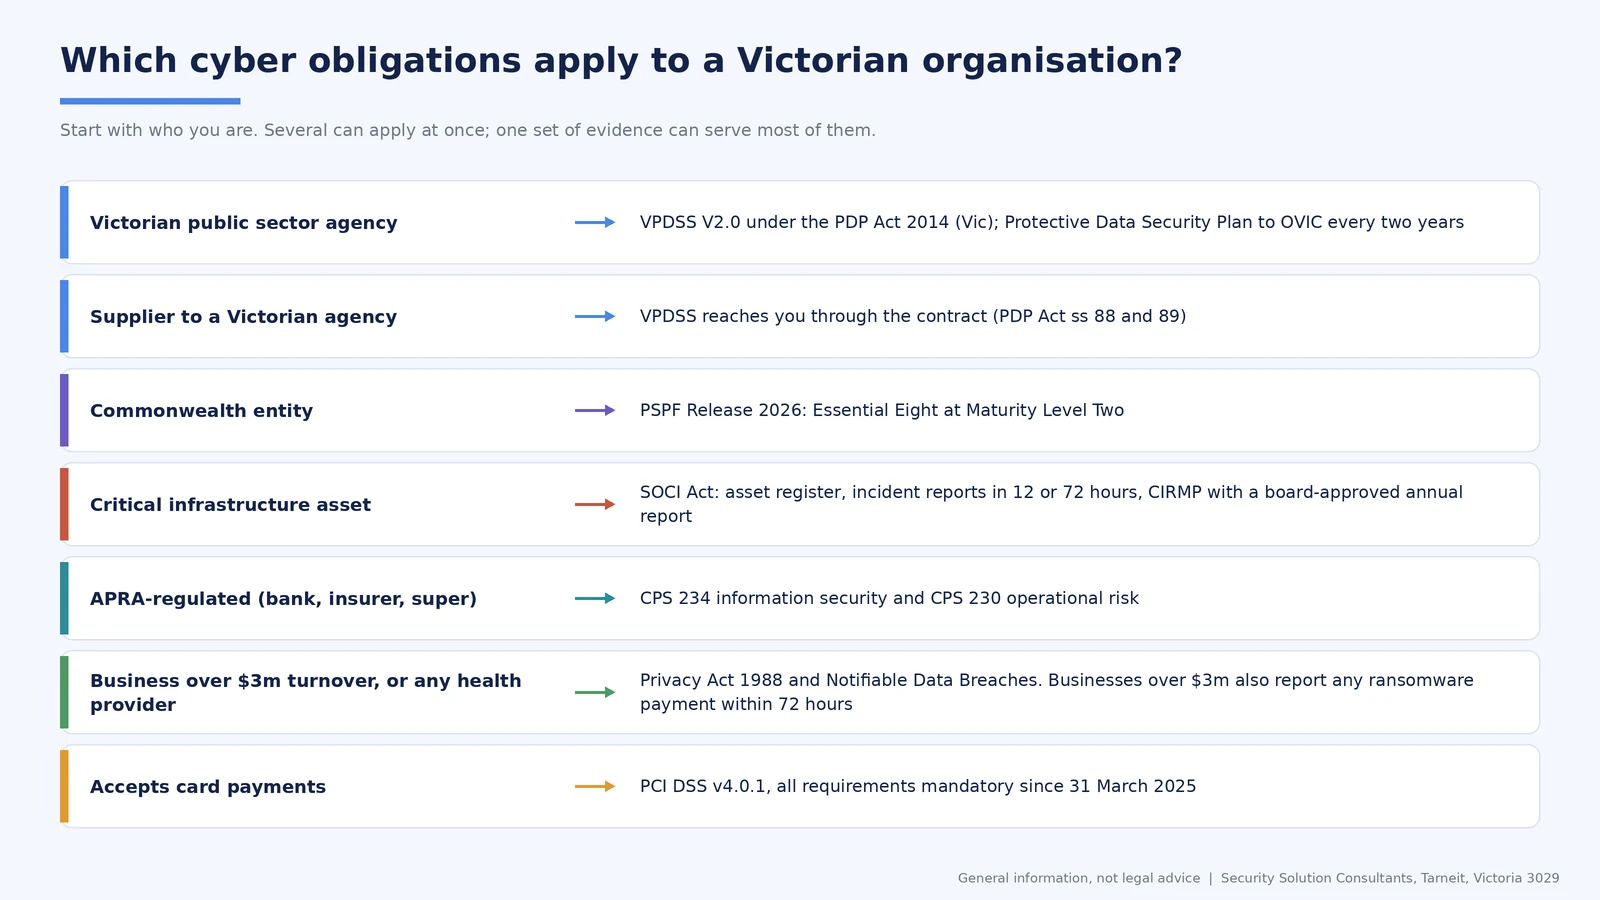
Victorian public sector and its suppliers. The Victorian Protective Data Security Standards (VPDSS V2.0) bind Victorian public sector agencies, which attest to OVIC through a Protective Data Security Plan every two years. The 2026 plans were due by 31 August 2026. Under sections 88 and 89 of the Privacy and Data Protection Act 2014 (Vic), agencies must also ensure their contracted service providers do not contravene the Standards, so an agency’s compliance problem becomes its supplier’s evidence problem.
Commonwealth entities and their suppliers. The Essential Eight is mandatory at Maturity Level Two for non-corporate Commonwealth entities under PSPF Release 2026, and routinely imposed on suppliers through procurement and contract terms.
Critical infrastructure. Responsible entities for water, energy, ports, freight, health, data storage and other critical infrastructure assets carry SOCI Act obligations: the asset register, cyber incident reporting within 12 or 72 hours, and a critical infrastructure risk management program with a board-approved annual report.
APRA-regulated entities. Banks, insurers and superannuation trustees, of which Melbourne has a large cluster, must meet CPS 234 for information security and CPS 230 for operational risk.
Everyone else with turnover above $3 million, and every health service provider. The Privacy Act 1988 and the Notifiable Data Breaches scheme apply. Businesses with turnover above $3 million must also report a ransomware payment within 72 hours under the Cyber Security Act 2024. If you accept card payments, PCI DSS v4.0.1 applies as well.
Our cyber security compliance services in Melbourne
- Compliance gap assessment. One review against every obligation that applies to you, with a single prioritised roadmap instead of one report per framework.
- Cyber security audits in Melbourne. Independent audits against the Essential Eight, ASD Essentials, ISO 27001, SOCI, VPDSS or a customer’s contract, with findings mapped clause by clause.
- Essential Eight assessment and the move to ASD Essentials. Maturity assessment against the Essential Eight, mapped to the new Essentials actions so existing investment carries forward.
- SOCI Act compliance advisory and CIRMP audit. Applicability, CIRMP design and uplift, readiness for the enhanced CIRMP rules and independent evidence for the board.
- VPDSS supplier assurance and PDSP support. We map your controls to the Standards, assemble the evidence pack agencies actually ask for, and support agencies with the security risk profile assessment and plan.
- ISO 27001 implementation and certification readiness. A management system that satisfies large parts of VPDSS, the Essential Eight and customer questionnaires at the same time.
- APRA CPS 234 and CPS 230 advisory. Control testing, material service provider management and operational resilience for Melbourne’s financial services sector.
- PCI DSS v4.0.1, enterprise risk management and business continuity. Risk registers, continuity plans and payment security that hold up under board and regulator scrutiny.
From the Essential Eight to ASD Essentials
On 15 October 2026 ASD published the ASD Essentials series, the evolution of the Essential Eight. Instead of eight strategies and one maturity level, it sets out principles, actions and domains in separate chapters for enterprise IT, operational technology and cloud, and reports posture by domain. Existing Essential Eight controls count where they achieve the outcome, but maturity levels do not convert. For Melbourne organisations the practical step now is a mapping: what your current Essential Eight evidence already covers, and where the new actions need work.
SOCI Act compliance for Victorian critical infrastructure
Victorian water corporations, energy networks, ports and freight operators run critical infrastructure risk management programs under the SOCI Act. For nine asset classes, the enhanced CIRMP rules that commenced on 10 June 2026 add obligations from around June 2027 and June 2028, including a framework uplift such as Essential Eight Maturity Level Two or AESCSF Security Profile 2, phishing-resistant multi-factor authentication and segregation of critical systems. Our SOCI compliance advisory sets out what applies when and builds the plan to get there.
GRCLens: evidence captured once, reused everywhere
Most compliance cost is duplicated effort. The same control gets evidenced separately for VPDSS, ISO 27001, the Essential Eight, a customer questionnaire and the board pack. GRCLens, our multi-framework GRC platform, maps every framework to one shared control model, so evidence captured once can satisfy several obligations at the same time. It already covers ASD Essentials, the Essential Eight, SOCI CIRMP and AESCSF, ISO 27001, APRA CPS 234 and CPS 230, and VPDSS.
Why Melbourne organisations choose Security Solution Consultants
- Based in Melbourne’s west, working to the actual Victorian instruments, VPDSS V2.0 and the PDP Act, not a national checklist with Victoria written on the cover.
- Consultants who deliver Essential Eight, ISO 27001, SOCI, CPS 230 and CPS 234 engagements as day-to-day work.
- One compliance platform built for evidence reuse, which is where the cost savings actually come from.
- Remote-first delivery with on-site workshops in Melbourne for the milestones that warrant being in the room.
- Fixed-scope engagements, with a defined deliverable and a defined price rather than an open retainer.
Penetration testing and security testing in Melbourne
Penetration testing in Melbourne is often driven by a contract rather than a choice. Victorian agencies must make sure their contracted service providers do not contravene the Victorian Protective Data Security Standards, so suppliers holding agency data are increasingly asked for a recent penetration test and evidence that the findings were fixed. Melbourne’s SaaS and fintech companies hear the same request from enterprise customers alongside a SOC 2 report or ISO 27001 certificate.
We run web application and API testing for those platforms, internal network testing for professional services firms and health providers, and passive OT assessments for Victorian water, energy and port operators working under the SOCI Act. For teams building their own software, a secure code review before release and a short threat modelling workshop at design time catch the flaws a point-in-time test can miss. Read more about our penetration testing and security testing services, or compare testing with an independent cyber security audit in Melbourne.
Frequently asked questions
What does cyber security compliance mean for a Melbourne business?
It means showing that the security controls a law, regulator, customer or contract requires are in place and working. For most Melbourne organisations that is some mix of the Essential Eight or ASD Essentials, ISO/IEC 27001, the Privacy Act 1988, and, depending on the sector, VPDSS, the SOCI Act, APRA CPS 234 or PCI DSS.
Does VPDSS apply to my private company?
Not directly. VPDSS binds Victorian public sector agencies and reaches you contractually. Under sections 88 and 89 of the Privacy and Data Protection Act 2014 (Vic) an agency must ensure its contracted service providers do not contravene a Standard, so the requirement arrives through your contract and the agency’s assurance process rather than through legislation aimed at you.
Is the Essential Eight still relevant now that ASD Essentials has been published?
Yes. ASD published the Essentials series on 15 October 2026 as the evolution of the Essential Eight, and existing Essential Eight controls carry forward where they achieve the outcome. Obligations that name the Essential Eight, such as PSPF Release 2026 for Commonwealth entities and some contracts, still name it until they are updated, so many organisations will report against both for a while.
Do you provide SOCI Act compliance advisory in Melbourne?
Yes. We help Victorian responsible entities confirm which obligations apply, build or uplift the critical infrastructure risk management program, prepare for the enhanced CIRMP rules and give directors independent evidence before they approve the annual report.
Does Victoria have a mandatory data breach notification scheme?
Not for private organisations. Their duty is the Commonwealth Notifiable Data Breaches scheme under the Privacy Act 1988. Victorian agencies are encouraged, but not required, to notify OVIC of BIL 2 or higher incidents within 30 days.
What does cyber security compliance consulting in Melbourne cost?
It depends on scope, and any firm quoting before understanding your environment is guessing. A VPDSS supplier evidence pack is a different exercise from an ISO 27001 certification program or a SOCI CIRMP audit. We scope to a fixed price after a short discovery call, so you know the number before you commit.
Do you work with organisations outside the Melbourne CBD?
Yes. We are based in Tarneit in Melbourne’s west and work across Victoria, including Geelong, Ballarat, Bendigo and the outer metropolitan corridors. Most delivery is remote, with on-site workshops, evidence walkthroughs and board sessions where they add value.
Get started
If you need cyber security compliance in Melbourne backed by people who work to the Victorian and Australian instruments every day, ask for a compliance gap assessment, a cyber security audit, a SOCI CIRMP review or a GRCLens demo. Contact us or email info@secsolutionshub.com. We also work with organisations in Sydney, Brisbane and across New Zealand.