
Security Solution Consultants (SSC) delivers cyber security services Adelaide organisations use to meet the SA Cyber Security Framework, enter Defence supply chains and answer customers who want ISO 27001 or SOC 2. We are based in Tarneit, Victoria 3029, work remote-first with South Australian clients, and come to Adelaide for workshops, physical and OT security reviews, data centre visits and findings walkthroughs.
South Australia does several things its own way. It has no privacy statute, it recommends rather than mandates an Essential Eight maturity level, and it places much of the supplier burden in guidelines and contract clauses rather than legislation. Getting the instruments right first saves money later.
Which rules apply in South Australia
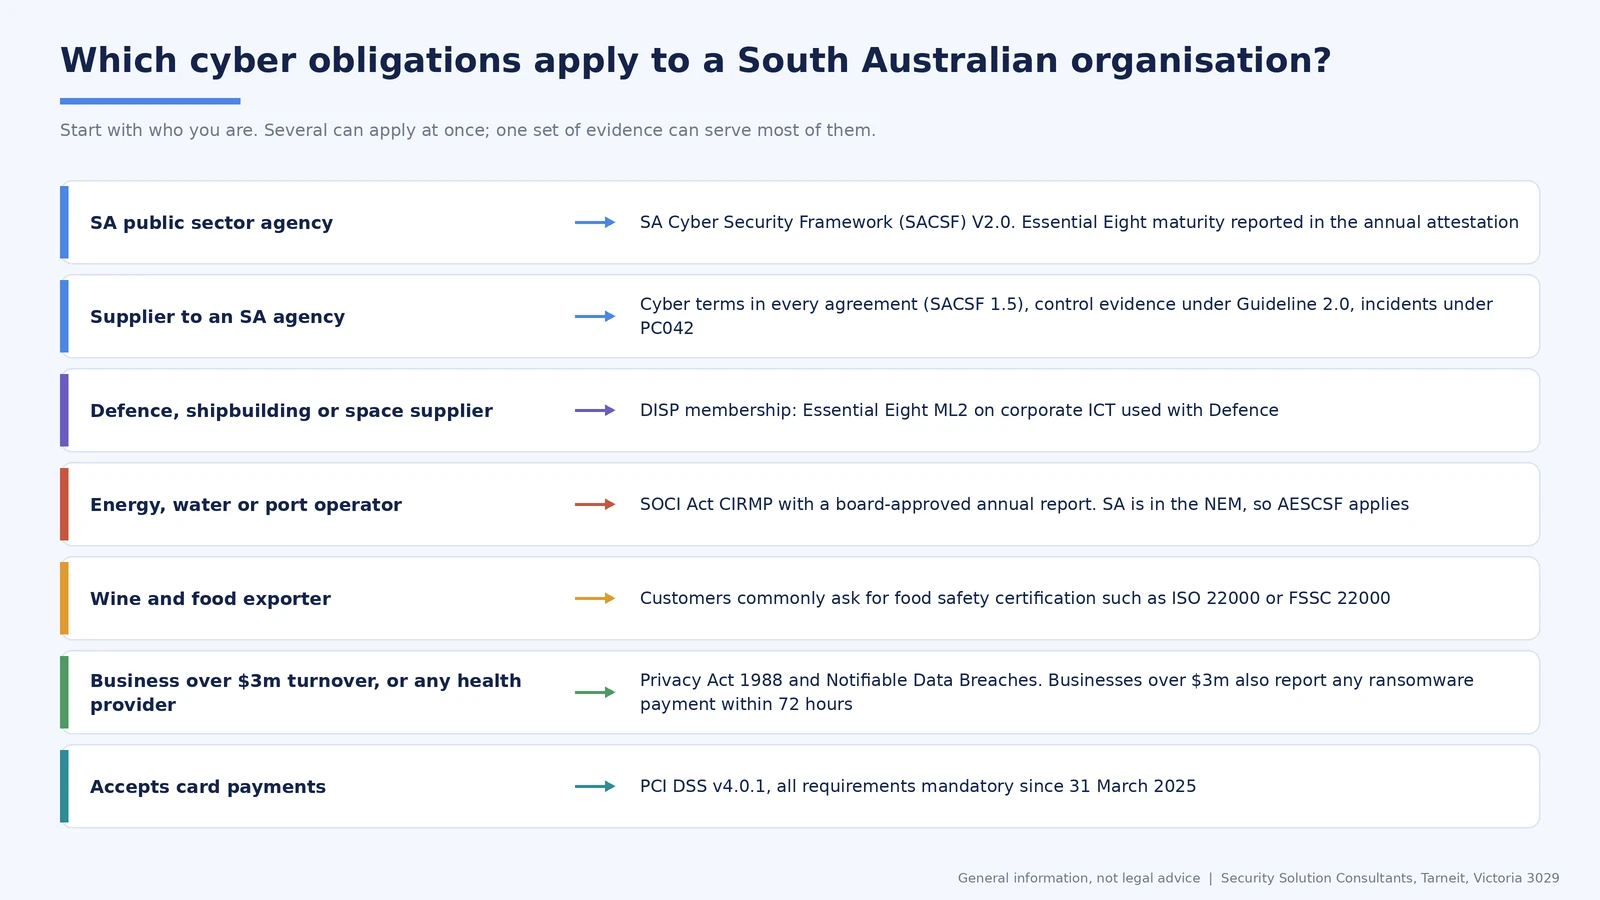
SA Government agencies. The SA Cyber Security Framework (SACSF) V2.0 was approved by Cabinet on 23 June 2025. Under Ruling 6, agencies had until 23 March 2026 to complete a gap analysis and either implement the framework or put a plan in place. The Cyber Security team in the Office of the Chief Information Officer, within the Department of Treasury and Finance, oversees it under the SA Government CISO, and the SA Cyber Security Strategy runs from 2025 to 2031. Guideline 9.0 (July 2025) sets no mandated Essential Eight level but recommends Maturity Level One as a minimum, reported in the annual attestation. SACSF 1.4 requires every agency to have a generative AI policy.
Suppliers to agencies. V2.0 removed the statement that the framework applies to suppliers, but the obligations still reach them. SACSF 1.5 requires cyber requirements in every agreement with a supplier that handles agency data, and Tier 3 agencies must obtain independent assurance from suppliers, cloud providers included. Guideline 2.0 expects suppliers to provide control evidence before and during the engagement and to report incidents, and Guideline 9.0 names ISO 27001 and SOC 2 as acceptable supplier assurance. Premier and Cabinet Circular PC042 (September 2024) requires suspected incidents to go to the SA Government Cyber Security Watch Desk, and it applies to organisations providing services to agencies.
Privacy. South Australia has no privacy statute. Agencies follow the Information Privacy Principles Instruction (PC012), and clause 5(A) requires their contracts to bind contracted service providers to those principles. Breach notification is administrative: under the Personal Information Data Breach Guideline, agencies notify the Privacy Committee, which received 225 notifications in 2024-25. Private businesses fall under the Commonwealth Privacy Act 1988 and its Notifiable Data Breaches scheme.
What the Audit Office keeps finding. The Audit Office of South Australia, which took that name on 1 July 2024, published its Review of legacy ICT systems (Report 3 of 2026) on 16 June 2026. It found incomplete asset inventories, few formal risk assessments and inconsistent reporting to governance committees. Its annual report (Report 7 of 2026, 13 October 2026) recorded 368 control findings, 166 of them repeats, and flagged legacy ICT as a continuing risk.
Critical infrastructure, payments and ransomware. SA electricity businesses sit in the NEM and use the AESCSF. SOCI Act obligations apply to responsible entities across the covered sectors, businesses over $3 million turnover must report ransomware payments within 72 hours under the Cyber Security Act 2024, and PCI DSS applies to anyone handling card data.
Certifications Adelaide businesses ask us about
- SOC 2 compliance in Adelaide. Because Guideline 9.0 names SOC 2 as acceptable supplier assurance, Adelaide software and cloud firms supplying agencies have a direct reason to obtain a report. Licensed CPA firms issue SOC 2 reports; we prepare you for the examination.
- ISO 27001 certification in Adelaide. The same guideline names ISO 27001, and ISO 27001:2022 can partly evidence the Defence Industry Security Program requirements. We implement the management system and prepare you for audit by an accredited certification body, the only kind of organisation that can certify you.
- ISO/IEC 42001. SA agencies must each have a generative AI policy under SACSF 1.4, and the state set up an Office for AI in July 2024, funded with $28 million in the 2025-26 Budget. Suppliers offering AI features to government can expect questions about how they govern them, and ISO 42001 gives a recognised structure for the answer.
- ISO 9001. Manufacturers and engineering firms tendering into the submarine and frigate programs, or into state infrastructure work, are commonly asked for certified quality management. We build ISO 9001 so it shares documentation with ISO 27001 where both are needed.
- ISO 22000. South Australia shipped 69% of Australia’s wine exports by value in the 12 months to March 2025, $1.906 billion of $2.76 billion, and primary industries earned $16.3 billion in 2024-25. Export buyers commonly ask wineries, food processors and ingredient suppliers for ISO 22000 or FSSC 22000.
- Critical infrastructure (SOCI Act). Electricity, gas, water, port and defence industry businesses with critical assets need a risk management program, covered below.
Critical infrastructure in South Australia
South Australia is part of the National Electricity Market, so its generators, networks and retailers assess their cyber maturity with AEMO’s AESCSF. The state also has its own Critical Infrastructure Resilience Strategy 2023 to 2026. Under the Commonwealth SOCI Act, responsible entities must maintain a critical infrastructure risk management program and give a board-approved annual report by 28 September. The enhanced CIRMP rules commenced on 10 June 2026, with some items deferred by 12 or 24 month grace periods, so the next two reporting cycles will ask more of SA operators than the last.
Suppliers feel this too. A CIRMP must address supply chain hazards, so maintenance contractors, software vendors and managed service providers to SA utilities are commonly asked for evidence of their own controls. We support both sides through SOCI Act compliance and CIRMP audits, energy sector security assessments and OT security training for critical infrastructure teams.
Our services in Adelaide
- SACSF gap analysis and attestation support. For agencies completing or acting on the Ruling 6 gap analysis and preparing the annual attestation.
- Supplier evidence under Guideline 2.0. A control evidence pack you can give an agency before and during an engagement, plus Watch Desk reporting arrangements under PC042.
- Cyber security audits in Adelaide. Independent audits against the SACSF, the Essential Eight, ISO 27001 or DISP requirements.
- Essential 8 compliance in Adelaide. Assessment at Maturity Level One for attestation or Level Two for Defence work, mapped to ASD Essentials.
- ISO 27001 implementation and SOC 2 readiness. The two assurance routes Guideline 9.0 names.
- DISP readiness. Gap assessment across governance, personnel, physical and ICT security, with uplift to Essential Eight Maturity Level Two. See also our security certification and accreditation services.
- PCI compliance in Adelaide. PCI DSS v4.0.1 readiness for retailers, hospitality groups and payment service providers.
- Maturity assessment and uplift. Including legacy system risk assessments of the kind the Audit Office found missing.
Defence and space supply chains
Adelaide’s defence work runs on a long horizon. The SSN-AUKUS submarines will be built at Osborne by a joint venture of ASC and BAE Systems, with Hunter class frigate work alongside, and the Australian Space Agency has had its headquarters at Lot Fourteen since 2020. Each draws small and medium firms into supply chains that expect formal security.
For Defence work that means the Defence Industry Security Program. DISP has an Entry level and Levels 1, 2 and 3, aligned to PROTECTED, SECRET and TOP SECRET, and it covers governance, personnel, physical and ICT and cyber security. Members must meet Essential Eight Maturity Level Two on corporate ICT used with Defence, a step above the Level One that SA agencies are encouraged to reach. ISO 27001:2022 can partly evidence those requirements.
Defence decides membership; our role is readiness. We run the gap assessment, help write the security policies and plans DISP expects, uplift Essential Eight controls, and review physical security on site at your Adelaide premises. Space and defence technology firms can pair this with ISO 27001 so one body of evidence serves both government and commercial customers.
From the Essential Eight to ASD Essentials in SA
ASD released the ASD Essentials series on 15 October 2026, covering enterprise IT, cloud and operational technology, along with guidance on transitioning from the Essential Eight. SA agencies still report Essential Eight maturity in their Guideline 9.0 attestation, and DISP still names Maturity Level Two, so both continue to apply until those documents change. We assess against the maturity model you report on today and map each result to the Essentials actions, so the transition does not mean starting again.
GRCLens for South Australian compliance
GRCLens, our GRC platform, maps frameworks such as ISO 27001, the Essential Eight and SOCI CIRMP to one shared control set. Evidence is captured once and reported many times, whether the request comes from an agency, a prime contractor or your own board.
For a one-off independent view rather than ongoing advice, see our cyber security audit services in Adelaide.
Penetration testing and security testing in Adelaide
Adelaide’s defence, naval shipbuilding and space supply chains are asked to prove their controls, not just describe them. DISP members must meet the Essential Eight at Maturity Level Two on the corporate ICT they use with Defence, and a penetration test is the most direct way to check that those mitigations hold up against an attacker. South Australian agencies also expect control evidence from suppliers under SACSF Guideline 2.0.
Penetration testing in Adelaide often focuses on internet-facing services, remote access, Active Directory and the cloud tenancies smaller suppliers depend on. The Audit Office of South Australia’s June 2026 review of legacy ICT systems is a reminder that older applications need testing too, and we scope those carefully to avoid disruption. For software and space technology teams, secure code review and threat modelling build security into the design, and phishing simulations test the human layer. Read more about our penetration testing and security testing services, or see cyber security audits in Adelaide.
Frequently asked questions
Do SA Government suppliers have to comply with the SACSF?
Not as a framework. Version 2.0 removed the statement that it applies to suppliers. The requirements arrive another way: SACSF 1.5 puts cyber clauses into every agreement with a supplier handling agency data, Guideline 2.0 asks for control evidence before and during the engagement, and PC042 requires service providers to report suspected incidents to the SA Government Cyber Security Watch Desk. Your contract is the place to look.
Will an agency accept our ISO 27001 certificate or SOC 2 report as assurance?
Guideline 9.0 names both ISO 27001 and SOC 2 as acceptable supplier assurance, which makes either a strong starting point. Check that the certificate scope or report boundary covers the service you actually provide to the agency. Tier 3 agencies must obtain independent assurance from their suppliers, including cloud providers, so a narrow scope may still leave questions to answer.
What Essential Eight maturity level suits an Adelaide business?
It depends on who is asking. SA agencies are encouraged to reach Maturity Level One at minimum and report it in their annual attestation. Defence Industry Security Program members must meet Maturity Level Two on corporate ICT used with Defence. A private customer’s contract may name its own target. We assess against the level that matters to your buyers and map it to ASD Essentials.
How is personal information protected in SA without a privacy act?
Through an administrative instruction. Agencies follow the Information Privacy Principles Instruction, PC012, and clause 5(A) requires their contracts to bind contracted service providers to the principles. Breaches are reported to the Privacy Committee under the Personal Information Data Breach Guideline, and it received 225 notifications in 2024-25. Private businesses are covered by the Commonwealth Privacy Act 1988 instead.
Can SSC get us DISP membership?
Defence grants DISP membership, not consultants. We prepare you for the application: a gap assessment across the governance, personnel, physical and ICT and cyber domains, the policies and plans you will need, and uplift to Essential Eight Maturity Level Two on the corporate ICT you use with Defence. Where you already hold ISO 27001:2022, we show how it partly evidences the requirements.
Should a Barossa or McLaren Vale winery consider ISO 22000?
If your export buyers ask for it, yes. South Australia accounted for 69% of Australian wine exports by value in the 12 months to March 2025, and overseas buyers commonly ask for ISO 22000 or FSSC 22000. We build the food safety management system with the records controls behind it, and can combine it with ISO 9001 where a buyer wants both.
Is your Adelaide work delivered on site or remotely?
Mostly remotely, from our base in Tarneit, Victoria. Document review, workshops by video, control testing and reporting all work well at a distance. We come to Adelaide and regional South Australia for physical security reviews under DISP, operational technology sites, data centres, and the findings walkthrough with your leadership team.
Next step
Tell us whether the driver is an agency contract, a Defence prime, an export buyer or your board, and we will scope a fixed-price engagement around it. Contact us or email info@secsolutionshub.com. We also support organisations in Melbourne, Perth and Hobart.

