
Security Solution Consultants (SSC) scopes every cyber security audit Adelaide clients commission around the instrument that triggered it: the SA Cyber Security Framework, a Guideline 2.0 evidence request, DISP, ISO 27001, the SOCI Act or a customer’s contract. We are based in Tarneit, in Melbourne’s west, carry out most fieldwork remotely, and visit Adelaide when physical security, operational technology or a findings walkthrough calls for it.
This page explains who in South Australia is commissioning audits, how ours run, which standard fits which situation, and what you can expect to receive.
Who in Adelaide is asking for audits
Agencies working through SACSF V2.0. Ruling 6 required a gap analysis and an implementation plan by 23 March 2026. Agencies are now delivering those plans, and an independent check of progress before the annual attestation is a natural next step.
Agencies the Audit Office is watching. Report 7 of 2026 recorded 368 control findings, 166 of which had been raised before, and named legacy ICT as a continuing risk. The June 2026 legacy ICT review found incomplete asset inventories and few formal risk assessments. Both are problems an internal audit can surface and fix before the Audit Office returns.
Suppliers asked for evidence. Tier 3 agencies must obtain independent assurance from their suppliers, including cloud providers, and Guideline 2.0 expects control evidence before and during an engagement. An independent audit report answers the request once instead of questionnaire by questionnaire.
Defence and space suppliers. Firms entering the SSN-AUKUS and Hunter class supply chains at Osborne want to know where they stand against DISP before they apply, and particularly whether their corporate ICT meets Essential Eight Maturity Level Two.
Health providers. The patient data breach at St Andrew’s Hospital in October 2026 gives Adelaide’s private health sector a close-to-home reason to check access controls, third-party connections and incident response.
Audit, assessment or penetration test: which do you need?
An audit compares what you do with what a document says you must do. The document might be the SACSF, ISO 27001 or a Defence requirement, and the output is a set of findings against named clauses that a customer or board can rely on. A technical assessment sets the document aside and examines the systems themselves: configurations, exposed services, patch levels, identity settings. Its output is a risk-ranked list of weaknesses. A penetration test is narrower again, a time-boxed attempt to break in through a defined target. Agencies and Defence ask for the first. The second and third tell you how hard you are to attack, which is useful but answers a different question. Many engagements combine an audit with targeted technical checks. If a penetration test is what you need, see our penetration testing and security testing services.
How an Adelaide audit runs
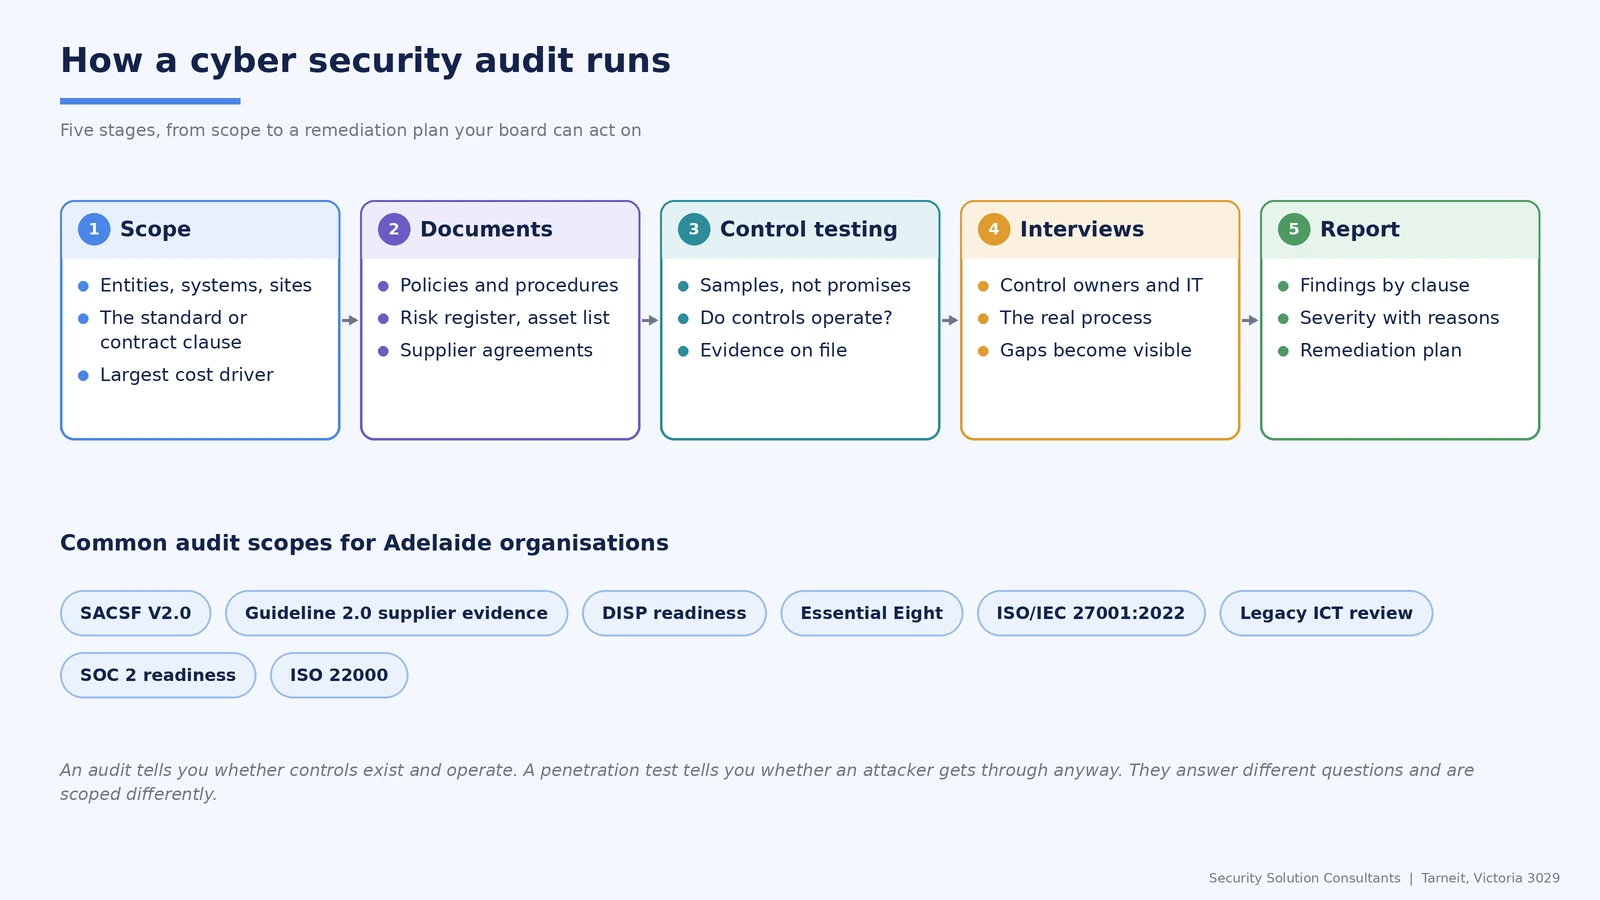
Scope. Entities, systems, sites and the standard, agreed in writing. For agency suppliers the scope follows the agency’s contract clause; for DISP, the four security domains.
Documents. We read the policies, asset inventory, risk assessments, incident procedures and supplier agreements. Given the Audit Office’s findings, we pay particular attention to whether the asset inventory is complete and whether legacy systems have formal risk assessments.
Control testing. Sampling evidence that controls work in practice: user access reviews, MFA, patching, backups, logging and alerting, and Essential Eight configuration.
Interviews. Conversations with the people who run the controls, including outsourced IT, to compare the written process with the real one.
Report. Rated findings mapped to the standard, an executive summary, a remediation plan and a walkthrough.
Standards we audit against in South Australia
- SACSF V2.0. Agency gap analysis under Ruling 6, progress against the implementation plan, and preparation for the annual attestation.
- SACSF supplier evidence. Control evidence under Guideline 2.0, contract clauses under SACSF 1.5, and incident reporting to the Watch Desk under PC042.
- Essential Eight assessment in Adelaide. Maturity Level One for agency attestation under Guideline 9.0, Maturity Level Two for DISP, with mapping to ASD Essentials.
- DISP readiness in Adelaide. Governance, personnel, physical and ICT and cyber security, tested against your target DISP level.
- ISO 27001 internal audit. The audit the standard requires, or a readiness review before the certification body’s stage one audit.
- SOC 2 readiness. A pre-examination review against the trust services criteria before a licensed CPA firm begins.
- SOCI CIRMP and AESCSF. For NEM participants and other responsible entities, ahead of the board report due by 28 September.
- Information Privacy Principles. Controls for contracted service providers bound by PC012 through clause 5(A).
- ISO 9001 and ISO 22000 internal audits. For defence manufacturers and for wine and food exporters whose buyers ask for certified systems.
What you get, how long it takes, what it costs
Deliverables. A short executive summary, a findings register with each item mapped to its clause and rated by risk, a remediation roadmap, and a session to walk through the results. Findings can be loaded into GRCLens so progress is tracked against the same controls at the next attestation.
Duration. A single organisation with a contained scope usually needs a few days of fieldwork, with the report following soon after. DISP readiness across four domains, multi-site groups and OT environments take longer. Prompt evidence is what keeps an audit on schedule.
Price. Fixed, after a scoping call. Scope drives cost far more than headcount, so confining the audit to the systems your agency or prime contractor actually cares about is the main lever. Certification audits and SOC 2 examinations are separate engagements with an accredited certification body or a CPA firm.
South Australian specifics that change the scope
Legacy systems. The Audit Office has flagged legacy ICT twice in 2026. If your organisation runs older finance, case management or operational systems, the scope should include an asset inventory check and a formal risk assessment for each legacy system.
The Watch Desk. PC042 requires organisations providing services to agencies to report suspected incidents to the SA Government Cyber Security Watch Desk. We test whether your incident procedure names it, and whether staff would recognise a suspected incident early enough to report it.
Privacy by contract. Because South Australia has no privacy statute, a supplier’s privacy duties come from clause 5(A) of PC012 and the contract itself. Agencies notify the Privacy Committee of breaches, so the audit checks how quickly you could tell the agency for it to do so.
Audits across South Australia
Remote fieldwork means the method is the same in the Adelaide CBD, at Osborne and Port Adelaide, in Mount Barker and the Adelaide Hills, across the Barossa, Clare and McLaren Vale wine regions, and in Whyalla, Port Augusta, the Riverland and Mount Gambier. We travel when the scope involves plant, physical security or OT. For ongoing compliance and certification support, see our cyber security services for Adelaide and South Australia.
Frequently asked questions
What does a SACSF V2.0 gap analysis cover?
It compares an agency’s current controls with each SACSF V2.0 requirement and records where the agency meets, partly meets or misses it. Ruling 6 set 23 March 2026 as the date to complete the analysis and either implement or plan. We can perform a fresh analysis, validate one done internally, or test progress against the resulting plan before the annual attestation.
Will an agency accept your audit report as independent supplier assurance?
It often helps, but the agency decides. Tier 3 agencies must obtain independent assurance from suppliers, and Guideline 9.0 names ISO 27001 and SOC 2 as acceptable forms. Where you hold neither yet, an independent audit against the agency’s contract clauses gives it something concrete to review. Confirm with the agency what form of assurance it will accept before we scope the work.
How do you assess readiness for the Defence Industry Security Program?
We test your organisation against the DISP level you are targeting across governance, personnel, physical and ICT and cyber security. On the ICT side we assess Essential Eight Maturity Level Two on the corporate systems you use with Defence. You receive a gap list, a remediation plan and an evidence index you can draw on when applying. Defence makes the membership decision.
Can you assess legacy systems the way the Audit Office does?
We use the themes the Audit Office raised in its June 2026 legacy ICT review: whether the asset inventory is complete, whether each legacy system has a formal risk assessment, and whether risks reach governance committees consistently. We then test compensating controls such as segmentation, access restrictions and monitoring, and help you prioritise replacement or remediation.
Which Essential Eight level will our Adelaide audit use?
The one that applies to you. For SA agencies that is usually Maturity Level One, the recommended minimum reported in the annual attestation. For Defence suppliers it is Maturity Level Two. Private contracts sometimes name their own level. We can also map results to ASD Essentials, published on 15 October 2026, so you can see how today’s evidence carries forward.
Can a business in the Riverland or Mount Gambier be audited without a site visit?
Yes. Document review, configuration checks and interviews all run remotely, so most regional South Australian audits need no travel at all. A visit makes sense when the scope includes physical security, plant and operational technology, or when your leadership prefers to walk through the findings in person. Any travel is quoted separately.
Next step
Share the clause, ruling or request that prompted the audit and we will confirm the right type of work and a fixed price. Get in touch or email info@secsolutionshub.com.

