Cyber Security and GRC Consultants in Johannesburg

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

Security Solution Consultants (SSC) are cyber security consultants for Johannesburg organisations that need to meet POPIA, the Prudential Authority and FSCA Joint Standards, ISO 27001, PCI DSS and ISO 45001 without slowing the business down. We work with mining houses, banks, insurers, healthcare groups and technology companies across Sandton, Rosebank, Midrand and Pretoria, combining practical governance, risk and compliance (GRC) consulting with GRCLens, our own GRC platform.
Executives in a Sandton boardroom reviewing a cyber risk report with the Johannesburg skyline behind them, representing cyber security consultants in Johannesburg
Cyber risk is now a standing item on Johannesburg board agendas.

Why Johannesburg organisations are investing in cyber governance

South Africa was the African country most frequently targeted by ransomware operators in 2024, according to INTERPOL’s 2025 Africa Cyberthreat Assessment. The local numbers explain why boards are asking harder questions:

  • In Sophos’ 2026 ransomware survey of South African organisations, 63% of attacks encrypted data and the average recovery cost was about R17 million.
  • The Information Regulator has received more than 8,000 security compromise notifications under POPIA since July 2021, and its first R5 million fine (against the Department of Justice in 2023) followed lapsed security licences and an ignored enforcement notice.
  • SABRIC reported R2.4 billion in digital banking fraud losses across more than 110,000 incidents in 2025, with card fraud up 18%.

The obligations we help you meet

ObligationWho it applies toWhat it asks for
POPIA (Protection of Personal Information Act 4 of 2013)Every organisation that processes personal informationThe eight conditions for lawful processing, security safeguards (s 19), notifying the Information Regulator and affected people as soon as reasonably possible after a compromise (s 22), and a registered Information Officer
Joint Standard 2 of 2024, Cybersecurity and Cyber ResilienceBanks, insurers, market infrastructures, pension funds and other listed financial institutions, from 1 June 2025A board approved cyber strategy, hygiene controls, regular testing, incident response, and notice of material incidents within 24 hours (Joint Notice 2 of 2026)
Joint Standard 1 of 2023, IT Governance and Risk ManagementThe same financial institutions, from 15 November 2024Board accountability for IT risk, IT risk management, service and project management frameworks
King IV Principle 12JSE listed companies (apply and explain)The board governs technology and information so it supports the organisation’s objectives
Mine Health and Safety Act 29 of 1996, with ISO 45001Mines and mining contractorsHazard identification, risk assessment and a safety management system; ISO 45001 is the common certifiable framework
PCI DSS v4.0.1Merchants, payment service providers and anyone storing, processing or transmitting card dataTwelve requirement areas; the future-dated requirements became mandatory on 31 March 2025

Mining and operational technology security

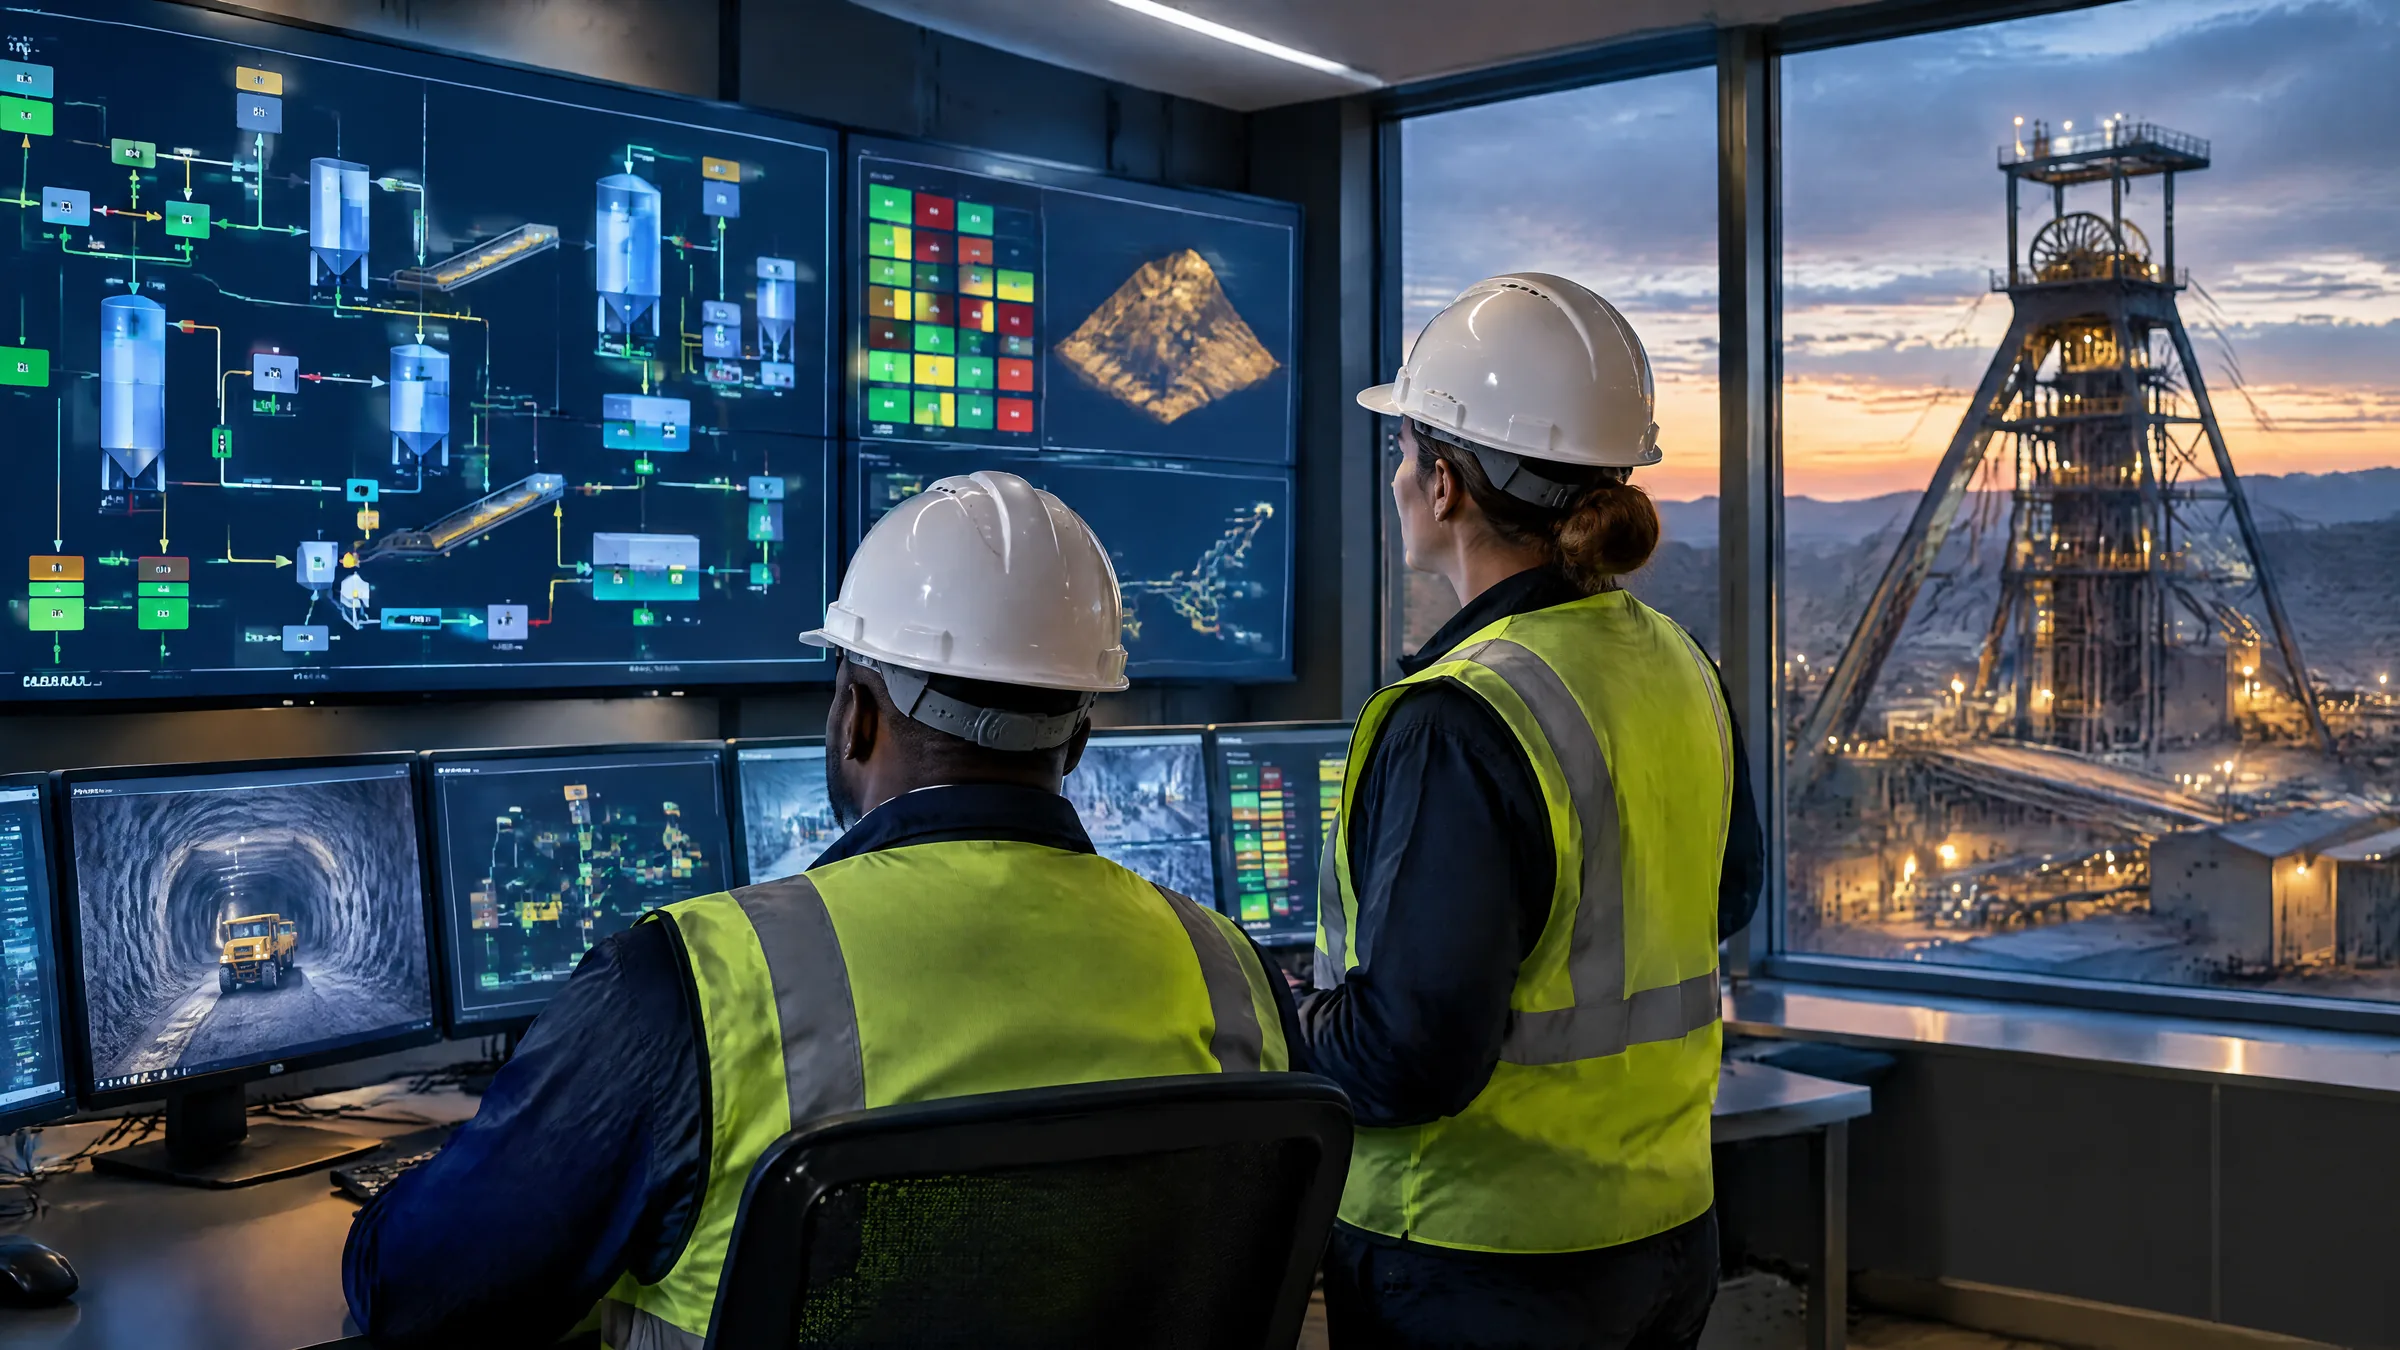
Engineers in hard hats watching wall displays in a deep-level mine operations control centre, representing operational technology security for South African mines
Hoisting, ventilation, pumping and processing now run on connected control systems.

When Sibanye-Stillwater was hit by a cyber attack in July 2024 it isolated its IT systems and later postponed its results. Mines in Gauteng and the platinum belt run hoisting, ventilation, pumping and processing plants on control systems that were never designed to face the internet, yet are now connected to corporate networks, vendors and remote support.

  • OT asset inventory and risk assessment across shafts, plants and smelters, including vendor remote access.
  • Segmentation and secure remote access designed with IEC 62443 zones and conduits, so an IT incident cannot reach the plant.
  • Incident playbooks for the plant floor that safety, engineering and IT can run together.
  • ISO 27001 scopes that include OT, so certification reflects how the mine actually operates.

See our operational technology and energy sector security assessments and critical infrastructure and OT security training. GRCLens includes an IEC 62443 module.
Work health and safety: ISO 45001 for mines and industry

A safety officer reviewing a checklist on a tablet with a mine worker at the surface of a South African platinum mine, representing ISO 45001 occupational health and safety
Safety management systems work when they reflect the work as it is really done.

Mining fatalities fell to a record low of 42 in 2024 and 41 in 2025, but 49 deaths had been recorded by mid September 2026, and the Minister has called for accountability across the industry. Mines answer to the Mine Health and Safety Act; most other workplaces to the Occupational Health and Safety Act 85 of 1993. ISO 45001, adopted in South Africa as SANS/ISO 45001, gives both a structure auditors and insurers recognise.

We run ISO 45001 gap assessments, hazard identification and risk assessment workshops, integrated management systems with ISO 14001 and ISO 9001, internal audits and certification readiness with a SANAS accredited certification body. Learn more about our ISO 9001, ISO 45001 and ISO 22000 consulting.
Banks, insurers and Joint Standard 2

Analysts at a bank security operations centre in Johannesburg at night, representing cyber resilience for South African banks and insurers
Joint Standard 2 turns cyber resilience into a supervised obligation.

Joint Standard 2 of 2024 requires an annual review of the cyber strategy, an annual independent review of the cybersecurity framework, a testing programme that includes at least annual penetration testing of internet facing systems, and remediation tracked to the board. From 1 September 2026, material incidents go to the Prudential Authority or FSCA within 24 hours of being classified, with an update within 14 days, and outsourcing does not move that duty to your provider.

We assess you against every paragraph of Joint Standards 1 and 2, design the testing and assurance programme, prepare board reporting, and support PCI DSS for card issuers, acquirers and payment providers. See our cyber security maturity assessments and PCI DSS compliance advisory.

POPIA compliance and ISO 27001 certification

A credible POPIA programme starts with a registered Information Officer, a personal information impact assessment and a compliance framework that is monitored, not just written. Section 19 then expects safeguards that are identified, implemented, regularly verified and updated, and section 21 makes you answerable for the security of your operators. Since April 2025 security compromises are reported through the Regulator’s eServices portal.

ISO 27001 is the most practical way to show your section 19 safeguards work. We design the scope, run the risk assessment and Statement of Applicability, prepare evidence and support you through Stage 1 and Stage 2 audits. Learn more about our ISO 27001 implementation and advisory, or see the GRCLens ISO 27001 module.

Healthcare and AI governance

The ransomware attack on the National Health Laboratory Service in June 2024 left about 6.3 million blood tests in a backlog. Health information is special personal information under POPIA, which allows processing only under the conditions in sections 26 to 32. We help hospital groups, laboratories, medical schemes and practices secure clinical systems and evidence their safeguards.

As Johannesburg organisations adopt AI, POPIA section 71 already limits decisions based solely on automated profiling. Our ISO 42001 consulting builds an AI management system that inventories AI use, assesses risk and impact, and keeps humans accountable.

GRCLens: one platform to run your GRC function

Consulting gets you compliant. GRCLens, the governance, risk and compliance platform we built and use on every engagement, keeps you compliant. It orchestrates your regulatory and legislative compliance in one place, so your risk, compliance and audit teams work from the same controls, evidence and numbers.
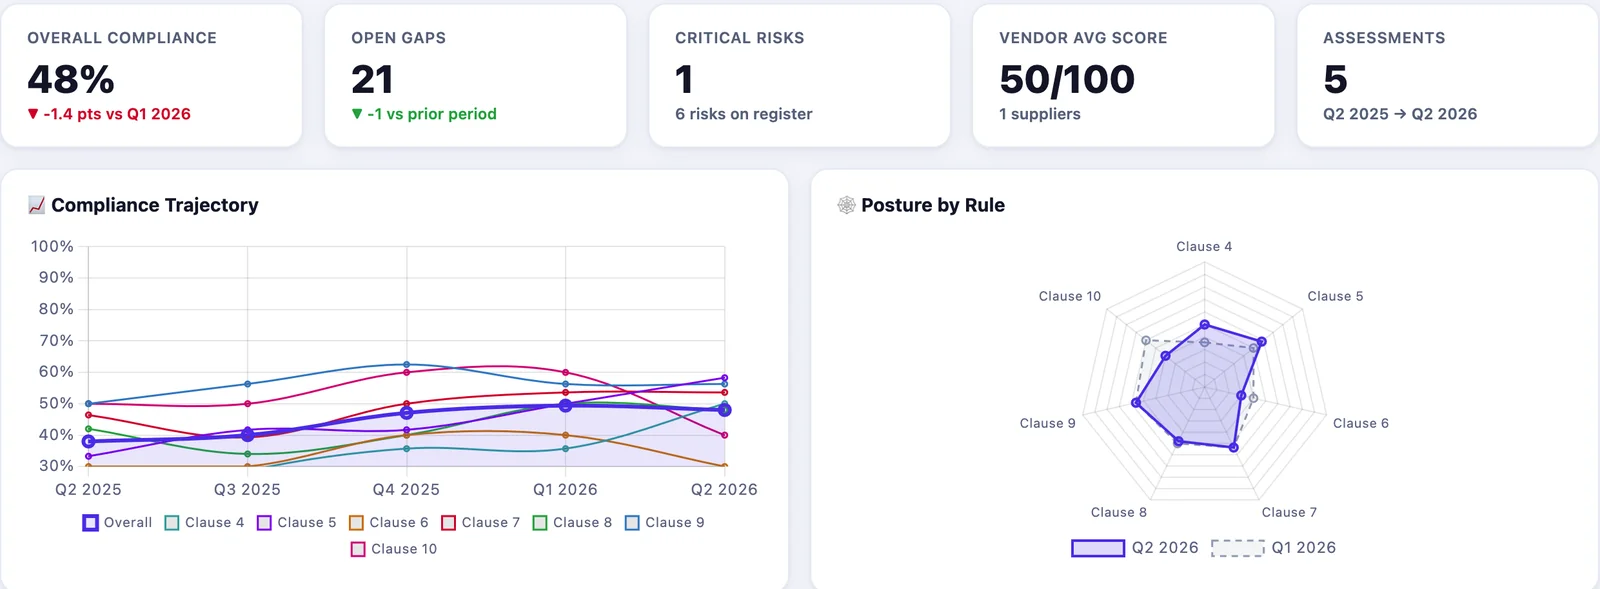
GRCLens board dashboard showing overall compliance, open gaps, critical risks, a compliance trajectory across five assessments and posture by clause
The GRCLens board view: compliance trend, open gaps, critical risks and posture by requirement.
  • Local law and international standards side by side. POPIA and Joint Standard 2 of 2024 sit in GRCLens next to ISO/IEC 27001, ISO/IEC 42001, ISO 45001, ISO 22000, PCI DSS, SOC 2 and IEC 62443, each with its own requirement catalogue.
  • Map once, comply many times. A shared control model reuses one piece of evidence against every obligation it satisfies, instead of collecting it again for each regulator.
  • Assurance built in. Every local framework carries an Assurance domain for audits, reviews and control monitoring, so you can show controls work, not just that they are documented.
  • Risks, indicators and suppliers. A risk register with key risk indicators traced to appetite, follow-up actions with owners and dates, and third-party assessments with vendor scores.
  • Board ready. Dashboards show the compliance trajectory, open gaps and critical risks, with an AI executive briefing and PDF and Word reports for the board and the regulator.
  • Hosted where your data must stay. GRCLens can run on premises in your own data centre or in a cloud region you choose.

See GRCLens for South Africa, or request a GRCLens demo.

How we work with organisations in Johannesburg

  • Remote first, on site when it matters. Our consultants run gap assessments, policy work, risk workshops and evidence reviews remotely, and we work with a local partner firm for on-site walkthroughs, interviews, audits and plant visits in Johannesburg.
  • One programme, many obligations. We map your controls once and reuse the evidence across local law, ISO standards, PCI DSS and your customers’ security questionnaires, instead of running a separate project for each.
  • Consulting and platform together. We configure GRCLens with your obligations, controls and evidence during the engagement, so your own team runs the programme after we hand over, with our consultants on call for audits and regulatory change.
  • Fixed scope, fixed quote. After a short scoping call you receive a written scope, timeline and price.

We also support organisations in Cape Town, Nairobi, Lusaka and Harare.
Frequently asked questions

We deliver most work remotely and use a local partner firm for on-site interviews, walkthroughs, audits and plant visits in Johannesburg, Sandton, Midrand and Pretoria, so you get specialist GRC expertise without paying for a large local team.

GRCLens is the governance, risk and compliance platform we built and use on every engagement. It holds your obligations, controls, evidence, risks and board reporting in one place. Many clients keep using it after the project to run their compliance programme, but our consulting does not depend on it.

It applies to banks, mutual banks, insurers, market infrastructures, pension funds, section 13B administrators, certain Category I financial services providers, over-the-counter derivative providers and credit rating agencies. It took effect on 1 June 2025.

Most mid-sized organisations are ready for the certification audit within four to nine months, depending on scope and how much is already in place. The certificate is issued by an accredited certification body, not by the consultant.

PCI DSS is a contractual requirement set by the card schemes and enforced by acquiring banks, not a statute. South African law separately expects payment systems to be sufficiently secure, so card data breaches also raise POPIA questions.

You must notify the Information Regulator and the affected people as soon as reasonably possible after you have reasonable grounds to believe personal information was accessed by an unauthorised person. Notifications are made through the Regulator's eServices portal.

Yes. Many of the same people, sites and risk registers are involved, so we plan the OT security assessment and the ISO 45001 programme together and share the governance, document control and internal audit.

Talk to us about cyber security in Johannesburg

Tell us where you are today and what you need to achieve. We will come back with a clear scope, timeline and fixed quote.