Cyber Security and GRC Consultants in Cape Town

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

Security Solution Consultants (SSC) are cyber security consultants for Cape Town organisations that need to protect customer data under POPIA, certify to ISO 27001, secure card payments under PCI DSS and govern their use of AI. We work with technology and fintech firms, insurers, healthcare providers, retailers and resources companies across the CBD, Century City, Woodstock and the Foreshore, combining hands-on GRC consulting with GRCLens, our own GRC platform.
A consulting team around a table in a Cape Town office with Table Mountain visible through the windows, representing cyber security consultants in Cape Town
Cape Town’s technology and financial sectors carry some of South Africa’s most sensitive data.

What Cape Town organisations are asking for

  • Proof for customers and investors. SaaS and fintech companies selling into Europe, the UK and the US are asked for ISO 27001 certificates and SOC 2 reports in almost every security review.
  • POPIA that stands up to the Regulator. The Information Regulator received 3,219 security compromise notifications in the year to March 2026, 1,858 of them from financial services, and it has said it wants the power to fine without a grace period.
  • Payment security. Card-not-present fraud made up 85.6% of gross credit card fraud losses in SABRIC’s 2024 statistics, which is why acquirers are tightening PCI DSS checks on online merchants.
  • Responsible AI. South Africa’s revised National AI Policy is expected to go to Cabinet in November 2026, and buyers already ask how AI products are governed.

The obligations we help you meet

ObligationWho it applies toWhat it asks for
POPIA and the 2018 Regulations (amended April 2025)Every organisation that processes personal informationAn Information Officer, a personal information impact assessment, security safeguards, operator contracts and security compromise notification
ISO/IEC 27001:2022Any organisation that wants independent proof of its information securityAn information security management system with risk based controls, internal audit and management review
PCI DSS v4.0.1Merchants and payment providers that handle card dataTwelve requirement areas, including the script and payment page controls in requirements 6.4.3 and 11.6.1
ISO/IEC 42001:2023 and POPIA s 71Organisations that build, buy or use AIAn AI management system, and no decisions with legal effect based solely on automated profiling unless an exception applies
Joint Standards 1 of 2023 and 2 of 2024Insurers, banks, pension funds and other listed financial institutionsIT governance, cyber resilience, testing and 24 hour notification of material incidents

AI governance with ISO 42001

A product and data science team in a Cape Town technology office looking at a large screen with an abstract neural network visualisation, representing AI governance and ISO 42001
Buyers now ask how AI features are governed, not just how they work.

Cape Town’s software and fintech companies ship AI features faster than their governance can keep up. ISO/IEC 42001 gives a certifiable way to show that AI is inventoried, risk assessed, tested and overseen by people. In August 2026 a South African customer experience provider announced what it described as the first local ISO 42001 certification in its sector, and procurement teams are starting to ask for the same.

We inventory your AI systems, run AI risk and impact assessments, align them with POPIA’s rules on automated decisions, and prepare you for certification. See our ISO 42001 consulting and the GRCLens ISO 42001 module.
Healthcare data protection

A doctor and a nurse reviewing a patient record on a tablet at a nurses' station in a Cape Town hospital, representing health information protection under POPIA
Health information is special personal information under POPIA.

South African healthcare organisations faced an average of 1,626 attacks a week in 2026, according to Check Point data reported in June 2026, and the National Health Laboratory Service ransomware attack in June 2024 showed how quickly clinical services stall when systems go down. Health information can be processed only under POPIA’s special personal information conditions, and HPCSA telehealth guidance adds consent and record keeping expectations.

We help hospitals, clinics, laboratories and medical schemes secure clinical systems, manage suppliers that host patient data, rehearse incident response and evidence their safeguards. Our incident response and recovery and data protection and encryption services support this work.
PCI DSS for merchants and payment providers

A customer tapping a contactless card on a payment terminal at a Cape Town cafe, representing PCI DSS compliance for South African merchants
Card-not-present fraud drives most card losses, so online checkouts get the most scrutiny.

PCI DSS is enforced by the card schemes and acquiring banks rather than by statute, but a card data breach is also a POPIA security compromise. Since 31 March 2025 the future-dated PCI DSS v4.0.1 requirements are mandatory, including control of every script on payment pages. In August 2026 the South African Reserve Bank took direct responsibility for payment system standards when PASA’s recognition ended.

We confirm your scope, help you choose the right Self-Assessment Questionnaire or prepare for a QSA assessment, close the gaps and keep evidence current. See our PCI DSS compliance advisory and the GRCLens PCI DSS module.

ISO 27001 and SOC 2 for technology companies

For a Cape Town SaaS company, one well designed control set can support ISO 27001 certification, a SOC 2 report for North American customers and your POPIA section 19 safeguards. We build that control set once, then map it to each requirement so evidence is collected once. Learn more about ISO 27001 implementation and SOC 2 readiness consulting.

GRCLens: one platform to run your GRC function

Consulting gets you compliant. GRCLens, the governance, risk and compliance platform we built and use on every engagement, keeps you compliant. It orchestrates your regulatory and legislative compliance in one place, so your risk, compliance and audit teams work from the same controls, evidence and numbers.
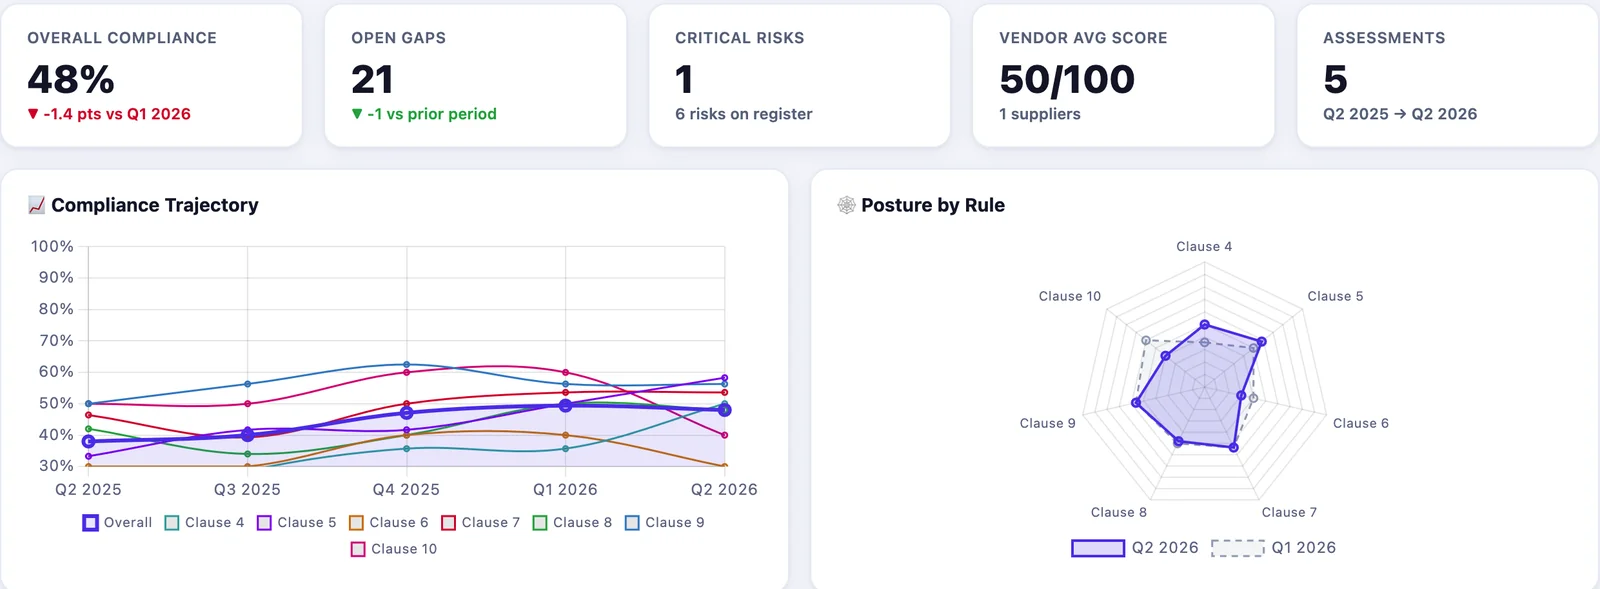
GRCLens board dashboard showing overall compliance, open gaps, critical risks, a compliance trajectory across five assessments and posture by clause
The GRCLens board view: compliance trend, open gaps, critical risks and posture by requirement.
  • Local law and international standards side by side. POPIA and Joint Standard 2 of 2024 sit in GRCLens next to ISO/IEC 27001, ISO/IEC 42001, ISO 45001, ISO 22000, PCI DSS, SOC 2 and IEC 62443, each with its own requirement catalogue.
  • Map once, comply many times. A shared control model reuses one piece of evidence against every obligation it satisfies, instead of collecting it again for each regulator.
  • Assurance built in. Every local framework carries an Assurance domain for audits, reviews and control monitoring, so you can show controls work, not just that they are documented.
  • Risks, indicators and suppliers. A risk register with key risk indicators traced to appetite, follow-up actions with owners and dates, and third-party assessments with vendor scores.
  • Board ready. Dashboards show the compliance trajectory, open gaps and critical risks, with an AI executive briefing and PDF and Word reports for the board and the regulator.
  • Hosted where your data must stay. GRCLens can run on premises in your own data centre or in a cloud region you choose.

See GRCLens for South Africa, or request a GRCLens demo.

How we work with organisations in Cape Town

  • Remote first, on site when it matters. Our consultants run gap assessments, policy work, risk workshops and evidence reviews remotely, and we work with a local partner firm for on-site walkthroughs, interviews, audits and plant visits in Cape Town.
  • One programme, many obligations. We map your controls once and reuse the evidence across local law, ISO standards, PCI DSS and your customers’ security questionnaires, instead of running a separate project for each.
  • Consulting and platform together. We configure GRCLens with your obligations, controls and evidence during the engagement, so your own team runs the programme after we hand over, with our consultants on call for audits and regulatory change.
  • Fixed scope, fixed quote. After a short scoping call you receive a written scope, timeline and price.

We also support organisations in Johannesburg, Nairobi, Lusaka and Harare.
Frequently asked questions

Yes. We deliver most work remotely and use a local partner firm for on-site workshops, interviews and audits in Cape Town and the wider Western Cape.

GRCLens is the governance, risk and compliance platform we built and use on every engagement. It holds your obligations, controls, evidence, risks and board reporting in one place. Many clients keep using it after the project to run their compliance programme, but our consulting does not depend on it.

Customers in South Africa, Europe and the UK usually ask for ISO 27001, while North American customers usually ask for SOC 2. Many companies need both, and one control set can support both.

Yes. Any AI system that processes personal information must meet POPIA's conditions, and section 71 limits decisions with legal or similar effect that are based solely on automated profiling.

Requirements 6.4.3 and 11.6.1, which became mandatory on 31 March 2025, require an inventory and authorisation of every script on payment pages and a way to detect unauthorised changes to those pages.

Information Officers are registered with the Information Regulator through its eServices portal. We help you appoint and register the Information Officer and any deputies, and set up the compliance framework they are responsible for.

Talk to us about cyber security in Cape Town

Tell us where you are today and what you need to achieve. We will come back with a clear scope, timeline and fixed quote.