Cyber Security Maturity Assessment and Uplift

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

A cyber security maturity assessment measures how well your organisation governs, protects, detects, responds to and recovers from cyber threats today, compares it with where you need to be, and gives you a prioritised plan to close the gap. Security Solution Consultants (SSC) runs independent cyber maturity assessments in Australia and New Zealand, and the uplift programs that follow, mapped to the frameworks your board, regulators and customers recognise.
Translucent glass steps ascending and glowing brighter towards the top, representing a cyber security maturity assessment and maturity levels
Maturity is measured in steps, and each step should reduce real risk.

A maturity assessment is different from a vulnerability scan or a penetration test. Those find technical weaknesses in specific systems. A maturity assessment looks at the whole security program: governance, people, processes and technology, and whether they work together consistently enough to manage risk.

Frameworks we assess against

FrameworkBest suited to
NIST Cybersecurity Framework (CSF) 2.0A widely recognised baseline for any organisation. Six functions, Govern, Identify, Protect, Detect, Respond and Recover, give boards a clear structure for reporting.
ASD Essential EightAustralian organisations, especially government entities and their suppliers. Maturity Levels One to Three across eight mitigation strategies.
ISO/IEC 27001:2022Organisations planning certification or wanting an internationally recognised management system.
CIS Critical Security ControlsTechnology teams wanting prioritised, practical safeguards grouped into Implementation Groups.
AESCSFAustralian electricity, gas and liquid fuel organisations, using Maturity Indicator Levels and Security Profiles.
NZ Protective Security Requirements and NZISMNew Zealand government agencies and their suppliers.
AU PSPF and the ISMAustralian Commonwealth entities and suppliers handling government information.

Many clients ask for more than one view. We assess once and map the results to each framework you need, so you are not paying for the same interviews and evidence review several times.
What a cyber security maturity assessment covers

  • Governance and risk: security strategy, policies, roles, risk management, board reporting and budget.
  • Identity and access: joiners, movers and leavers, privileged access, multi-factor authentication and access reviews.
  • Asset and vulnerability management: hardware, software and cloud inventories, patching timeframes and vulnerability remediation.
  • Data protection: classification, encryption, backups and data loss prevention.
  • Secure configuration: endpoints, servers, cloud platforms and network devices against agreed baselines.
  • Detection and response: logging, monitoring, incident response plans, exercises and lessons learned.
  • Third-party risk: how suppliers with access to your systems or data are assessed and monitored.
  • People and culture: awareness training, phishing resilience and how security is built into everyday work.
  • External attack surface: internet-facing assets and exposures, using our EASMLens platform to find what attackers can see.

How the assessment works

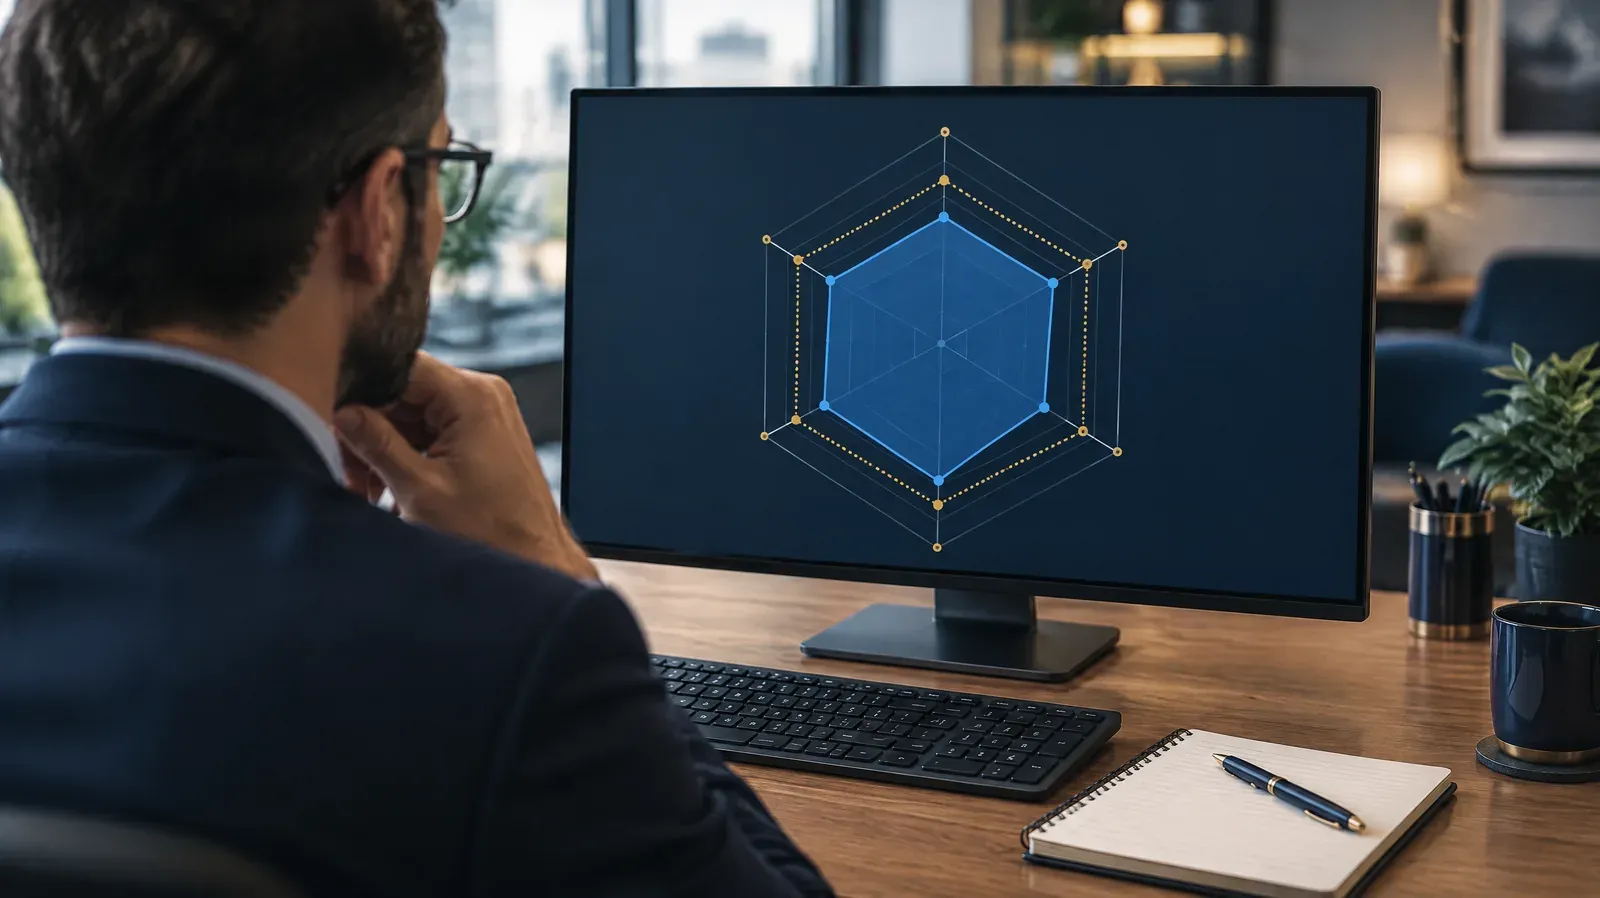
Consultant studying a radar chart comparing current and target cyber maturity on a monitor
We compare current maturity with a target state the board has agreed.
  1. Scope and target state. We agree the framework or frameworks, the parts of the organisation in scope, and the target maturity that matches your risk, obligations and budget.
  2. Evidence review. Policies, procedures, configuration exports, reports and registers are reviewed before interviews, so meetings focus on how things really work.
  3. Interviews and workshops. Short sessions with leadership, IT, security, HR, risk and key business owners.
  4. Technical sampling. Where useful, we test a sample of controls directly, for example MFA coverage, patch levels or backup restores.
  5. Scoring and validation. Each practice is rated against the framework’s maturity scale. We validate draft findings with you so there are no surprises in the final report.
  6. Report and roadmap. A board summary, detailed findings and a prioritised uplift roadmap with effort and cost ranges.

From assessment to uplift

Winding mountain road climbing towards a summit observatory at sunrise, representing a prioritised cyber security uplift roadmap
A clear roadmap turns findings into progress the board can track.

The assessment is only valuable if it leads to change. Our uplift roadmap groups recommendations into quick wins, foundational projects and longer-term improvements, sequenced by risk reduction and dependency rather than by framework clause. Each item has an owner, effort estimate and measure of success.

We then support the uplift itself: writing policies and standards, designing identity and access controls, setting up vulnerability management and logging, running incident response exercises, and preparing evidence for certification or regulator reviews. Related services include identity and access management, endpoint security management and incident response and recovery.

Cyber security maturity models and levels explained

Each framework uses its own scale, but they describe a similar journey. At the lowest levels, security depends on individuals: controls exist in places, but they are informal, inconsistent and undocumented. In the middle, controls are defined, documented and applied consistently, with clear owners. At the highest levels, controls are measured, monitored and improved, and security decisions are driven by risk and data. The Essential Eight is more specific: each maturity level sets out the implementation requirements an organisation must meet to mitigate increasingly capable adversaries.

The right target is rarely the highest level everywhere. We help you set a target that matches your threat environment, regulatory expectations and appetite, so investment goes where it reduces the most risk.

Common findings we see

  • Multi-factor authentication with gaps: enabled for email but not for remote access, administrators or key cloud services.
  • Patching without measurement: updates are applied, but nobody can say how many critical vulnerabilities are older than the agreed timeframe.
  • Untested backups: backups run nightly, but a full restore of a critical system has not been attempted.
  • Incomplete asset inventory: cloud services and internet-facing systems that IT does not know about.
  • Logging without monitoring: logs are collected but nobody reviews them, so incidents are discovered late.
  • Policies out of date: documents that describe how things were done several years and systems ago.

None of these require exotic technology to fix. They need clear ownership, a realistic plan and someone measuring progress, which is what an uplift program provides.

Reporting maturity to the board

Directors need to know three things: where we are, where we should be, and whether we are getting there. We give them a one-page maturity summary by domain, a small set of key risk indicators, and a quarterly progress view against the roadmap. Our guide to cyber risk KRIs for quarterly board reporting explains the indicators we typically recommend.

What you receive

  • An executive summary and board presentation
  • Current and target maturity scores by domain and by framework
  • Detailed findings with evidence references and risk ratings
  • A prioritised uplift roadmap with owners, effort and cost ranges
  • A framework mapping so one assessment supports several obligations
  • Optional quarterly re-scoring in GRCLens to track progress

Continuous maturity tracking with GRCLens

A point-in-time report starts to age the day it is delivered. GRCLens, the GRC platform built by SSC, keeps your maturity scores, findings, evidence and uplift actions in one place, so progress can be re-measured each quarter and reported to the board without starting again. It supports NIST CSF, the Essential Eight, ISO/IEC 27001, AESCSF, the NZ PSR and many more frameworks.

Who we work with

  • Boards and executives who want an independent view of cyber security posture
  • Organisations preparing for ISO/IEC 27001 certification or a regulator review
  • Government agencies and suppliers working to the Essential Eight, PSPF, PSR or NZISM
  • Energy and critical infrastructure operators working to AESCSF and the SOCI Act
  • Growing businesses whose security has grown faster than their governance

Further reading: cyber security maturity assessment guide, how to conduct a maturity assessment and Essential Eight maturity levels compared. To arrange an assessment, contact our team.
FAQs

An independent review of how consistently and effectively your organisation manages cyber security across governance, people, processes and technology, scored against a recognised framework and compared with a target maturity level.

It depends on your obligations and audience. NIST CSF 2.0 suits most organisations and board reporting, the Essential Eight is expected of many Australian government entities and suppliers, AESCSF applies to energy organisations, and ISO/IEC 27001 suits those planning certification. We can map one assessment to several.

A penetration test tries to exploit technical weaknesses in specific systems. A maturity assessment looks at the whole security program and how well controls are governed and operated across the organisation. They complement each other.

It depends on scope and size. For a mid-sized organisation assessed against one framework, evidence review, interviews and reporting usually take a few weeks. Larger or multi-framework assessments take longer.

A full assessment every one to two years is common, with lighter quarterly progress checks against the uplift roadmap. Reassess sooner after a major incident, merger or significant technology change.

An Essential Eight assessment is one type of maturity assessment, focused on eight specific mitigation strategies. Our broader maturity assessment can include the Essential Eight alongside other frameworks. See our dedicated Essential Eight compliance and assessment service for detail.