
Security Solution Consultants (SSC) are cyber security consultants Perth organisations bring in when a WA Government contract, a SOCI Act obligation or a customer’s security questionnaire asks them to prove their controls work. We are based in Tarneit, Victoria 3029, and work remote-first, coming on site in Perth and regional Western Australia when being in the room adds value: workshops, operational technology sites, physical security reviews, data centres and findings walkthroughs.
Most Perth engagements start by separating the WA and Commonwealth obligations that bind you directly from those that arrive through a contract. Then we build the evidence once and reuse it for every requirement that asks for it.
Which rules apply in Western Australia
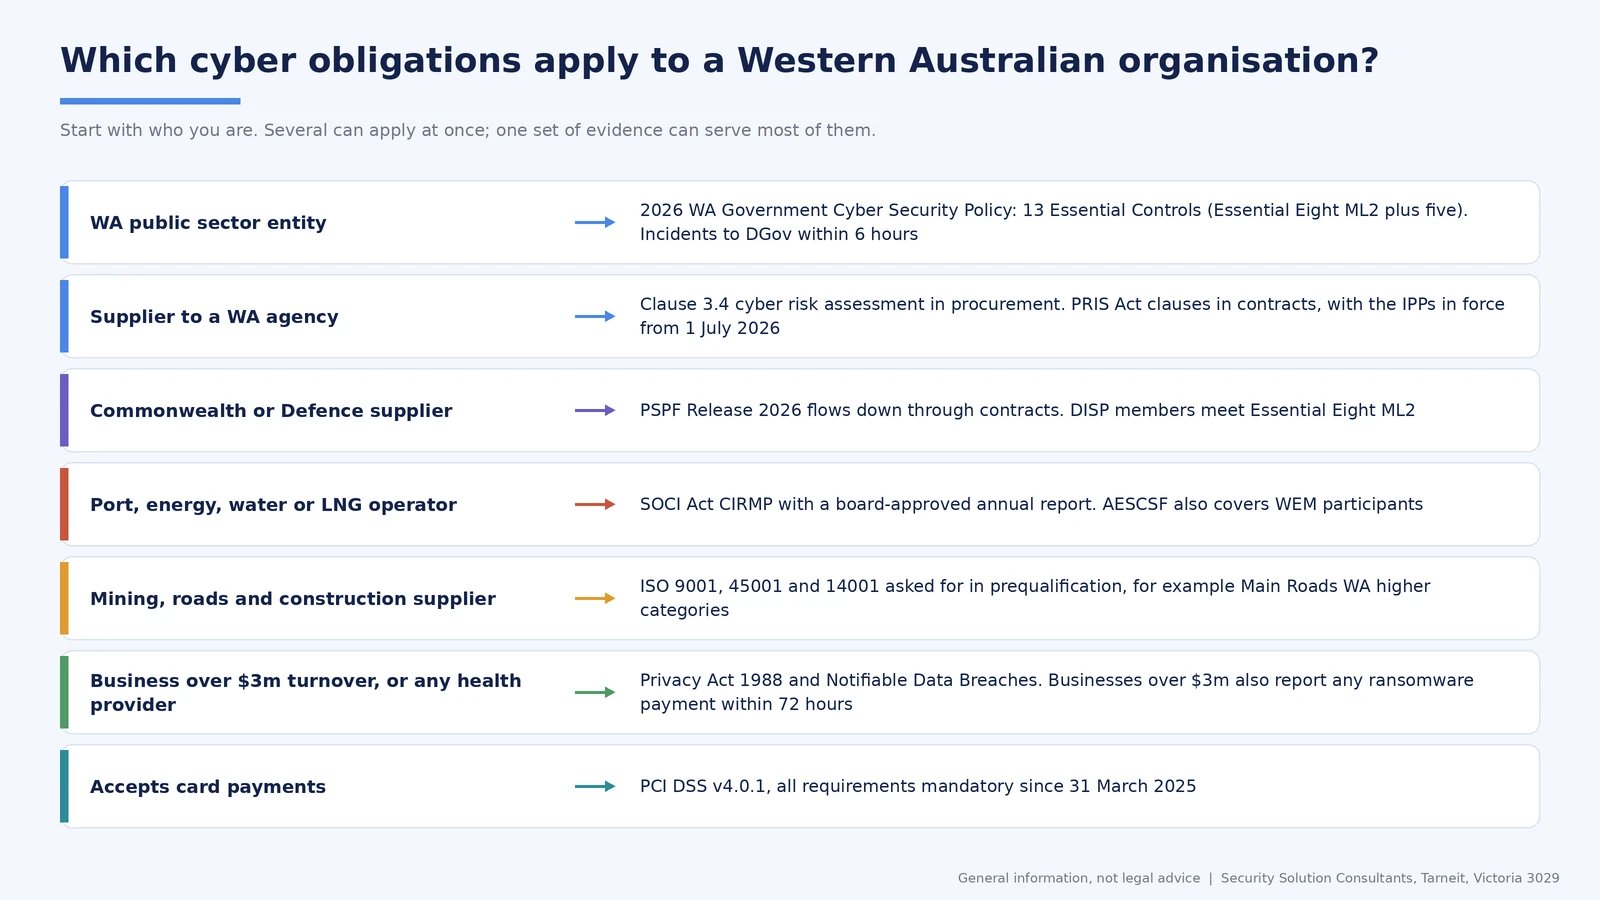
WA public sector entities. The 2026 WA Government Cyber Security Policy, version 2, was released in October 2026 and supersedes the 2024 Policy. Premier’s Circular 2025/13, effective 1 July 2025, makes the policy mandatory for Schedule 1 and Schedule 2 entities under the Public Sector Management Act 1994. Those entities must connect to the security operations centre run by the Office of Digital Government (DGov), report annually, and pass Office of the Auditor General letters to DGov within seven days. Local governments are encouraged to follow it. The Cyber Security Unit in DGov, within the Department of the Premier and Cabinet, oversees it.
What the policy demands. Its 13 Essential Controls combine the Essential Eight at Maturity Level Two with five further ASD mitigation strategies. Entities must have every Protect domain control in place by December 2028, legacy system transition plans by the end of 2027 and a post-quantum cryptography transition approach by December 2027. Incidents go to DGov within 6 hours, and confirmed incidents to the ACSC within 12 hours.
Privacy for agencies and their contractors. The Privacy and Responsible Information Sharing Act 2024 (PRIS Act) is phasing in: an Information Commissioner from 1 July 2025, eleven Information Privacy Principles from 1 July 2026, and mandatory breach notification from 1 January 2027. A contractor is bound only if its contract includes a PRIS clause (sections 129 to 130), the agency remains accountable for what its contractor does (section 140), and there is no small business carve out.
Private businesses. Outside government, Commonwealth rules apply: the Privacy Act 1988 and its Notifiable Data Breaches scheme, 72 hour ransomware payment reporting under the Cyber Security Act 2024 for businesses over $3 million turnover, the SOCI Act, and PCI DSS for card payments.
What the Auditor General keeps finding. The Office of the Auditor General’s State Government 2025: Information Systems Audit Results (Report 7: 2025-26, published 3 December 2025) raised 359 findings at 53 entities, down from 424 at 59 the year before. About two thirds were unresolved from earlier years, over 80% sat in the information and cyber categories, and fewer than a quarter of entities met the benchmark for access management and endpoint security. The office followed with a Microsoft 365 security controls report on 6 March 2026 and information systems results for universities and TAFEs on 22 May 2026.
Certifications Perth businesses ask us about
WA buyers, from agencies to resources companies, increasingly want a certificate or an independent report rather than a reassurance.
- SOC 2. Perth software, data and managed service firms selling to east coast or overseas customers are commonly asked for a SOC 2 Type 2 report. Only a licensed CPA firm can issue one; we prepare you, from scoping the trust services criteria to a readiness review.
- ISO/IEC 27001. Clause 3.4 of the WA policy asks agencies to weigh a supplier’s security maturity and certifications, and Tier 1 Risk procurements prefer IRAP or an equivalent industry certification. For many suppliers ISO 27001 is the practical choice. We build the management system and prepare you for the audit by an accredited certification body.
- ISO/IEC 42001. The 2026 policy added AI controls: only public, non-sensitive information may go into public AI tools, AI supply chain and offshoring risk must be managed, and inputs must be validated against prompt injection and data poisoning. Suppliers are also asked about AI security under clause 3.4. An AI management system built to ISO 42001 gives you a structured answer.
- ISO 9001. Main Roads WA prequalification asks for JAS-ANZ certified ISO 9001, ISO 45001 and ISO 14001 at higher categories. Mining services and engineering firms meet similar expectations: Rio Tinto alone spent A$10 billion with about 2,400 WA suppliers in 2024, and buyers in the resources sector commonly ask for certified quality systems.
- ISO 22000. WA food and beverage processors selling into supermarket and export channels are commonly asked for ISO 22000 or FSSC 22000. We set up the food safety management system and connect it to the information security controls that protect production, traceability and recall records.
- Critical infrastructure (SOCI Act). Energy, water and port operators, and the contractors who maintain their systems, need to evidence a critical infrastructure risk management program. The next section covers what that looks like in WA.
Critical infrastructure in Western Australia
Western Australia’s essential services are organised differently from the east coast. The state is not in the National Electricity Market: the South West Interconnected System runs the Wholesale Electricity Market (WEM), and AEMO’s AESCSF criticality tool covers WEM participants. Western Power, Synergy and Horizon Power operate on the electricity side, Water Corporation supplies water, and Fremantle Ports, Pilbara Ports and Southern Ports move the state’s trade. Pilbara Ports alone handled 775.7 million tonnes in 2024-25, part of a resources sector whose sales reached $220 billion that year, $36 billion of it LNG.
The Commonwealth SOCI Act applies to responsible entities in these sectors. The enhanced CIRMP rules commenced on 10 June 2026, with some items carrying 12 or 24 month grace periods, and each responsible entity still owes a board-approved annual report by 28 September. Two WA details help: the Cyber and Infrastructure Security Centre accepted the WA Government Cyber Security Policy (2024) as an equivalent framework for the CIRMP, and an AESCSF self-assessment may be submitted. A state-owned operator can often use one body of evidence for both obligations.
The November 2023 incident that suspended DP World’s terminals, Fremantle among them, showed how fast a cyber event at one operator becomes a supply problem for everyone downstream. We support operators and their suppliers through SOCI Act compliance and CIRMP audits and critical infrastructure and OT security training.
Defence is the other growing driver. Submarine Rotational Force-West will operate from HMAS Stirling from 2027, and together with the Henderson Defence Precinct that is drawing WA firms into Defence supply chains. Those firms meet the Defence Industry Security Program (DISP), whose members must hold Essential Eight Maturity Level Two on corporate ICT used with Defence. ISO 27001:2022 can partly evidence the requirement.
Our services in Perth
- WA policy gap assessment. A review against the 13 Essential Controls and the 2026 policy’s governance, reporting and AI requirements, with a plan that meets the December 2027 and December 2028 milestones.
- Essential Eight compliance in Perth. Maturity assessment at the level your policy or contract names, mapped to the new ASD Essentials actions.
- Supplier evidence packs for clause 3.4. The certifications, maturity statement, incident reporting arrangements and data handling answers agencies ask for, assembled once and kept current.
- ISO 27001 consultant support in Perth. Implementation, internal audit and certification readiness.
- PCI DSS compliance for Perth merchants and service providers. Readiness for v4.0.1 ahead of a QSA assessment or self-assessment questionnaire.
- SOCI Act advisory. CIRMP design, AESCSF assessments for WEM participants and independent evidence for the board.
- Incident response readiness. Playbooks and exercises built around the six hour DGov reporting clock.
- Enterprise risk management, business continuity and training. For remote sites, long supply lines and the teams who run them.
Supplying a WA agency under clause 3.4
Clause 3.4 of the 2026 policy requires an agency to run a cyber risk assessment for any procurement where the supplier will access its data or systems. The assessment looks at the supplier’s security maturity and certifications, whether it can support 6 hour incident reporting, how it secures AI, whether it holds cyber insurance, its exposure to foreign ownership, control or influence (FOCI), and how data is returned at the end of the contract.
Clause 3.5 draws a hard line: Tier 1 Risk information must not be offshored. For a Perth SaaS or managed service provider, that means knowing exactly where data is stored, backed up and supported from, including any follow-the-sun help desk and the subprocessors in your cloud stack. For Tier 1 Risk procurements, agencies prefer an IRAP assessment or an equivalent industry certification. Only ASD-endorsed assessors can perform IRAP assessments; we provide IRAP readiness and ISO 27001 preparation, not the assessment itself.
Privacy runs alongside. If the agency puts a PRIS clause in your contract, you take on the Information Privacy Principles, and from 1 January 2027 you will need to support the agency’s breach notification. We prepare a single supplier evidence pack that answers all of this, so each new tender becomes an update rather than a rewrite.
Essential Eight, ASD Essentials and the WA Essential Controls
ASD published the ASD Essentials series on 15 October 2026, with chapters for enterprise IT, cloud and operational technology and a guide to transitioning from the Essential Eight. The WA policy still names the Essential Eight at Maturity Level Two inside its Essential Controls, and obligations that name it keep doing so until they are updated. For Perth agencies and their suppliers, the sensible step is to keep reporting against the Essential Eight while mapping existing evidence to the new Essentials actions.
GRCLens: evidence once, report many times
A WA supplier can face an agency review, ISO 27001, SOCI and a customer questionnaire in one quarter. GRCLens, the GRC platform we build, maps frameworks such as ISO 27001, the Essential Eight and SOCI CIRMP to one shared control set, so a control evidenced once is reported against each.
If your board, the Auditor General or an agency customer wants an independent point-in-time view instead, see our cyber security audit services for Perth and WA organisations.
Penetration testing and security testing in Perth
The WA Auditor General keeps finding the same gaps. In the 2025 information systems audit results, fewer than a quarter of state entities met the benchmark for access management and endpoint security, and the March 2026 report on Microsoft 365 security controls described weaknesses that included a phishing-led invoice fraud. Penetration testing in Perth therefore starts where those findings point: identity, Microsoft 365 configuration, email security and how staff respond to a convincing lure.
We test web applications and APIs for WA agencies and the suppliers assessed under clause 3.4 of the 2026 WA Government Cyber Security Policy, run internal network tests that follow real attack paths, and deliver phishing simulations that measure reporting as well as clicks. For mining, LNG and port operators, our OT assessments are passive and safety first, focused on remote operations centres, vendor access and the boundary with corporate IT. Secure code review and threat modelling help Perth software teams fix flaws before release. See our penetration testing services, or the cyber security audit services in Perth for control assurance.
Frequently asked questions
Does the 2026 WA Government Cyber Security Policy bind private suppliers?
Not directly. Premier’s Circular 2025/13 makes it mandatory for Schedule 1 and Schedule 2 entities under the Public Sector Management Act 1994. It reaches suppliers through procurement: under clause 3.4 an agency must assess the cyber risk of any supplier that will access its data or systems, and the contract then carries the requirements. In practice a Perth supplier feels the policy through tender questions and contract clauses.
When does the PRIS Act start affecting WA Government contractors?
The Information Privacy Principles took effect on 1 July 2026 and mandatory breach notification starts on 1 January 2027. A contractor is bound only where its contract includes a PRIS clause under sections 129 to 130, and there is no small business carve out. Because the agency stays accountable under section 140, privacy clauses and evidence requests are likely to appear in renewals and new contracts.
Which certification should a Perth mining services firm get first?
It depends on what your buyers ask for. For Main Roads WA prequalification at higher categories, JAS-ANZ certified ISO 9001, ISO 45001 and ISO 14001 are the stated expectations. For contracts that give you access to a client’s data or systems, ISO 27001 usually carries more weight. We review your current and target contracts, recommend an order, and share documentation between standards so the second one costs less.
Can SSC issue our SOC 2 report?
No. SOC 2 reports are issued only by licensed CPA firms. We get you ready: agreeing the scope and trust services criteria, closing control gaps, preparing evidence and running a readiness review so the CPA firm’s examination runs smoothly. SOC 2 and ISO 27001 overlap heavily, so if you also need ISO 27001 we map one to the other rather than building two separate programs.
Is Maturity Level Two still the WA target now that ASD Essentials is out?
Yes, for now. The 13 Essential Controls in the 2026 WA Government Cyber Security Policy include the Essential Eight at Maturity Level Two, and that wording stands until the policy changes. ASD published the Essentials series on 15 October 2026 as the evolution of the Essential Eight. We assess against the maturity model you are measured on and map the results to the new Essentials actions.
How does the SOCI Act work for WA energy businesses outside the NEM?
The SOCI Act applies to WA responsible entities just as it does elsewhere. The difference is the market: WA runs the Wholesale Electricity Market on the South West Interconnected System, and AEMO’s AESCSF criticality tool covers WEM participants. The Cyber and Infrastructure Security Centre has also accepted the WA Government Cyber Security Policy (2024) as an equivalent framework for the CIRMP, and an AESCSF self-assessment may be submitted.
Will you come to our Perth premises or a regional WA site?
Yes, when it helps. We are based in Tarneit, Victoria, and handle most document review, interviews and reporting remotely. We travel to Perth and regional sites, including the Pilbara, for workshops, operational technology and physical security reviews, data centre visits and findings walkthroughs, wherever being present makes a real difference to the result.
Next step
Tell us which WA obligation, contract or certification is driving the question and we will scope the work to a fixed price. Contact us or email info@secsolutionshub.com. We also work with organisations in Adelaide, Melbourne and Sydney.

