Security Solution Consultants (SSC) are cyber security consultants for Nairobi organisations that need to meet Kenya’s Data Protection Act, the Central Bank of Kenya’s cybersecurity guidelines, ISO 27001 and PCI DSS. We work with banks, payment service providers, insurers, SACCOs, healthcare providers and regional headquarters in Westlands, Upper Hill and Kilimani, combining practical GRC consulting with GRCLens, our own GRC platform.
| Obligation | Who it applies to | What it asks for |
|---|---|---|
| Data Protection Act 2019 and the 2021 Regulations | Data controllers and processors, with registration required above the thresholds or in listed sectors | Registration with the ODPC, lawful processing, data protection impact assessments, security by design, and breach notice to the ODPC within 72 hours |
| CBK cybersecurity guidance for banks (2017) and payment service providers (2019) | Banks and licensed payment service providers | Board accountability, a CISO, controls and testing, and incident notification to the CBK within 24 hours |
| Computer Misuse and Cybercrimes (CII and Cybercrime Management) Regulations 2024 | Owners of designated critical information infrastructure | A CISO, a risk assessment within 12 months, reporting of changes, and hosting the infrastructure in Kenya |
| IRA Guidance Note on Cybersecurity (2025) | Insurers and reinsurers | A board approved strategy and notice of material incidents within 24 hours |
| Digital Health Act 2023 and the 2025 Health Information Regulations | Health facilities and digital health solution providers | Health data custodianship, security operations, breach notification and certification of digital health solutions |
| PCI DSS v4.0.1 | Merchants, acquirers, issuers and payment providers handling card data | Twelve requirement areas, with the future-dated requirements mandatory since 31 March 2025 |
Kenya’s payments ecosystem is built on mobile money, cards and fast-growing digital lenders, and fraud follows the money. The National Computer and Cybercrimes Coordination Committee reported in 2026 that mobile money accounted for half of documented fraud cases, and the CBK recorded 353 bank cyber fraud cases in 2024, more than double the year before. The CBK launched a Banking Sector Security Operations Centre in September 2025 and expects banks and payment providers to report incidents to it.
We assess banks and payment service providers against the CBK guidelines, prepare PCI DSS scoping and Self-Assessment Questionnaires or QSA assessments, and design the testing and incident reporting that supervisors ask about. See our PCI DSS compliance advisory.
The ODPC expects registration certificates to be renewed before they expire, and in August 2026 it gave lapsed entities 14 days to renew. Beyond registration, the Act requires a lawful basis for every purpose, data protection impact assessments for high risk processing, data protection by design, processor contracts, and breach notice to the ODPC within 72 hours (48 hours from a processor to its controller). Fines reach KES 5 million or 1% of annual turnover, whichever is lower, and the ODPC also orders compensation to complainants.
We register you, build the records and policies, run DPIAs, and set up the monitoring that keeps you compliant. In July 2026 the ODPC also consulted on AI guidance that would require DPIAs for eight common AI uses, including credit scoring and recommendation engines.
Health data may only be processed by a health care provider or a person under a duty of professional secrecy, and the Digital Health Act 2023 adds custodianship, security and certification rules for digital health solutions. With more than 32 million Kenyans registered with the Social Health Authority, hospitals, clinics, insurers and health technology providers are handling more sensitive data than ever.
We help health organisations secure patient systems and suppliers, prepare for ODPC and Digital Health Agency scrutiny, and rehearse breach response.
Kenyan banks and insurers have pursued ISO 27001 certification for years, and public tenders, from the Kenya Revenue Authority to pension funds, increasingly ask for it. KENAS has accredited the Kenya Bureau of Standards to certify against ISO/IEC 27001:2022, alongside international certification bodies. A well scoped ISMS also gives you the evidence for Data Protection Act security duties and CBK expectations.
We design the scope, run the risk assessment, prepare evidence and support you through certification. Learn more about our ISO 27001 implementation and advisory.
Consulting gets you compliant. GRCLens, the governance, risk and compliance platform we built and use on every engagement, keeps you compliant. It orchestrates your regulatory and legislative compliance in one place, so your risk, compliance and audit teams work from the same controls, evidence and numbers.
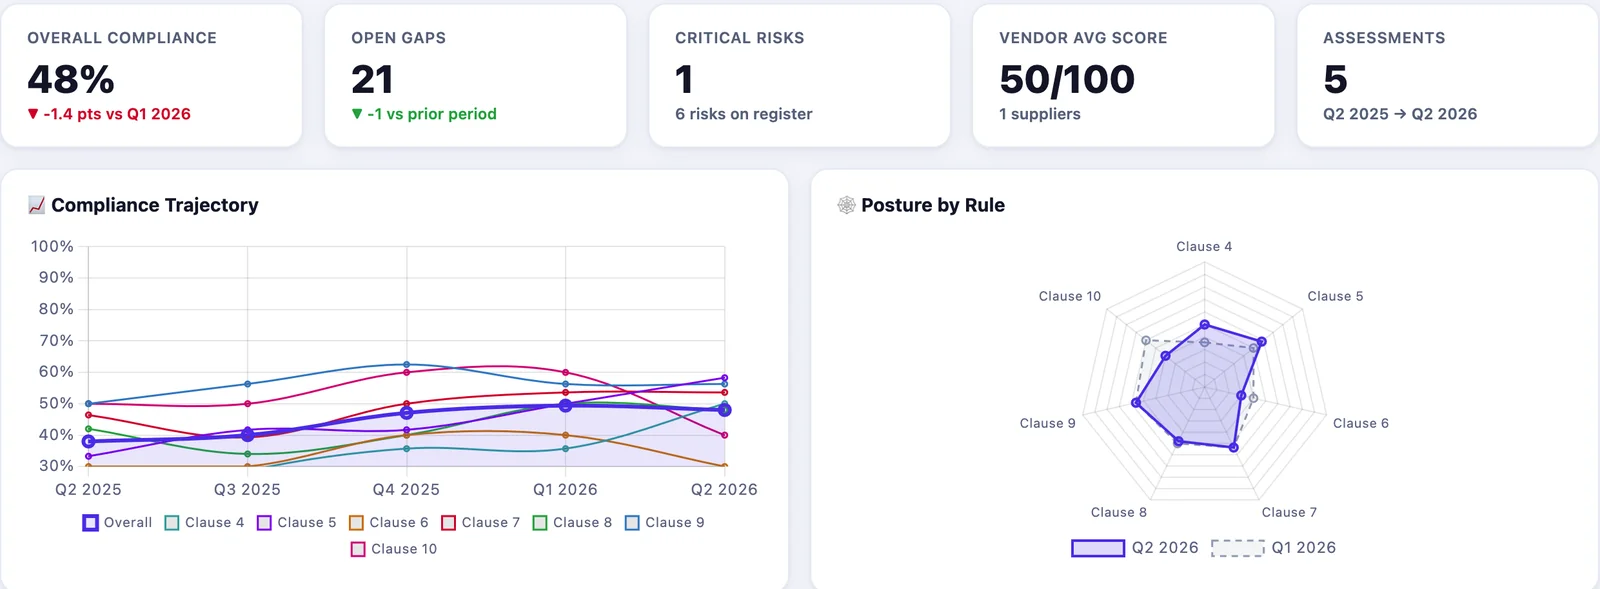
See GRCLens for Kenya, or request a GRCLens demo.
We also support organisations in Johannesburg, Cape Town, Lusaka and Harare.