IEC 62443 Consulting and OT Security Assessment

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

Our IEC 62443 consulting helps the operators and suppliers of industrial control systems turn the standard into decisions: which zones you have, how they connect, what security level each one needs, and how to get there without putting safety or production at risk. Security Solution Consultants (SSC) provides IEC 62443-3-2 risk assessments, zone and conduit design, OT security assessments and security program reviews for energy, water, transport, mining and manufacturing, and gap assessments for product suppliers preparing for certification. We work across Australia, New Zealand and the Gulf, where IEC 62443 sits alongside the SOCI Act, the AESCSF and Saudi Arabia’s OTCC.
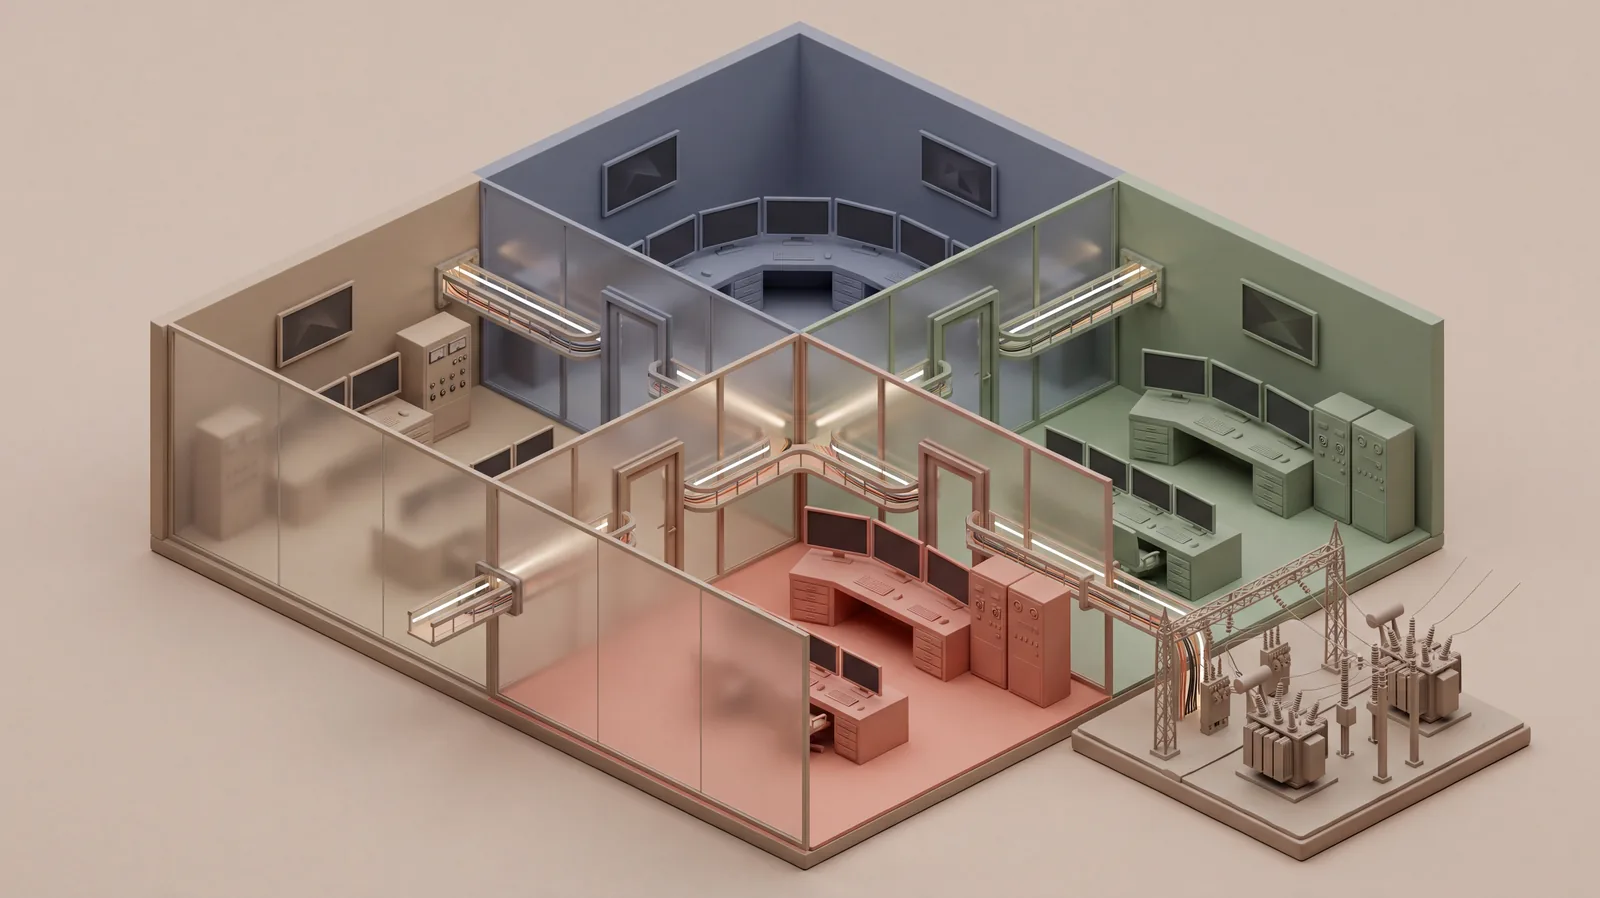
Empty substation control room divided by frosted glass partitions into colour-tinted zones, with glowing cable trays passing through sealed openings between them, representing IEC 62443 zones and conduits
Zones and conduits turn a flat plant network into areas you can reason about and defend.

The IEC 62443 series at a glance

ISA/IEC 62443 is a series of standards for securing industrial automation and control systems (IACS). Its parts are written for different roles: the asset owner who runs the plant, the integrator or service provider who builds and maintains it, and the supplier who makes the components. The parts most engagements use are:

PartTitleWritten forHow we use it
62443-2-1Security program requirements for IACS asset owners (Edition 2.0, 2024)Asset owners and operatorsDesign or assess your OT security program. The 2024 edition restructures requirements into program elements and adds a maturity model.
62443-2-4Security program requirements for IACS service providersIntegrators and maintenance providersSet and check requirements for the integrators and vendors who work on your systems.
62443-3-2Security risk assessment for system designAsset owners and integratorsDefine the system, partition it into zones and conduits, assess risk and set a target security level for each.
62443-3-3System security requirements and security levelsIntegrators and asset ownersSystem requirements under seven foundational requirements, FR 1 to FR 7, at security levels 1 to 4.
62443-4-1Secure product development lifecycle requirementsProduct suppliersGap assessment of your secure development lifecycle.
62443-4-2Technical security requirements for IACS componentsProduct suppliersGap assessment of a component’s security capability.

Zones, conduits and security levels

A zone groups assets that share the same security requirements; a conduit groups the communication channels that connect two or more zones and share common security requirements. IEC 62443-3-2 sets out the process: define the system under consideration, partition it into zones and conduits, assess the risk of each, set a target security level for each, and document the resulting security requirements.

The series uses three views of a security level, and the gaps between them are where the work is:

  • SL-T (target). The level a zone or conduit needs, set by the risk assessment.
  • SL-C (capability). The level a system or component can deliver when properly configured, defined in 62443-3-3 for systems and 62443-4-2 for components.
  • SL-A (achieved). The level the system actually reaches as built and operated, which is what an assessment measures.

Where SL-A falls short of SL-T, you have a remediation plan. Where SL-C falls short of SL-T, no amount of configuration will close the gap, and compensating countermeasures, such as a tighter conduit, are needed.

Security levelProtects against
SL 1Casual or coincidental violation
SL 2Intentional violation using simple means, with low resources, generic skills and low motivation
SL 3Intentional violation using sophisticated means, with moderate resources, IACS-specific skills and moderate motivation
SL 4Intentional violation using sophisticated means, with extended resources, IACS-specific skills and high motivation

Most of our engagements are for asset owners: the utilities, ports, mines and plants that own the risk. We also work with system integrators who need to show that what they deliver meets a specified SL-T, and with product suppliers whose customers now ask for evidence against 62443-4-1 and 62443-4-2 before they buy.

Our IEC 62443 consulting services

  • IEC 62443-3-2 risk assessment. Workshops with your engineers covering the system under consideration, initial risk, the zone and conduit model, detailed risk for each zone and conduit, SL-T, and a cybersecurity requirements specification you can build and buy against.
  • Zones and conduits design. Segmentation architecture for brownfield and greenfield sites, including the industrial DMZ, vendor remote access and data flows to the enterprise and the cloud.
  • OT security assessment. A passive, safety-first review of the plant as it actually is, measuring SL-A against the target and the drawings against reality.
  • SCADA security assessment. Control centres, remote sites and the telemetry, radio and cellular links between them, with particular attention to vendor and support access.
  • Asset owner security program (62443-2-1). Policies, roles, asset inventory, patch and change management, incident response and recovery, scored against the 2024 edition’s maturity model.
  • Integrator and supplier requirements. Security requirements for specifications and contracts based on 62443-2-4 and 62443-3-3, and checks of what was delivered before you accept it.
  • Product supplier readiness (62443-4-1 and 62443-4-2). Gap assessments of your development lifecycle and component capability before certification by an accredited body.

How we assess without putting the plant at risk

Operational technology controls physical processes, so availability and safety come first. Our OT security assessments are passive by default:
  1. Rules agreed with operations. What we may touch, the change windows, and who can stop the work at any time.
  2. Documents and architecture. Network drawings, asset registers, firewall rule sets and remote access designs.
  3. Interviews. Engineers, operators, maintenance contractors and vendors.
  4. Offline configuration review. Firewalls, switches and remote access gateways reviewed from exported configurations.
  5. Passive traffic analysis. Capture from a SPAN port or network tap to build an asset inventory and compare the conduits actually in use with the ones on the drawing.
  6. Active checks only by agreement. In writing, in a maintenance window or on a test bench. For deeper testing, see our penetration testing and security testing services.
Close-up of a programmable logic controller rack in an open cabinet, with an orange armoured fibre conduit clamped by a brass padlock, representing a protected OT conduit
A conduit is only as strong as the controls on every channel that runs through it.

One assessment, several obligations

We map every finding to the obligations it supports, so one body of evidence serves several regimes.

ObligationWhere IEC 62443 work helps
SOCI Act CIRMPThe enhanced CIRMP rules require an inventory of critical systems and how they connect, and network segregation so critical systems can operate independently, by about June 2028. A zone and conduit model is a direct way to evidence both. IEC 62443 is not itself one of the recognised CIRMP cyber frameworks, so we map the work into the framework you have chosen.
AESCSF version 2Supports practices in the cyber security architecture domain added in version 2, and in asset, threat and vulnerability, and access management.
Saudi NCA OTCC-1:2022The National Cybersecurity Authority’s extension of the Essential Cybersecurity Controls for industrial control systems. We map zone, conduit and remote access findings to OTCC controls for Saudi operators.
NIST SP 800-82 Rev. 3NIST’s guide to OT security, often used alongside IEC 62443 for architecture and monitoring.

What you receive

  • A zone and conduit diagram and register, agreed with your engineers
  • A risk assessment with an SL-T for every zone and conduit
  • An SL-A gap analysis from the assessment
  • A cybersecurity requirements specification for projects and procurement
  • A prioritised roadmap mapped to your CIRMP, AESCSF or OTCC obligations
  • A short board summary in plain language
  • Optional tracking of zones, security levels and actions in the GRCLens IEC 62443 module

We advise; we do not certify. SSC is an independent consultancy, not a certification body. We are not an IECEE or ISASecure certification body and we do not issue IEC 62443 certificates. We prepare asset owners and suppliers for assessment by an accredited body, and keeping the adviser separate from the certifier protects the value of the certificate.

Why work with SSC

  • Our consultants assess OT environments, AESCSF maturity and CIRMP programs for energy and infrastructure operators, so recommendations reflect how plants actually run.
  • Safety first and passive by default, with active testing only on operations’ written agreement.
  • SSC is certified to ISO/IEC 27001 and follows a Secure by Design approach.
  • The same practitioners teach our ISA/IEC 62443 fundamentals course, part of our critical infrastructure and OT security training, so your team can carry the work forward.
  • The GRCLens IEC 62443 module keeps the security program, FR 1 to FR 7, zones, conduits and security levels in one place.

Related services: energy sector security assessments and AESCSF, SOCI Act compliance and CIRMP audit, penetration testing and OT assessments and critical infrastructure and OT security training.
Frequently asked questions

A series of international standards, published jointly as ISA/IEC 62443, for securing industrial automation and control systems. It covers security programs for asset owners and service providers, risk assessment and system design using zones and conduits, and security requirements for systems, products and components.

SL-T is the target security level a zone or conduit needs, set by the risk assessment. SL-C is the level a system or component can provide when properly configured. SL-A is the level actually achieved in operation, which is what an assessment measures.

A zone is a group of assets that share the same security requirements. A conduit is a group of communication channels that connect zones and share common security requirements. Together they give each part of the plant a defined boundary and a target security level.

Not by default. We rely on documentation, interviews, offline configuration review and passive traffic analysis. Any active testing is agreed in writing with operations and done in a maintenance window or on a test bench.

No. SSC is an independent consultancy, not an IECEE or ISASecure certification body, and does not issue IEC 62443 certificates. We prepare asset owners and suppliers for assessment by an accredited body.

Not on its own. The CIRMP rules name specific recognised frameworks, such as ISO/IEC 27001, the Essential Eight, the NIST Cybersecurity Framework, C2M2 and the AESCSF. IEC 62443 work provides strong evidence for the OT parts of the program, and we map it into the framework you have chosen.

Asset owners usually start with a 62443-3-2 risk assessment of one important system, which produces the zone and conduit model and target security levels, then build the 62443-2-1 program around it. Product suppliers start with 62443-4-1 for the development lifecycle, then 62443-4-2 for each component.

Yes. For Saudi operators we map IEC 62443 findings to the National Cybersecurity Authority's Operational Technology Cybersecurity Controls (OTCC-1:2022), the extension of the Essential Cybersecurity Controls for industrial control systems.

Talk to us about IEC 62443 and OT security

Tell us where you are today and what you need to achieve. We will come back with a clear scope, timeline and fixed quote.