SOCI Act Audit and Compliance Advisory

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

Our SOCI Act compliance services help responsible entities for critical infrastructure assets meet their obligations under the Security of Critical Infrastructure Act 2018: registering assets, reporting cyber incidents, and running a Critical Infrastructure Risk Management Program (CIRMP) that the board can sign off with confidence. Security Solution Consultants (SSC) provides SOCI Act audits, CIRMP assessments and advisory for energy, water, transport, data storage, health, food and other critical infrastructure sectors across Australia.
Leadership team reviewing a risk program binder with transmission towers and port cranes outside the window, representing SOCI Act compliance
The SOCI Act makes critical infrastructure risk a board responsibility.

SOCI Act obligations at a glance

The SOCI Act is administered by the Cyber and Infrastructure Security Centre in the Department of Home Affairs. It covers critical infrastructure assets across 11 sectors: communications, data storage or processing, defence industry, energy, financial services and markets, food and grocery, health care and medical, higher education and research, space technology, transport, and water and sewerage. Which obligations apply depends on the asset class.

ObligationWhat it requires
Register of critical infrastructure assetsOwnership and operational information about the asset, kept up to date
Mandatory cyber incident reportingReport critical cyber incidents with a significant impact within 12 hours, and other incidents with a relevant impact within 72 hours
Critical Infrastructure Risk Management Program (CIRMP)Identify and minimise material risks across four hazard domains, comply with a recognised cyber security framework, and submit a board-approved annual report
Enhanced cyber security obligationsFor Systems of National Significance: incident response planning, cyber security exercises, vulnerability assessments and system information reporting, when required

Amendments passed in late 2024 also brought certain data storage systems that hold business critical data within the scope of the critical infrastructure asset they support.
Our SOCI Act and CIRMP services

  • Applicability assessment. Confirm which of your assets are critical infrastructure assets, which obligations apply, and who in the organisation owns each one.
  • CIRMP design and uplift. A written program covering the four hazard domains, with risk registers, controls, owners and review cycles that fit your existing risk framework.
  • Cyber framework compliance. Assess and uplift against the recognised framework you choose, such as the Essential Eight, ISO/IEC 27001, the NIST Cybersecurity Framework or the AESCSF for energy.
  • Independent CIRMP audit. An independent review of whether your program is in place and working, so directors have evidence before they approve the annual report.
  • Incident reporting readiness. Playbooks, thresholds and contact trees so the 12-hour and 72-hour reporting clocks can be met in a real incident.
  • Board reporting and the annual report. A clear board paper and the evidence pack behind the attestation.

The four CIRMP hazard domains

Critical infrastructure facility with a secure perimeter fence and a control building under storm clouds, representing the four CIRMP hazard domains
A CIRMP covers cyber, people, suppliers and the physical world in one program.
Hazard domainWhat we assess
Cyber and information securityCompliance with your chosen cyber framework, critical systems, access, monitoring and incident response
PersonnelCritical workers, background checks, insider risk and access when people leave
Supply chainSuppliers and service providers with access to the asset, offshore dependencies and contract controls
Physical security and natural hazardsSite security, environmental and natural hazard risks, and recovery arrangements

What a SOCI Act audit covers

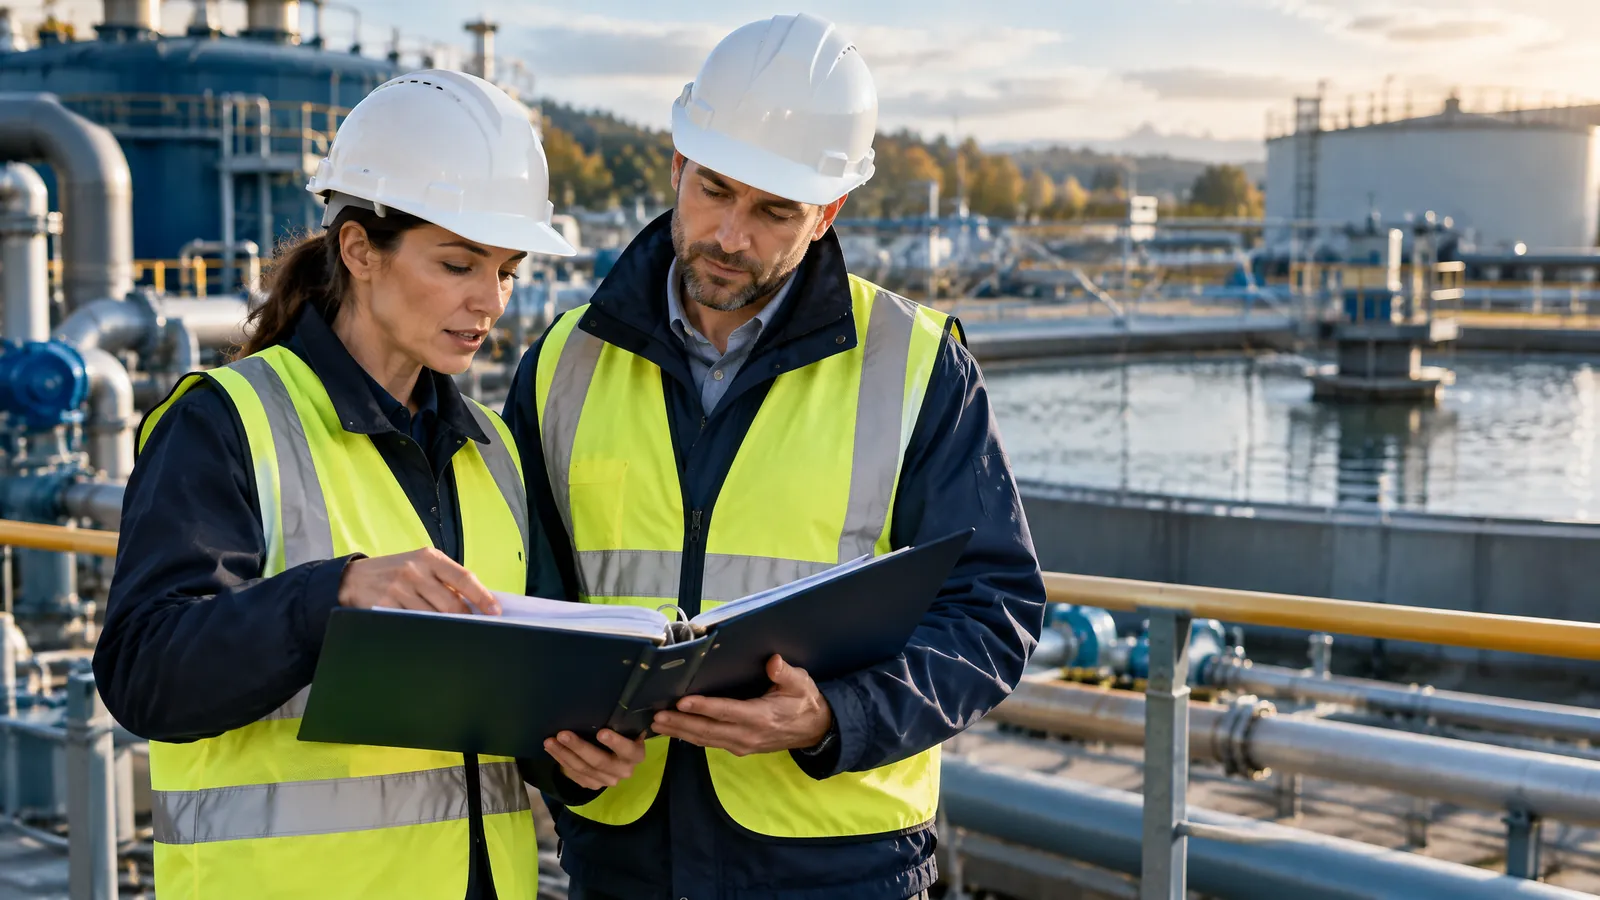
Auditor and engineer in hard hats reviewing an evidence binder at a water treatment plant, representing a SOCI CIRMP audit
An independent review gives directors evidence before they attest.

The SOCI Act does not require an external audit, but boards must approve an annual CIRMP report and stand behind it. Our audit gives them independent evidence. We review:

  1. Whether the CIRMP document meets the rules and reflects how the asset actually operates.
  2. Whether material risks in each hazard domain are identified, assessed and owned.
  3. Whether the controls described are in place and operating, using samples of evidence.
  4. Progress against the recognised cyber framework, including maturity scores where relevant.
  5. Incident reporting arrangements, tested against a realistic scenario.
  6. Governance: review cycles, board reporting and the annual report process.

The result is a findings report with ratings, a remediation plan with owners and dates, and a short board summary.

Why work with SSC

  • We work with critical infrastructure operators on the AESCSF, the Essential Eight and ISO/IEC 27001, so the cyber domain of your CIRMP is built on practical experience.
  • SSC is certified to ISO/IEC 27001 and follows a Secure by Design approach.
  • Our GRCLens platform can hold the CIRMP risk register, controls and evidence, so the annual report draws on live data instead of spreadsheets.

Related services: energy sector security and AESCSF assessments, enterprise risk management, and critical infrastructure and OT security training. Read our guide to what the 2026 CIRMP rules mean.
Frequently asked questions

Responsible entities and direct interest holders of critical infrastructure assets across 11 sectors, including energy, water, transport, communications, data storage, health, food and grocery, and financial services. Which obligations apply depends on the asset class.

A Critical Infrastructure Risk Management Program is a written program that identifies and minimises material risks to an asset across four hazard domains: cyber and information security, personnel, supply chain, and physical security and natural hazards.

Within 90 days after the end of the Australian financial year, which is 28 September for a year ending 30 June. The report must be approved by the board, council or other governing body.

No. The Act requires a board-approved annual report, not an external audit. An independent audit gives directors evidence that the program is in place and working before they approve the report.

The CIRMP rules recognise frameworks such as the Essential Eight at maturity level one, ISO/IEC 27001, the NIST Cybersecurity Framework and, for energy, the AESCSF at security profile one, or an equivalent.

Critical cyber incidents having a significant impact must be reported within 12 hours of becoming aware of them, and other incidents having a relevant impact within 72 hours.

Talk to us about SOCI Act compliance

Tell us where you are today and what you need to achieve. We will come back with a clear scope, timeline and fixed quote.