Robotaxis stopped being a thought experiment in 2026. Fully driverless, fare-charging services now run in Dubai and Abu Dhabi, Waymo has lobbied Australian governments for a national law, and Australia’s transport ministers have agreed to allow conditional automated vehicle deployment in selected locations from 2027.
That timeline puts a hard question in front of every board whose organisation builds, operates, insures, finances or relies on automated vehicles: when a driverless car is hacked and someone is hurt, who is accountable? This guide sets out where the law stands in Australia and New Zealand in September 2026, what the proposed accountability model asks of directors, and the questions boards should be asking now, before the first incident rather than after it.
The short answer
In brief: In Australia, the proposed Automated Vehicle Safety Law puts responsibility for an automated driving system on a company, the Automated Driving System Entity (ADSE), rather than on the person in the seat, and gives its executive officers due diligence duties. Until that law exists, liability for a hacked vehicle would be argued through product liability, the Australian Consumer Law and state injury schemes that were written for human drivers. In New Zealand, there is no automated vehicle framework yet, and trials run on case-by-case exemptions.
In both countries, cyber security is not a separate topic from vehicle safety. Under the Australian model, an ADSE would have to show how its system was designed to resist intrusion, how intrusions will be detected, and how their consequences will be limited. A board that treats vehicle cyber risk as an IT matter will find it has misread the law.
Where the law stands in Australia in 2026
Australia’s reform has been led by the National Transport Commission and the federal Department of Infrastructure, with a public consultation on the regulatory framework and the Automated Vehicle Safety Law (AVSL) held from April to June 2024. The core design choice is that a Commonwealth in-service regulator will oversee automated driving systems, and each system will have a responsible corporate entity. The NTC’s automated vehicle program sets out the background.
| Instrument | Status in September 2026 | What it means for cyber risk |
|---|---|---|
| Automated Vehicle Safety Law (Commonwealth) | Designed and consulted on; we have seen no bill introduced to Parliament | Will create the ADSE, a general safety duty, and due diligence duties for executive officers |
| Ministers’ deployment decision (21 November 2025) | Agreed: conditional deployment in selected locations from 2027 | Pilots will start before the national law is complete, so contracts and permits carry the risk allocation |
| UN Regulations 155 and 156 (vehicle cyber security and software updates) | Not mandated in Australia; the Australian Electric Vehicle Association called for adoption in June 2026 | No mandatory vehicle cyber management system for type approval yet |
| UN Regulation and GTR on Automated Driving Systems | Adopted by UNECE WP.29 on 24 June 2026; entry into force expected January 2027 | Likely template for any future Australian standard on driverless systems |
One point is often misreported. Several vendor websites say Australia has required UN Regulation 155 since 2024. It has not. The Australian Electric Vehicle Association’s June 2026 policy statement says Australia has no dedicated, mandatory vehicle cyber security or software update regime, and its first recommendation is to adopt one aligned with UN R155 and R156. Boards relying on supplier assurances should check which regime the assurance actually refers to.
New Zealand: exemptions, not a framework
New Zealand’s Ministry of Transport says current law does not expressly require a driver, but most regulations assume one, and the settings suit driver assistance rather than Levels 3 to 5. Trials run on exemptions granted case by case under section 166 of the Land Transport Act 1998. In August 2026, the Transport Minister told 1News that changing the rules is not an immediate priority, even as a US robotaxi operator announced plans for New Zealand roads.
Two other threads matter. The ACC scheme means injury compensation is no-fault, which shifts the argument from compensation to recovery and regulatory accountability. And the Government’s proposed critical infrastructure cyber regime, consulted on until April 2026, would bring major roads, rail freight, airports and large ports into scope, with directors responsible for compliance through attestations. We cover that regime for transport operators in our companion article on GRCLens.
What the ADSE model asks of directors
The NTC’s 2024 paper on ADSE in-service obligations describes a general safety duty: the ADSE must ensure its system operates safely so far as reasonably practicable. Cyber security sits inside that duty rather than beside it. The ADSE would need to demonstrate that it has:
- designed the system to minimise the risk of cyber intrusion;
- a way to detect intrusions and limit their consequences;
- controls that stop the automated system operating if safety-critical software updates are not installed, or if faults appear after an update;
- an Australian presence, so there is a local entity the regulator can hold to account.
Executive officers of an ADSE would carry due diligence obligations, a model familiar from work health and safety law. In practice that means directors will need evidence, not assurances: that they understood the risks, resourced the controls, received meaningful reporting and acted on it. The UK has already legislated a similar structure. Its Automated Vehicles Act 2024 creates an Authorised Self-Driving Entity with a lifetime duty to keep the vehicle driving safely and lawfully, a user-in-charge who is protected from driving offences while the feature is engaged, and licensed operators for journeys with nobody in control.
The attack surface is already in production
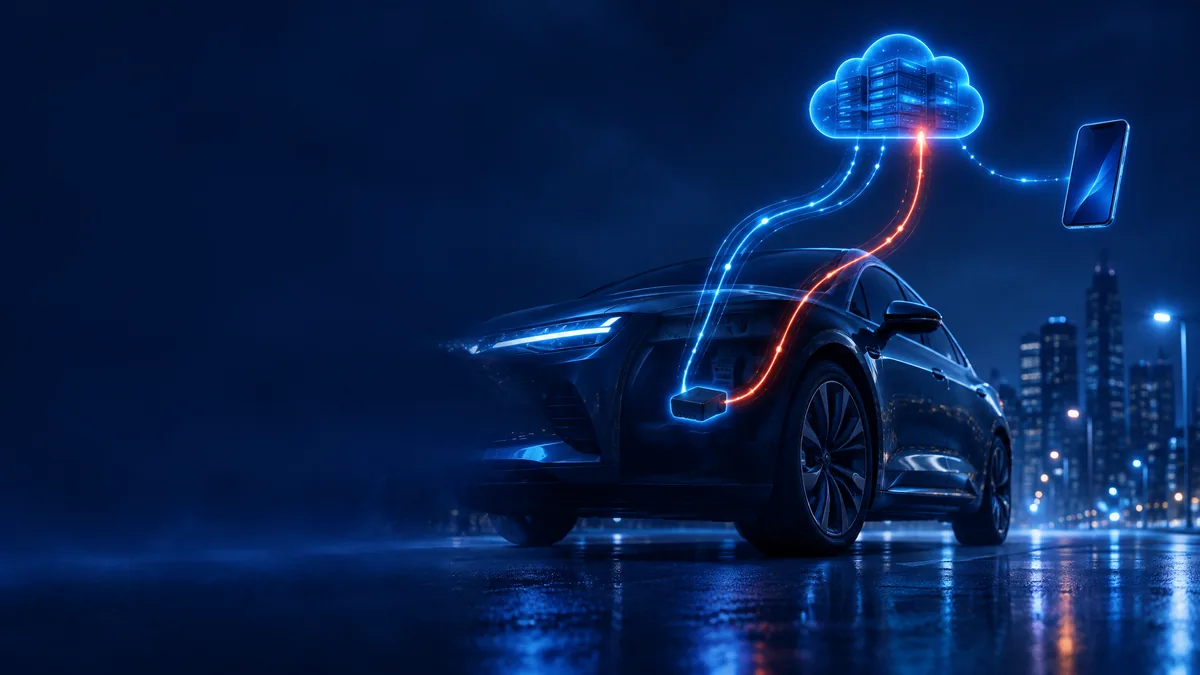
The research record of the last two years shows where risk actually enters a connected or automated vehicle. It is rarely the car alone:
- Dealer and cloud portals. In 2024, researchers showed that a flaw in Kia’s dealer portal could let an attacker take remote control of many vehicles in about 30 seconds using only the licence plate. In January 2025, a similar admin-panel flaw in Subaru’s Starlink service exposed remote vehicle control and more than a year of location history.
- Supplier software. The PerfektBlue flaws in a widely used Bluetooth stack, disclosed in July 2025, affected infotainment units at several major manufacturers. The supplier shipped patches in September 2024, yet some manufacturers did not push fixes until June 2025. Supplier patch latency is a board-level risk, not a technical footnote.
- Chained exploits. At Black Hat Asia 2025, researchers chained 11 vulnerabilities in a 2020 Nissan Leaf to move from Bluetooth to cellular control, including the steering while the car was moving.
- Volume. Pwn2Own Automotive 2026 in Tokyo produced 76 zero-day vulnerabilities and more than US$1 million in awards in three days.
The Upstream Security 2026 Automotive and Smart Mobility report, which analysed 494 public incidents from 2025, found that 92% of attacks were remote, 67% involved telematics or cloud systems, and ransomware-related incidents more than doubled to 44%. It also described attackers using a companion app to lock owners out of their vehicles and demand payment.
Who pays when: a liability map
Until the AVSL is in force, the answer depends on which existing regime a claim lands in. The table below summarises the routes commentators and courts are likely to use. It is general information, not legal advice.
| Scenario | Likely route today (Australia) | What changes under the proposed model |
|---|---|---|
| Injury caused by an automated vehicle after a cyber attack | State motor accident injury (CTP) schemes, which may need expert evidence that a vehicle under full automation was being ‘driven’; product liability claims against the manufacturer | The ADSE carries the in-service safety duty; schemes are expected to add recovery mechanisms for injuries caused by an automated system |
| Defect in automation software exploited by an attacker | Australian Consumer Law and product liability against the manufacturer, software designer or licensor | Regulator can act against the ADSE directly for failing its safety duty |
| Supplier component flaw with slow patching | Contract claims between manufacturer and supplier; indemnities decide who bears the loss | ADSE remains accountable to the regulator regardless of which supplier failed |
| Fleet operator’s cloud platform breached | Privacy Act, contract, and directors’ duties; possible SOCI obligations if the operator runs critical freight or transport assets | Operator obligations depend on the final split between ADSE and operator roles |
New Zealand’s ACC scheme changes the first row: an injured person is covered regardless of fault, and the practical questions become recovery, regulatory action and reputation.
Three governance lessons from the United States
The US has the longest operating record for robotaxis, and its lessons are about governance as much as technology:
- Disclosure is a control. After a Cruise vehicle dragged a pedestrian in San Francisco in October 2023, the company paid a US$1.5 million penalty to NHTSA for omitting crash details and later a US$500,000 fine for filing a false report. GM stopped funding the robotaxi business in December 2024. The failure that ended the program was candour, not code.
- Recalls must actually fix the problem. Waymo recalled software on more than 3,000 vehicles in December 2025 after reports that its cars passed stopped school buses; officials said some incidents happened after Waymo said the issue was fixed. Boards should ask how a fix is verified, not only whether it shipped.
- Remote operation is part of the attack surface. Tesla disclosed in May 2026 that two low-speed robotaxi crashes in Austin happened while a remote operator was driving. Teleoperation channels need the same identity, logging and resilience controls as the vehicle itself.
Ten questions every board should ask now
- Which of our entities would be the ADSE, the operator, or a supplier to either, and have we mapped the duties each role carries?
- Which vehicle cyber and software update standards do our suppliers certify against, and are those certifications recognised in Australia or only overseas?
- Do we hold a current threat analysis and risk assessment (TARA) under ISO/SAE 21434 for every vehicle system we are responsible for?
- How quickly can we push a safety-critical update to every vehicle, and can we stop a vehicle operating if it misses one?
- What are our contractual patch timelines with component and software suppliers, and what happened last time a supplier was late?
- How do we monitor the cloud, telematics and companion app platforms that 92% of attacks now use?
- Who can remotely operate or command our vehicles, how is that access authenticated, and is every session logged?
- If a vehicle is hijacked, what is our playbook for stopping the fleet, notifying regulators and informing the public, and when did we last test it?
- What evidence would we show a regulator to prove due diligence by our executive officers?
- Which insurers, CTP schemes or ACC recovery routes apply to us, and where are the gaps?
Standards to anchor the programme
Even without an Australian mandate, the international standards give boards a defensible benchmark:
- UN Regulation 155 for a certified cyber security management system across the vehicle lifecycle, and UN Regulation 156 for software update management.
- ISO/SAE 21434 for road vehicle cyber security engineering, with threat analysis and risk assessment as the core evidence.
- ISO/IEC 27001 and NIST CSF 2.0 for the organisation-wide security management system around the fleet, the cloud platform and the operations centre. ISO/SAE 21434 itself expects an organisation-level security management system alongside it.
For a deeper look at the technical controls, see our earlier analysis of driverless car cyber risks and controls on GRCLens, and for the wider threat picture, the top cybersecurity threats of 2026.
Related reading
- Cybersecurity threats in 2026
- GRC in cybersecurity: why it matters
- Cyber security services in New Zealand
Frequently asked questions
Is Australia’s Automated Vehicle Safety Law in force?
No. The law has been designed and consulted on, and ministers agreed in November 2025 to allow conditional deployment from 2027, but as at September 2026 we have not seen the bill introduced to Parliament.
Does Australia require UN Regulation 155 for new vehicles?
No. Some vendor material says it does, but the Australian Electric Vehicle Association’s June 2026 policy statement confirms there is no mandatory vehicle cyber security or software update regime yet.
Who is liable if a hacked robotaxi injures someone in New Zealand?
The injured person is covered by ACC regardless of fault. The open questions are recovery against the operator or manufacturer and regulatory accountability, because New Zealand has no automated vehicle framework yet.
What is an ADSE?
An Automated Driving System Entity is the company that would be responsible for an automated driving system under Australia’s proposed law, with a general safety duty that includes cyber security and due diligence duties for its executive officers.
How Security Solution Consultants can help
Security Solution Consultants helps boards and executive teams in Australia, New Zealand and the Gulf get ahead of automated vehicle risk before the law does it for them. We map which entities would carry ADSE, operator and supplier duties, run threat analysis and risk assessments aligned with ISO/SAE 21434, build the ISO 27001 and NIST CSF programme around your fleet platform, and design the board reporting that shows due diligence. Where a fleet touches freight or transport infrastructure, we align the programme with the SOCI Act and New Zealand’s proposed critical infrastructure regime.
Our enterprise risk management and security compliance teams work alongside GRCLens, which keeps the risk register, supplier assessments and evidence in one place. Talk to us about an automated vehicle governance review.