Security Solution Consultants (SSC) are cyber security consultants for Cape Town organisations that need to protect customer data under POPIA, certify to ISO 27001, secure card payments under PCI DSS and govern their use of AI. We work with technology and fintech firms, insurers, healthcare providers, retailers and resources companies across the CBD, Century City, Woodstock and the Foreshore, combining hands-on GRC consulting with GRCLens, our own GRC platform.
| Obligation | Who it applies to | What it asks for |
|---|---|---|
| POPIA and the 2018 Regulations (amended April 2025) | Every organisation that processes personal information | An Information Officer, a personal information impact assessment, security safeguards, operator contracts and security compromise notification |
| ISO/IEC 27001:2022 | Any organisation that wants independent proof of its information security | An information security management system with risk based controls, internal audit and management review |
| PCI DSS v4.0.1 | Merchants and payment providers that handle card data | Twelve requirement areas, including the script and payment page controls in requirements 6.4.3 and 11.6.1 |
| ISO/IEC 42001:2023 and POPIA s 71 | Organisations that build, buy or use AI | An AI management system, and no decisions with legal effect based solely on automated profiling unless an exception applies |
| Joint Standards 1 of 2023 and 2 of 2024 | Insurers, banks, pension funds and other listed financial institutions | IT governance, cyber resilience, testing and 24 hour notification of material incidents |
Cape Town’s software and fintech companies ship AI features faster than their governance can keep up. ISO/IEC 42001 gives a certifiable way to show that AI is inventoried, risk assessed, tested and overseen by people. In August 2026 a South African customer experience provider announced what it described as the first local ISO 42001 certification in its sector, and procurement teams are starting to ask for the same.
We inventory your AI systems, run AI risk and impact assessments, align them with POPIA’s rules on automated decisions, and prepare you for certification. See our ISO 42001 consulting and the GRCLens ISO 42001 module.
South African healthcare organisations faced an average of 1,626 attacks a week in 2026, according to Check Point data reported in June 2026, and the National Health Laboratory Service ransomware attack in June 2024 showed how quickly clinical services stall when systems go down. Health information can be processed only under POPIA’s special personal information conditions, and HPCSA telehealth guidance adds consent and record keeping expectations.
We help hospitals, clinics, laboratories and medical schemes secure clinical systems, manage suppliers that host patient data, rehearse incident response and evidence their safeguards. Our incident response and recovery and data protection and encryption services support this work.
PCI DSS is enforced by the card schemes and acquiring banks rather than by statute, but a card data breach is also a POPIA security compromise. Since 31 March 2025 the future-dated PCI DSS v4.0.1 requirements are mandatory, including control of every script on payment pages. In August 2026 the South African Reserve Bank took direct responsibility for payment system standards when PASA’s recognition ended.
We confirm your scope, help you choose the right Self-Assessment Questionnaire or prepare for a QSA assessment, close the gaps and keep evidence current. See our PCI DSS compliance advisory and the GRCLens PCI DSS module.
For a Cape Town SaaS company, one well designed control set can support ISO 27001 certification, a SOC 2 report for North American customers and your POPIA section 19 safeguards. We build that control set once, then map it to each requirement so evidence is collected once. Learn more about ISO 27001 implementation and SOC 2 readiness consulting.
Consulting gets you compliant. GRCLens, the governance, risk and compliance platform we built and use on every engagement, keeps you compliant. It orchestrates your regulatory and legislative compliance in one place, so your risk, compliance and audit teams work from the same controls, evidence and numbers.
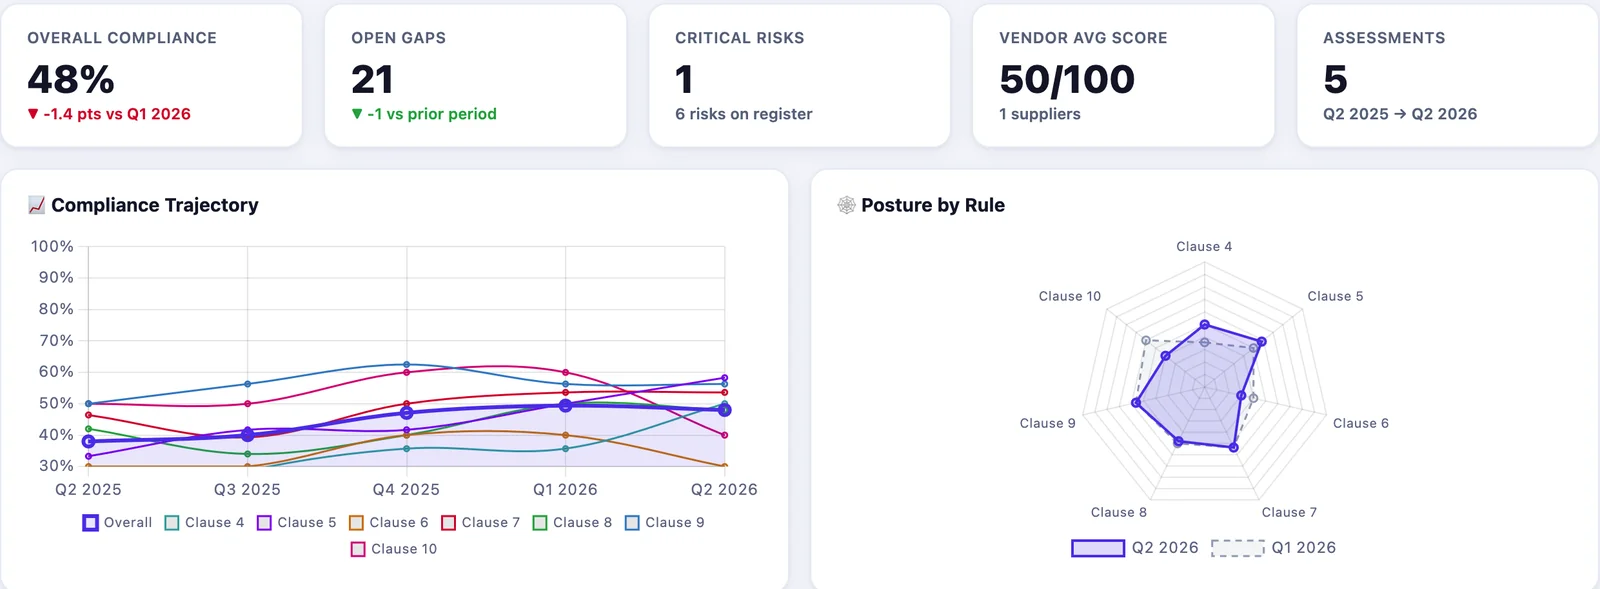
See GRCLens for South Africa, or request a GRCLens demo.
We also support organisations in Johannesburg, Nairobi, Lusaka and Harare.