Cyber Security and Data Protection Consultants in Harare, Zimbabwe

Yellow circular logo with intertwined abstract shapes next to "Business Continuity Management (BCM).
EASMLens external attack surface management platform logo
NSPM network security policy management logo
PhishLens phishing simulation and awareness logo

Security Solution Consultants (SSC) are cyber security consultants for Harare organisations that need to meet Zimbabwe’s Cyber and Data Protection Act, POTRAZ licensing and inspections, Reserve Bank of Zimbabwe cyber security expectations, ISO 27001, PCI DSS and ISO 45001. We work with banks, insurers, mobile money and fintech providers, mining companies, healthcare providers and local authorities, combining practical GRC consulting with GRCLens, our own GRC platform.
Zimbabwean professionals discussing a governance report in a Harare boardroom with jacaranda trees in bloom outside, representing cyber security and data protection consultants in Zimbabwe
POTRAZ inspections began on 1 September 2026.

Why Zimbabwean organisations are acting now

  • Under Statutory Instrument 155 of 2024, data controllers need a POTRAZ licence, renewed every 12 months, and a certified data protection officer appointed within 90 days.
  • From 1 September 2026, POTRAZ began risk based compliance inspections, naming financial institutions, insurers, local authorities, healthcare providers, mining companies and schools.
  • Mobile money fraud is estimated to cost more than US$30 million a year, and ZB Financial Holdings was hit by ransomware in July 2024 with data leaked online.
  • Zimbabwe launched its National AI Strategy 2026 to 2030 in March 2026, proposing a regulatory committee within POTRAZ.

The obligations we help you meet

ObligationWho it applies toWhat it asks for
Cyber and Data Protection Act [Chapter 12:07]Data controllers and processorsLawful processing, special rules for sensitive, health, genetic and biometric data, security safeguards, and breach notice to POTRAZ within 24 hours
SI 155 of 2024 (licensing and data protection officers)Data controllers, with licence fees from US$50 to US$2,500 by tierA POTRAZ licence renewed every 12 months, a certified data protection officer, and notice to affected people within 72 hours of a breach
POTRAZ Regulatory Notice 2 of 2026Financial institutions, insurers, local authorities, healthcare, mining and schools firstRisk based compliance inspections from 1 September 2026
Reserve Bank of Zimbabwe cyber security guidanceBanks and payment system providersBoard oversight, a CISO, third party risk management, periodic audits and incident reporting
Mines and Minerals Act, mining safety regulations and ISO 45001Mining companies and contractorsMine safety duties; ISO 45001 is held by major operators such as Zimplats and Mimosa
PCI DSS v4.0.1Banks, switches, merchants and payment providers handling card dataTwelve requirement areas, with the future-dated requirements mandatory since 31 March 2025

POTRAZ licensing, data protection officers and inspections

A data protection officer presenting a register and a laptop to two inspectors across a meeting table in Harare, representing POTRAZ compliance inspections
An inspection asks for evidence, not intentions.

A POTRAZ inspection will ask whether you are licensed, who your data protection officer is and whether they are certified, what personal data you hold and why, how it is secured, and how you handle breaches and data subject requests. Health, genetic and biometric data carry extra conditions, and transfers outside Zimbabwe need a lawful basis.

We confirm your licence tier, support the data protection officer, build the records, policies and breach procedures, and run a mock inspection so the real one holds no surprises.
Mining: safety and operational technology

A safety officer and an engineer talking beside an open-pit lithium mine in Zimbabwe at golden hour, representing ISO 45001 and security for Zimbabwe's platinum and lithium mines
Lithium is now one of Zimbabwe’s largest exports.

Zimbabwe exported 1.128 million tonnes of lithium concentrate in 2025, and new processing plants are being built ahead of a ban on concentrate exports from 2027. Platinum producers such as Zimplats and Mimosa already hold ISO 45001, and POTRAZ has named mining companies among the first sectors to be inspected. The July 2024 cyber attack on Sibanye-Stillwater, a co-owner of Mimosa, showed how incidents at a parent group reach local operations.

We help mines build ISO 45001 safety management systems, secure processing plants and remote access with IEC 62443, and meet their data protection duties for employee and contractor data. See our ISO 45001 consulting and operational technology security assessments.
Banks, fintechs and payment security

A shop owner accepting a mobile wallet payment from a customer at a small grocery counter in Harare, representing payment security for Zimbabwe's banks and fintechs
Digital payments are growing fast, and fraud with them.

The Reserve Bank of Zimbabwe expects banks and payment system providers to run board overseen cyber security programmes with a CISO, third party risk management, periodic audits and incident reporting, and the Governor has warned about weaknesses in third party providers and digital banking. Zimswitch has achieved PCI DSS compliance and EcoCash Holdings became the first Zimbabwean fintech certified to ISO 27001, which raises expectations for everyone connected to them.

We run gap assessments against RBZ expectations, PCI DSS scoping and readiness, and incident response planning. See our PCI DSS compliance advisory and cyber security maturity assessments.

ISO 27001, healthcare and AI governance

  • ISO 27001: SAZ Certification Services is SADCAS accredited for ISO/IEC 27001:2022, so local certification is available alongside international bodies. See our ISO 27001 implementation.
  • Healthcare: the Impilo electronic health record now runs in more than 1,100 health facilities, and POTRAZ has named healthcare providers among the first sectors to be inspected.
  • AI governance: our ISO 42001 consulting helps organisations govern AI ahead of the regulation the National AI Strategy proposes.

GRCLens: one platform to run your GRC function

Consulting gets you compliant. GRCLens, the governance, risk and compliance platform we built and use on every engagement, keeps you compliant. It orchestrates your regulatory and legislative compliance in one place, so your risk, compliance and audit teams work from the same controls, evidence and numbers.
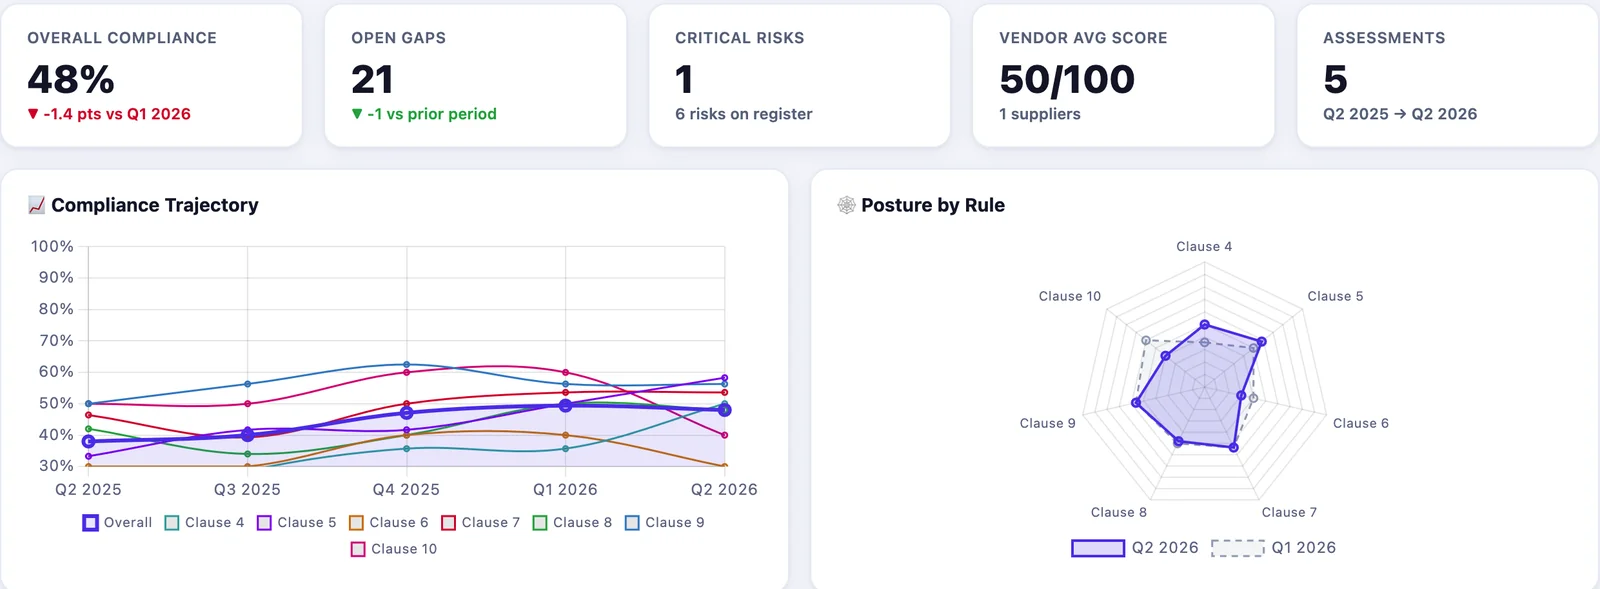
GRCLens board dashboard showing overall compliance, open gaps, critical risks, a compliance trajectory across five assessments and posture by clause
The GRCLens board view: compliance trend, open gaps, critical risks and posture by requirement.
  • Local law and international standards side by side. the Cyber and Data Protection Act sit in GRCLens next to ISO/IEC 27001, ISO/IEC 42001, ISO 45001, ISO 22000, PCI DSS, SOC 2 and IEC 62443, each with its own requirement catalogue.
  • Map once, comply many times. A shared control model reuses one piece of evidence against every obligation it satisfies, instead of collecting it again for each regulator.
  • Assurance built in. Every local framework carries an Assurance domain for audits, reviews and control monitoring, so you can show controls work, not just that they are documented.
  • Risks, indicators and suppliers. A risk register with key risk indicators traced to appetite, follow-up actions with owners and dates, and third-party assessments with vendor scores.
  • Board ready. Dashboards show the compliance trajectory, open gaps and critical risks, with an AI executive briefing and PDF and Word reports for the board and the regulator.
  • Hosted where your data must stay. GRCLens can run on premises in your own data centre or in a cloud region you choose.

See GRCLens for Zimbabwe, or request a GRCLens demo.

How we work with organisations in Harare

  • Remote first, on site when it matters. Our consultants run gap assessments, policy work, risk workshops and evidence reviews remotely, and we work with a local partner firm for on-site walkthroughs, interviews, audits and plant visits in Harare.
  • One programme, many obligations. We map your controls once and reuse the evidence across local law, ISO standards, PCI DSS and your customers’ security questionnaires, instead of running a separate project for each.
  • Consulting and platform together. We configure GRCLens with your obligations, controls and evidence during the engagement, so your own team runs the programme after we hand over, with our consultants on call for audits and regulatory change.
  • Fixed scope, fixed quote. After a short scoping call you receive a written scope, timeline and price.

We also support organisations in Johannesburg, Cape Town, Nairobi and Lusaka.
Frequently asked questions

Data controllers that process personal data in Zimbabwe need a licence under SI 155 of 2024, with the fee tier set by the number of data subjects. Licences last 12 months and should be renewed three months before expiry.

GRCLens is the governance, risk and compliance platform we built and use on every engagement. It holds your obligations, controls, evidence, risks and board reporting in one place. Many clients keep using it after the project to run their compliance programme, but our consulting does not depend on it.

Data controllers must appoint a data protection officer and notify POTRAZ within 90 days, and the officer must complete a certification course approved by POTRAZ.

Under SI 155 of 2024, breaches are reported to POTRAZ within 24 hours and to affected data subjects within 72 hours.

Expect questions about your licence, your data protection officer, what personal data you hold and why, how it is secured, how you handle breaches and requests, and any transfers outside Zimbabwe.

We deliver most work remotely and use a local partner firm for on-site interviews, mock inspections and audits in Harare and at mine sites.

Talk to us about cyber security in Zimbabwe

Tell us where you are today and what you need to achieve. We will come back with a clear scope, timeline and fixed quote.