
Security Solution Consultants (SSC) runs the kind of cyber security audit Perth agencies, utilities and resources suppliers can put in front of a board, an agency customer or the Office of the Auditor General. We work from Tarneit, in Melbourne’s west, deliver most fieldwork remotely, and fly in for the parts that need eyes on the ground: operational technology, physical security, data centres and the findings walkthrough.
Each audit is measured against the instrument that created the question, whether that is the 2026 WA Government Cyber Security Policy, the Essential Eight, ISO/IEC 27001, the SOCI Act or a clause in a contract. That choice decides the scope, the effort and what the report will be worth to the person reading it.
Who in Perth is asking for audits, and why
State agencies facing the Auditor General. The Office of the Auditor General’s information systems audit results for 2025 (Report 7: 2025-26) counted 359 findings across 53 entities, and about two thirds had been raised in earlier years and were still open. Under Premier’s Circular 2025/13, agencies now pass the Auditor General’s letters to DGov within seven days, so repeat findings are seen centrally. An internal audit before the next OAG visit is a cheaper place to find gaps in access management and endpoint security, the two areas where fewer than a quarter of entities met the benchmark.
Microsoft 365 tenancies. The Auditor General’s Microsoft 365 security controls report of 6 March 2026 made tenancy configuration an audit topic in its own right. We review conditional access, administrator roles, logging and external sharing settings against the WA policy and the Essential Eight.
Universities, TAFEs and member bodies. The Auditor General published information systems results for universities and TAFEs on 22 May 2026, and the password data breach at UWA in August 2025 is recent memory. Professional bodies hold sensitive member data too: the Legal Practice Board of WA was subject to unauthorised access on 21 May 2025. For these organisations an independent look at identity, access and third-party controls is a practical starting point.
Suppliers to WA agencies. Clause 3.4 requires a cyber risk assessment for every procurement where the supplier will touch agency data or systems. Suppliers who commission their own audit first can answer with a report rather than a promise.
Energy, water, ports and resources. Responsible entities under the SOCI Act owe their board-approved annual report by 28 September, and the enhanced CIRMP rules that commenced on 10 June 2026 add items as their 12 and 24 month grace periods end. A SOCI audit in WA gives directors evidence before they sign.
Compliance audit, technical assessment or penetration test
These three are often sold under one name, but they answer different questions. A compliance audit asks whether you meet a stated requirement, such as the WA Essential Controls or ISO 27001 Annex A, and produces findings against each clause. A technical assessment looks at how your systems are really configured, from patch levels to firewall rules and cloud settings, and lists weaknesses by risk. A penetration test goes deeper on a narrow target and tries to exploit what it finds. Only the first will satisfy an agency, a certification body or a SOCI board report. The other two are valuable inputs, and we often pair a light technical assessment with an audit so findings rest on evidence rather than interviews alone. If a penetration test is what you need, see our penetration testing and security testing services.
How a Perth cyber security audit runs
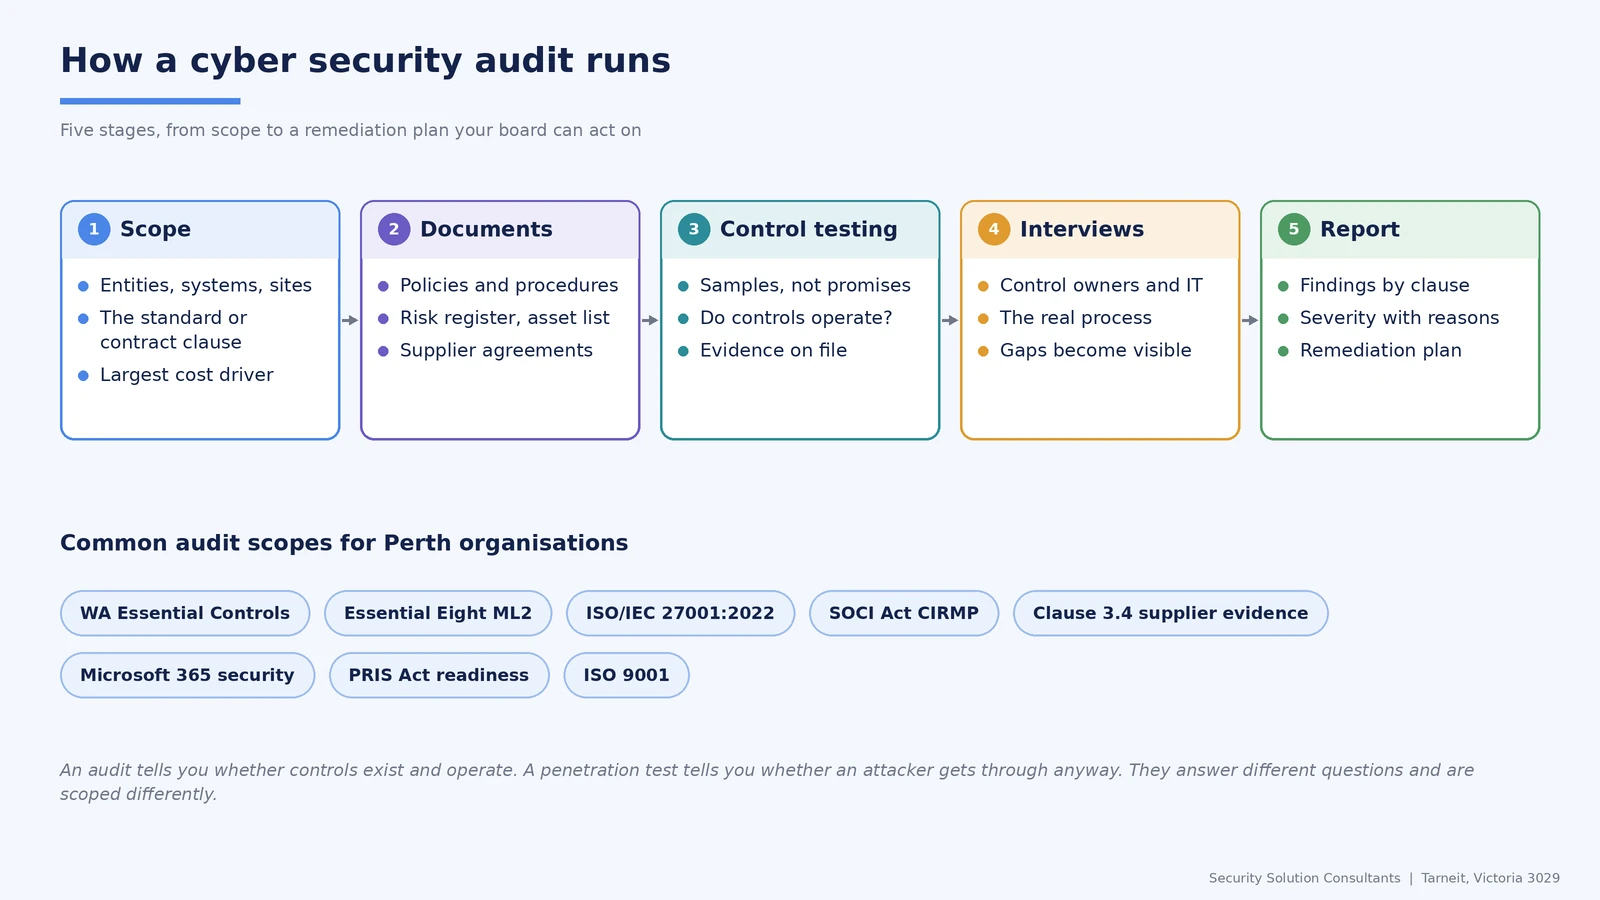
1. Scope. We fix the entities, systems, sites and the standard in a short scoping call. For WA agencies we usually anchor on the 13 Essential Controls; for suppliers, on the agency’s clause 3.4 questions.
2. Documents. Policies, the asset register, risk assessments, incident procedures and supplier contracts. Missing documents are recorded as findings, not worked around.
3. Control testing. We sample evidence that controls operate: patch records, access reviews, MFA enrolment, backups and restore tests, logging. Configuration exports from Microsoft 365 or your cloud tenancy are reviewed directly.
4. Interviews. Short sessions with control owners, IT staff and managed service providers to test whether the process on paper is the process in practice, including how an incident would actually reach DGov within 6 hours.
5. Report. Findings rated by risk and mapped clause by clause, with a remediation plan and a walkthrough for the people who will fix them.
Which standard to audit against in Western Australia
- 2026 WA Government Cyber Security Policy. The 13 Essential Controls, governance and reporting obligations, AI controls, and the milestones for legacy transition plans and post-quantum readiness.
- Essential Eight assessment in Perth. Maturity Level Two testing against the ASD maturity model, mapped to the new ASD Essentials actions.
- ISO 27001 internal audit for Perth organisations. The internal audit the standard requires, or a readiness review before an accredited certification body arrives.
- SOCI CIRMP audit. For WA energy, water and port operators, using the WA policy, AESCSF or the Essential Eight as the cyber framework.
- PRIS Act readiness. Agency and contractor controls against the Information Privacy Principles ahead of breach notification on 1 January 2027.
- SOC 2 readiness. A pre-examination review before a licensed CPA firm begins its work.
- PCI DSS v4.0.1. Readiness ahead of a QSA assessment or self-assessment questionnaire.
- A clause in your contract. If a resources company or agency has written a security schedule, we audit to that schedule and nothing wider.
Deliverables, timing and price
What you receive. A summary your executive team can read in ten minutes, a detailed findings register mapped to the standard, a prioritised remediation plan with suggested owners, and a walkthrough session. If you use GRCLens, findings and evidence load straight into it for next year.
How long. For a single entity with one environment, fieldwork is measured in days and the report follows within an agreed window. Groups, OT sites and multi-framework scopes take longer, and slow evidence requests are the usual cause of delay.
What it costs. We price on scope, not headcount, and give a fixed quote after a discovery call. The quickest way to lower the price is to narrow the scope to what the requirement covers. If you need certification, the certification body is a separate cost: no one should sell you both the preparation and the certificate.
Western Australian specifics that change the scope
The six hour clock. WA agencies must report incidents to DGov within 6 hours and confirmed incidents to the ACSC within 12 hours, and clause 3.4 asks suppliers whether they can support that. We test detection, escalation and contact paths, not just the written procedure.
Where your data lives. Clause 3.5 bars offshoring of Tier 1 Risk information. Audits for agency suppliers therefore cover data location, backup regions, offshore support access and subprocessors.
A separate electricity market. WA’s Wholesale Electricity Market sits outside the NEM, and AEMO’s AESCSF criticality tool covers WEM participants. For energy businesses we agree early whether the CIRMP evidence will rest on AESCSF or on the WA policy, which the Cyber and Infrastructure Security Centre has accepted as an equivalent framework.
Audits across Western Australia
Remote delivery means distance does not change the method. Organisations in Fremantle, Joondalup, Mandurah, Bunbury, Geraldton, Kalgoorlie, Karratha and Port Hedland get the same scope, testing and report as a client in the Perth CBD. We travel for OT sites, port and mine infrastructure, and physical security. If you need ongoing advice rather than a point-in-time review, see our cyber security consulting for Perth and Western Australia.
Frequently asked questions
Can you test us against the 13 Essential Controls in the WA policy?
Yes. We assess each Essential Control, including the Essential Eight at Maturity Level Two and the five further ASD strategies, and record where you sit against the policy’s milestones: legacy transition plans by the end of 2027, a post-quantum transition approach by December 2027 and every Protect domain control by December 2028. The report shows what is done, what is planned and what is missing.
How should a WA agency prepare for its next OAG information systems audit?
Start with last year’s letter. The Auditor General found that about two thirds of its 2025 findings had been raised before, so closing old items is the quickest gain. We retest those findings, then the areas where fewer than a quarter of entities met the benchmark, access management and endpoint security, and give you evidence of what has changed before the auditors arrive.
Do you review Microsoft 365 configuration as part of an audit?
Yes, when it is in scope. Since the Auditor General’s Microsoft 365 security controls report of 6 March 2026, a tenancy review is a natural part of a WA audit. We check identity and conditional access, privileged roles, audit logging, external sharing and email protections against the WA policy and the Essential Eight, and report each gap with the configuration change needed to close it.
Is a SOCI audit in WA a legal requirement?
No. The SOCI Act requires a critical infrastructure risk management program and a board-approved annual report by 28 September, not an external audit. Directors still need a basis for approving that report, especially as new CIRMP items arrive when the 12 and 24 month grace periods that started on 10 June 2026 run out. An independent audit gives them that basis.
Does your ISO 27001 internal audit lead to certification?
It is a step towards certification, not the certificate itself. The standard requires an internal audit, and ours tests every clause and the Annex A controls you have selected. Certification is then performed by an accredited certification body, independently of us. We can support you through its stage one and stage two audits and help close any nonconformities it raises.
Can you audit sites in the Pilbara or the Goldfields?
Yes. Most of the work happens remotely, including document review, configuration testing and interviews. We visit when the scope needs it: processing plants, port facilities, control rooms and other operational technology, physical security, or a findings session with site leadership. Travel is quoted separately so you can see exactly what the on-site component adds.
How soon can an audit in Perth start?
Once scope is agreed, the start date depends mostly on how quickly you can share documents and book interviews. If a deadline is driving the request, such as the 28 September SOCI report or an agency tender closing date, tell us at the start and we will plan the fieldwork backwards from it so the report lands in time.
Next step
Send us the clause, letter or question that started this, and we will tell you which kind of audit it needs and what it will cost. Get in touch or email info@secsolutionshub.com.

