
Security Solution Consultants (SSC) carries out each cyber security audit Tasmania organisations ask us for, from Hobart agencies to Launceston manufacturers and north west food processors, against the instrument that actually binds them. We are based in Tarneit, in Melbourne’s west, run most fieldwork remotely, and cross Bass Strait for the work that needs a site visit: operational technology, physical security, data centres and findings walkthroughs.
That instrument might be the Tasmanian Government Cyber Security Policy, INFOSEC-3 of the TAS-PSPF, ISO/IEC 27001, the SOCI Act, ISO 22000 or a customer’s contract. Choosing it correctly is what makes the audit useful.
Who in Tasmania is asking for audits, and why
Agencies after the Auditor-General’s August report. Audit Tasmania’s report of 12 August 2026 on State entities recorded repeated cyber and IT weaknesses, 227 new findings and 266 still unresolved. An internal view of where an agency stands against the Tasmanian Government Cyber Security Standards, taken before the next audit cycle, also gives it a defensible input to the annual report to the Secretaries Board.
Agencies managing contractors. The same report found the Department of Health’s engagement of an ICT contractor did not comply with Treasurer’s Instruction PF-3. Contractor engagement and oversight is now worth auditing in its own right.
Cloud and IT suppliers. Under INFOSEC-3, outsourced IT and cloud services are expected to have an IRAP assessment and contracts must carry security terms. Before an ASD-endorsed assessor is engaged, suppliers benefit from a readiness audit against the ISM.
Anyone running third-party file transfer or integration tools. The 2023 Clop attack through GoAnywhere at the Department for Education, Children and Young People leaked about 16,000 documents. Our audits now include an inventory of internet-facing third-party software and how quickly it is patched.
Energy, water and ports. TasNetworks, Hydro Tasmania, TasWater and TasPorts sit at the centre of the state’s critical infrastructure. Responsible entities and their suppliers use a SOCI audit to give directors evidence before the 28 September annual report.
Food exporters. Processors working to ISO 22000 or FSSC 22000 need internal audits anyway. Adding the cyber controls that protect traceability and plant systems makes one visit do two jobs.
Software and managed service firms. Hobart software businesses selling to mainland and overseas customers meet SOC 2 and ISO 27001 questionnaires long before they hold either. A readiness audit shows which answers they can already evidence and which gaps to close before a CPA firm or certification body is engaged.
Audit, technical review or penetration test?
Think of it as three questions. An audit asks “do we meet the requirement?” and checks your controls against a named standard, such as the state’s Cyber Security Standards or ISO 27001, producing clause-referenced findings that an agency, certification body or board can accept. A technical review asks “how exposed are our systems?” and inspects configurations, patching, identity and exposed services directly, producing a ranked list of weaknesses. A penetration test asks “can someone actually get in?” and tries, within agreed limits, against a defined target. Contracts and regulators want the first. The other two strengthen it, and we often add focused technical checks to an audit so findings rest on evidence, not on what people remember. If a penetration test is what you need, see our penetration testing and security testing services.
The five stages of a Tasmanian audit
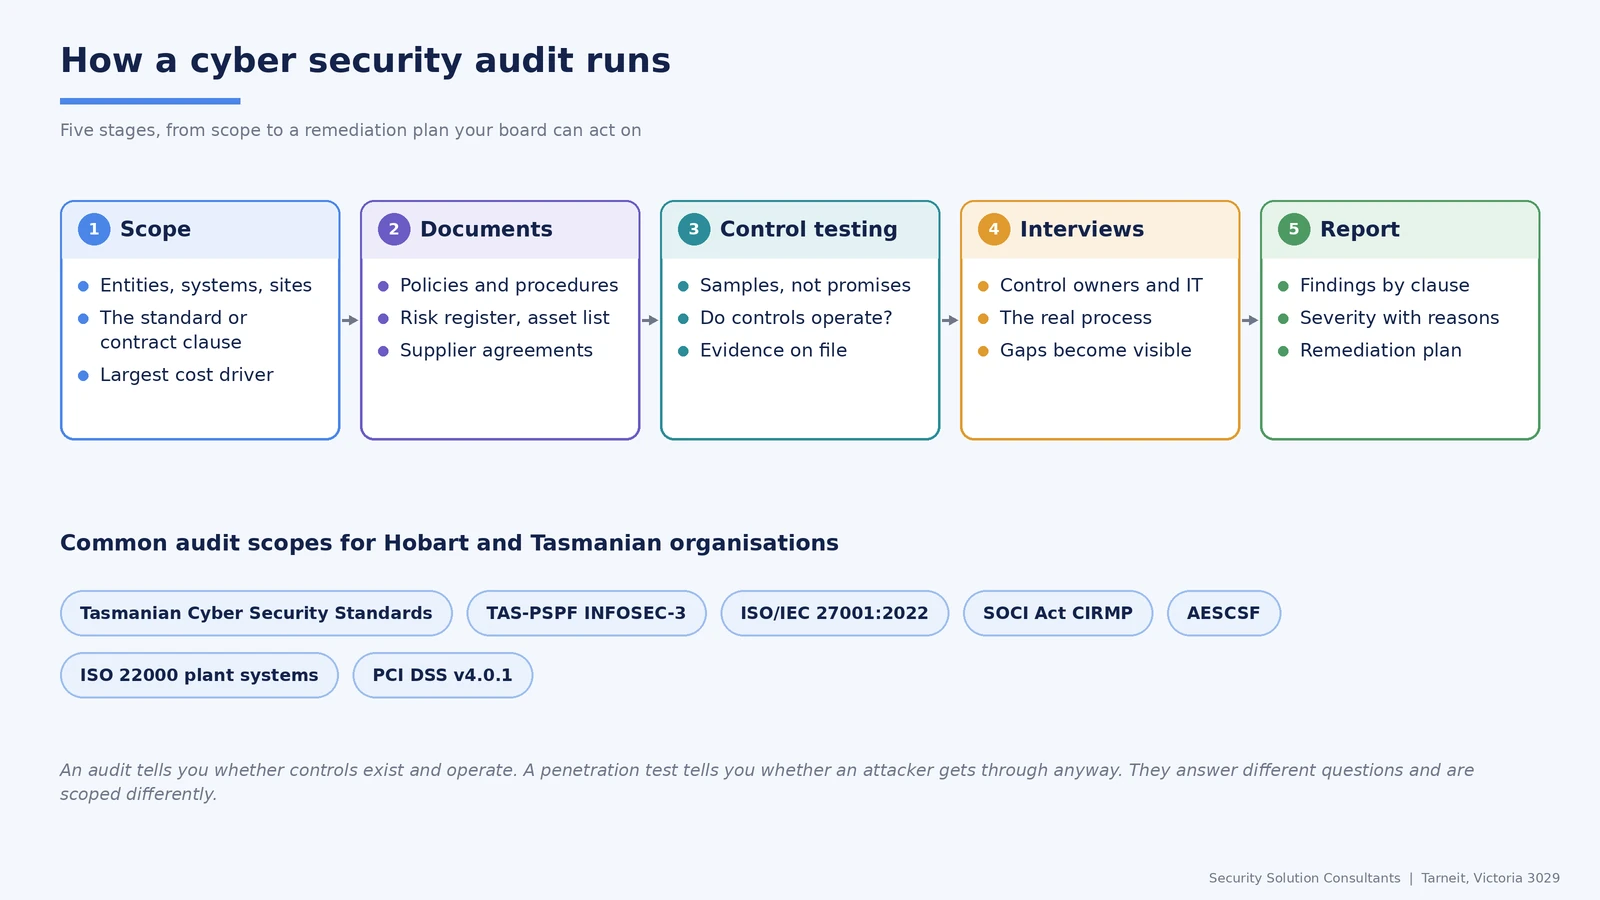
Scope. We agree the entities, systems, sites and the standard. For agencies that is usually the state policy and Standards; for suppliers, the INFOSEC-3 contract terms; for food exporters, ISO 22000 plus plant systems.
Documents. Policies, risk assessments, asset registers, contracts with IT providers, incident procedures and, for agencies, last year’s audit letters.
Control testing. Evidence that controls run in practice: account reviews, MFA, patching of internet-facing software, backups and restores, logging, and supplier access.
Interviews. Short sessions with system owners, IT staff, contractors and plant engineers to see whether daily practice matches the documents.
Report. Findings rated and mapped to clauses, with a remediation plan and a walkthrough for the people who will act on it.
Choosing the yardstick in Tasmania
- Tasmanian Government Cyber Security Policy v1.1 and Standards. For Schedule 1 agencies, including incident notification to the Government CIO and annual reporting.
- TAS-PSPF v2.1 INFOSEC-3. Authorisation to operate, supply chain security, contract terms and IRAP readiness for outsourced IT and cloud.
- ISO 27001 audit in Tasmania. Internal audit against AS ISO/IEC 27001, the standard the state policy names, or readiness for certification.
- Essential Eight and ASD Essentials. Where a Commonwealth contract, Defence prime or insurer asks for maturity evidence.
- SOCI CIRMP and AESCSF. For NEM participants and other responsible entities, plus assurance over their suppliers.
- ISO 22000 and FSSC 22000. Internal audits that include the systems behind traceability and recall.
- SOC 2 readiness. For Tasmanian software firms preparing for a licensed CPA firm’s examination.
- Personal Information Protection Act 2004. Privacy controls for agencies and for the contractors treated as personal information custodians.
Outputs, timing and fees
Outputs. An executive summary, a findings register mapped to the chosen standard, a remediation plan with priorities and owners, and a walkthrough. If you use GRCLens, findings load into it for tracking.
Timing. Fieldwork for a contained scope runs over a few days and reporting follows. Multi-site, OT or multi-framework audits take longer, and the speed of evidence requests is the factor you control.
Fees. We quote a fixed fee once scope is agreed. Remote delivery limits travel to the visits that matter, and narrowing scope to what your contract or regulator asks for is the biggest saving. Certification audits and IRAP assessments are separate, carried out by an accredited certification body or an ASD-endorsed assessor.
Tasmanian specifics that change the scope
IRAP for cloud and outsourced IT. INFOSEC-3 makes IRAP the expectation for these services. An audit of an agency or its supplier therefore checks which cloud services are in use, whether each has an IRAP assessment, and what is missing.
No state breach scheme, but custodians include contractors. PIPA treats contractors under a personal information contract as custodians, yet the state has no mandatory notification scheme. We test incident response against your contracts and, for private organisations, the Commonwealth Notifiable Data Breaches scheme.
An island with few links. Basslink is the electricity link to the NEM, with Marinus Link still planned, and freight runs through TasPorts. Continuity, recovery and supplier dependency carry more weight in a Tasmanian scope than they might on the mainland.
Audits across Tasmania
We audit organisations in Hobart, Kingston, Glenorchy, Launceston, Devonport, Burnie, the Huon Valley and the north west coast with the same remote method, travelling when plant, OT or physical security is in scope. Where an organisation has sites in both the south and the north of the state, we plan any visits so one trip covers them. For ongoing advice, certification support and SOCI programs, see our cyber security services in Hobart and Tasmania.
Frequently asked questions
Can you assess an agency against the Tasmanian Government Cyber Security Standards?
Yes. We test a Schedule 1 agency’s controls against the Tasmanian Government Cyber Security Policy v1.1 and its Standards, including incident notification to the Government Chief Information Officer and the evidence behind the annual report to the Secretaries Board. Where the agency also works to AS ISO/IEC 27001, we map findings to both so one audit serves both purposes.
Does our cloud service need an IRAP assessment to support a Tasmanian agency?
Under INFOSEC-3 of TAS-PSPF v2.1, outsourced IT and cloud services are expected to have one. Only ASD-endorsed assessors can perform IRAP assessments, so we do not. We run a readiness audit against the ISM first, fix the gaps with you, and organise the evidence so the assessor’s engagement is shorter and more predictable.
What should we check after the 2023 GoAnywhere incident?
Look at every internet-facing tool you depend on that someone else wrote, especially file transfer, remote access and integration software. Confirm you know it exists, who patches it and how fast, what data passes through it, and how you would detect misuse. The Department for Education, Children and Young People incident showed that one supplier product can expose a very large volume of records.
Can a food processing plant’s control systems be part of the audit?
Yes. We review how plant networks are separated from office IT, who has remote access, how changes are controlled, and whether traceability and recall records are backed up and recoverable. For processors working to ISO 22000 or FSSC 22000, we align these checks with the food safety internal audit so you prepare once for both.
How is an ISO 27001 internal audit different from the certification audit?
An internal audit is one you commission to check your own management system, and the standard requires it. The certification audit is carried out by an accredited certification body, which decides whether to certify you. We perform the first and help you prepare for the second, but we cannot do both for the same organisation, and no one should.
Does anyone need to fly in for a Hobart audit?
Usually not. Documents, configuration evidence and interviews can all be handled remotely, which keeps costs down for Tasmanian clients. We travel when the scope includes physical security, plant or operational technology, a data centre, or when you want the findings presented in person to your executive or board.
What does a cyber security audit in Tasmania cost?
The fee depends on scope: the number of entities, systems and sites, the standard, and whether OT or travel is involved. We confirm scope in a short call and then give a fixed price. Narrowing the audit to what your agency contract, SOCI program or customer actually requires is the most effective way to keep it affordable.
Next step
Send us the policy clause, contract term or audit letter behind your request, and we will tell you what type of audit fits and what it will cost. Get in touch or email info@secsolutionshub.com.

