
A cyber security audit Darwin organisations can put in front of Defence, a SOCI board, an NT Government agency or a prime contractor has to test what is actually in place, not restate policy. Security Solution Consultants (SSC) runs those audits from Tarneit, Victoria 3029, with most fieldwork done remotely and site visits in Darwin when operational technology, physical security or port systems need to be seen in person.
Who is asking for audits in the Top End
Defence suppliers. With the Marine Rotational Force Darwin at about 2,000 personnel in 2026, and a national commitment of $13 to $16 billion over ten years to harden northern bases, local firms bidding for that work meet Defence’s security expectations early. Primes and Defence ask for DISP membership and Essential Eight Maturity Level Two on corporate ICT used with Defence, and an audit is the sensible way to find the gaps before they do.
Critical infrastructure operators. The Port of Darwin and Power and Water Corporation run assets in sectors covered by the SOCI Act, and the LNG operations at Bladin Point and Darwin LNG run complex OT with large contractor supply chains. Directors approving the CIRMP annual report by 28 September benefit from an independent view first, particularly now that the enhanced CIRMP rules of 10 June 2026 have raised the baseline.
Contractors to the NT Government. Under the Information Act 2002 (NT), contract service providers are treated as part of the agency for the contracted work, so agencies want assurance that suppliers handle personal information under the Information Privacy Principles. The NT Health case, where 3,277 patient records went to a vendor during a 2019 upgrade, shows why.
Health and essential services after the October outage. The 8 October 2026 NT Government network outage was not an attack, but it pushed hospitals onto continuity plans. It is a reasonable prompt for organisations that rely on the same networks to have continuity and recovery arrangements reviewed alongside a cyber audit.
Three kinds of security review
A compliance audit measures you against a stated yardstick, such as a SOCI CIRMP, DISP, ISO 27001 or a contract schedule, and tells you where you fall short of each requirement. A technical assessment examines the systems themselves: firewall rules, remote access paths into OT, account permissions, patch levels and backup recovery. A penetration test is an authorised attack that tries to exploit what it finds within an agreed window. Each answers a different question. Boards and regulators usually want the first, engineers often want the second, and the third is best used to confirm that fixes work. In live OT environments active testing needs careful planning with site engineers, so passive review often takes its place. If a penetration test is what you need, see our penetration testing and security testing services.
How an audit runs in Darwin
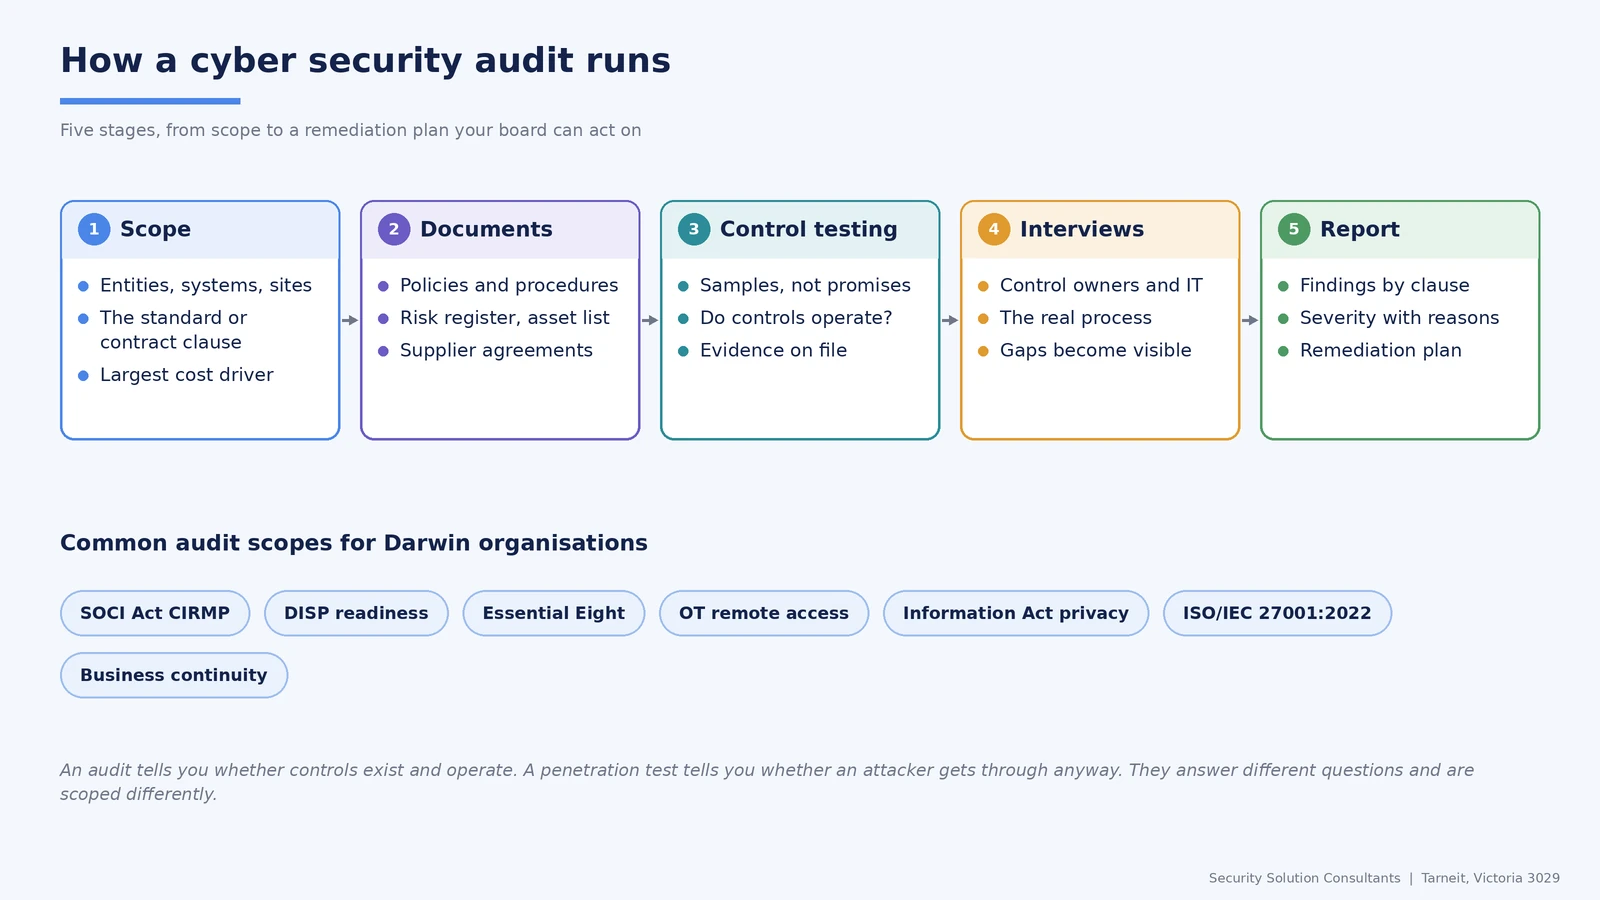
1. Scope. We agree the entities, sites and yardstick. For a port or energy business this includes deciding whether OT is in or out, and which remote sites need a visit.
2. Documents. Your CIRMP, policies, network diagrams, supplier contracts, access lists and continuity plans, requested in one list at the start.
3. Control testing. Sampled testing of whether controls operate: user access reviews, patch records, backups that restore, and supplier remote access that is logged and time-limited.
4. Interviews. Control owners, IT staff, OT engineers, contract managers and, for DISP, the people responsible for personnel and physical security.
5. Report. Findings rated by severity and mapped to the yardstick, a remediation plan with owners, and a walkthrough in Darwin or online.
Standards we audit against in the NT
- SOCI Act CIRMP and the enhanced CIRMP rules. Including the items on 12 and 24 month grace periods and a framework uplift such as Essential Eight Maturity Level Two or AESCSF. See our SOCI Act audit and compliance service.
- DISP readiness. Governance, personnel, physical, and ICT and cyber security, tested before you apply to Defence.
- Essential Eight and ASD Essentials. Maturity assessment, mapped to the Essentials enterprise IT and OT chapters. See our Essential Eight assessment.
- Information Act 2002 (NT). A review of how a contract service provider handles agency personal information against the 10 Information Privacy Principles.
- PSPF Release 2026. For Commonwealth entities with Territory operations.
- ISO 27001 internal audit. The audit the standard requires before and between certification body visits. See ISO 27001 advisory.
- ISO 9001 and ISO 22000 internal audits. For Defence, construction and food suppliers. See ISO 9001 and ISO 22000 consulting.
- Business continuity. A review of plans, recovery times and the last real exercise. See business continuity management.
What the audit produces
A findings report against the yardstick you chose, with evidence references, the reasoning behind each severity and practical fixes; a short summary a board or contract manager can read in ten minutes; and a session to go through the results with the people who will fix them. Findings can also be loaded into GRCLens so remediation is tracked against the same controls next time.
Timeframes
Fieldwork for a single business with a clear scope is usually measured in days. OT sites, several locations or a combined DISP and ISO 27001 review add time, mostly for travel and evidence gathering. OT evidence tends to take longest to collect, because it often sits with engineers or maintenance contractors rather than the IT team.
Cost
Each audit is a fixed quote after scoping. Travel to Darwin or regional sites is built into that quote, so the number does not move once fieldwork starts. The number of sites, whether OT is in scope and how many frameworks the findings must map to are what move the price. If you need certification, the accredited certification body is a separate engagement you contract directly.
Northern Territory specifics that change the scope
Distance shapes the plan. Sites in Katherine, Alice Springs or remote communities cannot always be visited cheaply. We test as much as possible remotely and reserve travel for OT, physical controls and the findings session.
The government policy is not public. Because the NT Government’s cyber security policy is not published, the yardstick for a Territory supplier is usually the contract and any security schedule or questionnaire the agency issues. We start from those documents rather than a generic checklist.
Third parties hold the data and run the systems. From the NT Health vendor incident to remote OT support at energy sites, much NT risk sits with suppliers. We extend testing to supplier access paths and contract terms, not only your own network.
Audits across the Northern Territory
We audit organisations in Darwin, Palmerston, Katherine, Alice Springs and remote communities, mostly online with planned site visits. Interviews run by video, evidence moves through a secure share, and on-site days are planned around your site access rules and shift patterns so operations are not interrupted. For ongoing advice, compliance programs and certification support, see our page on cyber security compliance and consulting in Darwin and the NT.
Frequently asked questions
What should a Darwin Defence supplier audit before applying for DISP?
All four DISP domains: governance, personnel security, physical security, and ICT and cyber security. On the ICT side, Defence expects Essential Eight Maturity Level Two on the corporate systems you use with Defence, so an Essential Eight assessment is the core. An ISO 27001:2022 certificate can partly evidence that domain. Defence decides membership; the audit tells you whether you are ready to apply.
Is an external SOCI audit required for Northern Territory operators?
The SOCI Act does not require an external audit. It requires responsible entities to maintain a critical infrastructure risk management program and give a board-approved annual report by 28 September. With the enhanced CIRMP rules in force since 10 June 2026, an independent audit gives directors evidence that the program works before they sign.
Can you audit OT at a Darwin site without disrupting operations?
Yes. OT audits rely mainly on document review, configuration exports, network diagrams, interviews with engineers and observation on site. We do not run active scanning on live control systems unless your engineers agree and there is a rollback plan. Much of the value comes from reviewing remote access, segmentation and supplier accounts, which can be done safely.
How do you audit a contract service provider under the NT Information Act?
We map the personal information you hold under the contract, then test how you collect, use, store, disclose and dispose of it against the 10 Information Privacy Principles in the Information Act 2002 (NT), and against any extra terms in the contract. We also check who else, such as a software vendor, can reach that data.
How much travel to Darwin does an audit need?
Often one trip, sometimes none. Document review, testing of cloud and corporate systems, and most interviews work online. We plan a visit when OT, physical security or port systems are in scope, or when you want the findings presented in person, and we build the travel into the fixed quote.
Does the October 2026 outage mean we need a continuity review?
It is a good prompt. The NT Government network outage on 8 October 2026 was not a cyber attack, yet hospitals had to move onto their continuity plans. A continuity review checks whether your plans set realistic recovery times, whether staff know the manual workarounds, and when the plan was last exercised. We can run it alongside a cyber audit so the findings fit together.
Can one Darwin audit cover several frameworks at once?
Yes, and in the Territory it often makes sense. A contractor may need DISP readiness, an ISO 27001 internal audit and a response to a SOCI operator’s supplier questionnaire in the same year. We test each control once and map the result to every framework in scope, which shortens fieldwork and gives you one remediation plan.
Next step
Tell us who is asking for the audit and what they named in the request, and we will reply with a scope and a fixed price. Contact us or email info@secsolutionshub.com.

