Security Solution Consultants (SSC) delivers a cyber security audit Brisbane agencies, councils and suppliers can rely on when IS18, the Queensland Privacy Principles, a customer’s SOC 2 request or an ISO 27001 certificate is on the line. We work from Tarneit, Victoria 3029, run most fieldwork remotely, and come to Brisbane for workshops, site inspections and the findings session when that helps.
Who in Brisbane is asking for audits
Queensland Government agencies. The Information and cyber security policy (IS18) moved to version 10.0.0 in June 2026 and remains mandated. At its core, agencies must implement and operate an information security management system based on the current version of ISO 27001. Control mappings and attestations built against earlier versions now need checking against the new text, and an independent audit gives the accountable officer something firmer than self-assessment to sign against.
Suppliers to agencies. The Queensland Audit Office report Managing third-party cyber security risks (Report 13: 2025-26, 26 March 2026) found that, at entities which had not assessed third-party risk, its auditors got past controls, reached corporate systems and extracted sensitive data. It made seven recommendations. Agencies responding to that report are likely to ask more of their suppliers, so a Brisbane IT provider or software vendor should be ready with evidence.
Councils. Queensland local governments, including the councils of greater Brisbane, came under the mandatory notification of data breach scheme on 1 July 2026 through the IPOLA reforms. IS18 does not bind councils, but they are encouraged to use it.
Brisbane 2032 suppliers. The Games program covers 37 venues and about 1,500 tenders over six years, advertised through ICN Gateway. Tender documents commonly ask about information security, privacy and quality controls, and an audit before bidding shows where the gaps are.
Software, METS and agrifood exporters. Brisbane SaaS firms are commonly asked for SOC 2 or ISO 27001 by enterprise and overseas customers. Queensland’s mining equipment, technology and services (METS) sector, worth about $3.8 billion and 32,000 jobs, and its agrifood exporters, at $15.6 billion in 2024-25 including $8.4 billion of beef, are commonly asked for evidence on information security and food safety.
Compliance audit, technical assessment and penetration test
It pays to name the job before you buy it. A compliance audit compares your controls with a set of written requirements, such as IS18, the QPPs, ISO 27001 or the SOC 2 trust services criteria, and reports conformity and gaps clause by clause. A technical assessment inspects how things are actually built: identity settings, endpoint hardening, cloud configuration and internet exposure. A penetration test goes further and tries to exploit weaknesses to show real impact, much as QAO’s auditors did in their third-party review. Agencies attesting under IS18 and customers asking for SOC 2 want the first; the second and third help you fix problems and prove the fixes hold. If a penetration test is what you need, see our penetration testing and security testing services.
How a Brisbane audit runs
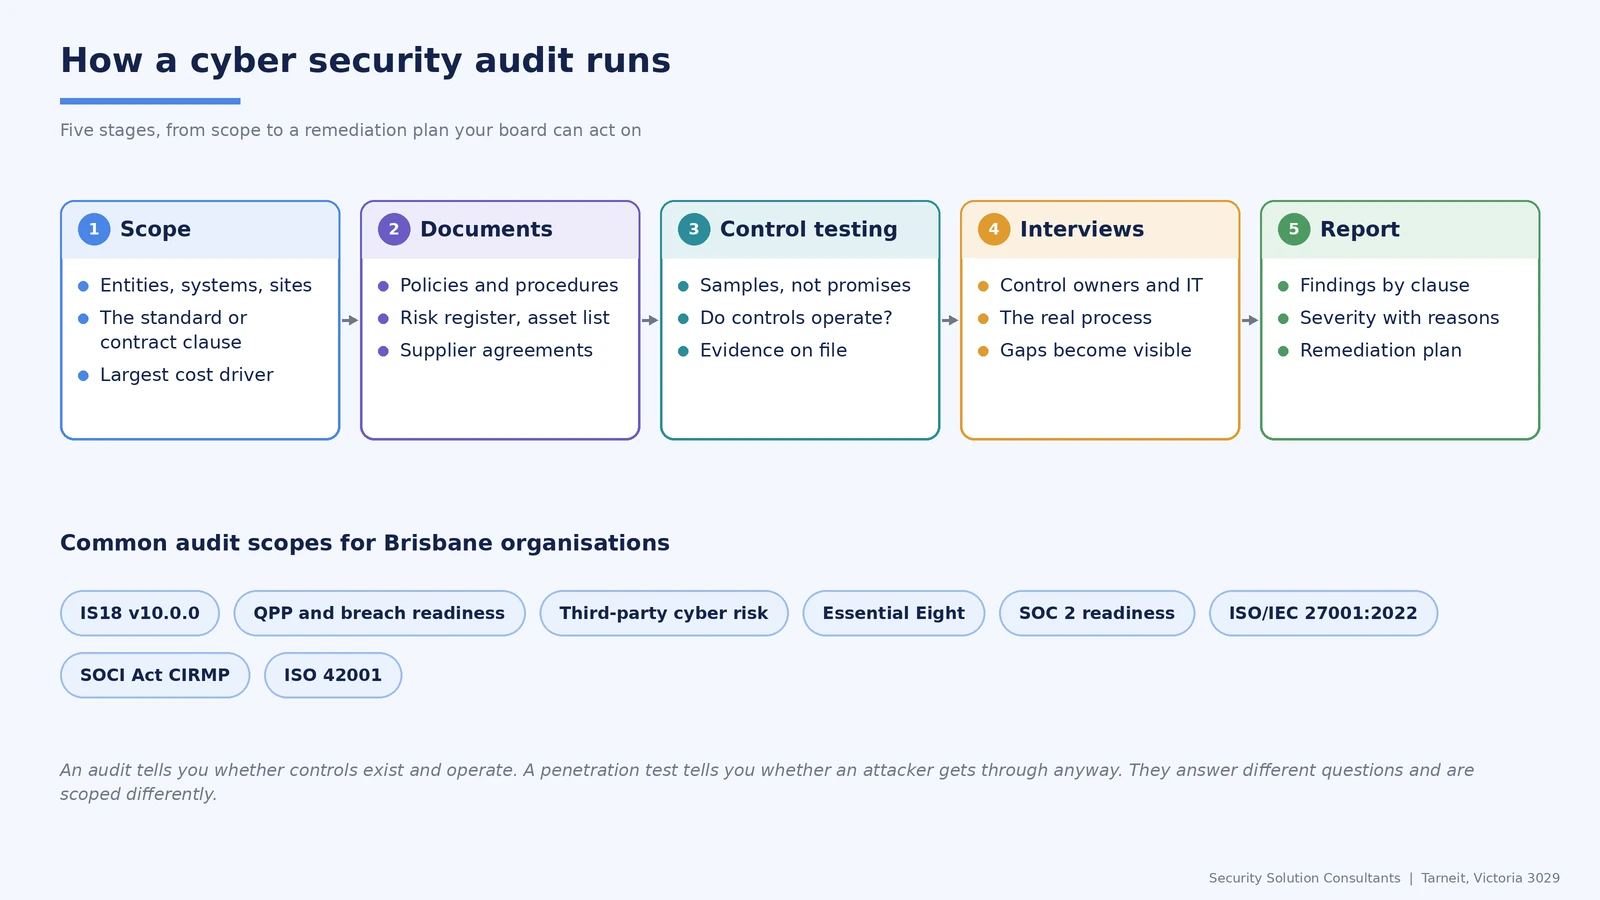
Scope: the entity, systems and yardstick, written down and agreed before fieldwork. For an agency this might be the ISMS boundary; for a supplier, only the systems that touch the customer’s data.
Documents: the ISMS, risk register, statement of applicability, supplier register, privacy policy and data breach response plan.
Control testing: samples covering access, passwords and authentication, the weaknesses QAO reported in Information systems 2025 (Report 6: 2025-26, 3 December 2025), plus patching, logging, backups, supplier onboarding and systems past their supported life.
Interviews: system owners, the privacy officer, IT staff and the contract managers who own supplier relationships.
Report: rated findings mapped to the standard, a remediation plan with owners and dates, and a walkthrough with your team.
Which standard to audit against in Queensland
- IS18 v10.0.0. An ISMS and controls review against the current version of the policy, supporting the accountable officer’s assurance.
- Queensland Privacy Principles and the breach notification scheme. Readiness for agencies (in force since 1 July 2025), councils (breach notification since 1 July 2026) and the contracted service providers agencies must take reasonable steps to bind to the QPPs under sections 35 and 36.
- Third-party cyber risk. A supplier risk review built around the issues in QAO’s March 2026 report. Reports are published at qao.qld.gov.au.
- Essential Eight and ASD Essentials. Maturity against the targets your agency set under IS18, mapped to ASD Essentials. See our Essential Eight assessment.
- ISO 27001. Internal audit and certification readiness; the IS18 ISMS is based on it. See ISO 27001 advisory.
- SOC 2 readiness. For Brisbane SaaS and managed service providers, before a licensed CPA firm starts its examination. See SOC 2 readiness consulting.
- ISO 42001. Queensland’s AI governance policy is aligned to ISO/IEC 38507 and treats ISO 42001 as a supporting tool; we audit AI management systems against 42001. See ISO 42001 consulting.
- SOCI CIRMP. For energy, water and port operators, including the enhanced CIRMP rules. See SOCI Act audit.
- ISO 9001 and ISO 22000. Internal audits for METS suppliers, Games tenderers and food exporters. See ISO 9001 and ISO 22000 consulting.
What you get
A report that ties each finding to the clause, principle or criterion it relates to; a severity rating with the reason; a remediation plan your team can schedule; and a plain-language summary for the accountable officer, board or customer. For IS18 work we also note which findings affect the annual attestation.
Duration
Most single-entity audits complete fieldwork within a couple of weeks of the evidence arriving. Agency ISMS reviews, multi-site businesses and combined SOC 2 and ISO 27001 readiness work run longer.
Cost
We fix the price after scoping. Scope breadth, the number of frameworks and the state of your documentation drive cost more than staff numbers. Certification audits by an accredited body, SOC 2 examinations by a CPA firm and PCI assessments by a QSA are separate engagements you contract directly.
Queensland specifics that change the scope
IS18 changed in June 2026. Version 10.0.0 replaced the earlier text, so an audit should test against the current policy rather than a mapping built for the 2018 or 2025 versions. Agencies that last mapped their controls before June 2026 should expect some gaps to be paperwork rather than security, and both kinds need closing before the next attestation.
Privacy obligations now travel through contracts. Under IPOLA, agencies must take reasonable steps to bind contracted service providers to the QPPs, and councils joined the mandatory breach notification scheme on 1 July 2026. Suppliers holding Queensland public sector personal information should have breach response and QPP handling in scope.
Ageing systems and third parties are known weak points. QAO found half of the audited finance systems past their supported life, and showed what can happen when third-party risk goes unassessed. We test both directly rather than relying on policy statements.
Audits across Queensland
We audit organisations on the Gold Coast and Sunshine Coast, in Ipswich, Toowoomba, Townsville, Cairns and Mackay, and across regional Queensland, with remote fieldwork and site visits where OT or physical controls are in scope. For ongoing compliance work, including IS18 programs and certification support, see our Brisbane cyber security compliance and consulting page.
Frequently asked questions
Can SSC audit a Queensland agency’s ISMS against IS18?
Yes. IS18, now at version 10.0.0 (June 2026), requires agencies to implement and operate an ISMS based on the current version of ISO 27001. We test the ISMS and the controls behind it against the current policy text, flag anything that affects the accountable officer’s attestation, and give you a remediation plan before you sign.
Do the Queensland Privacy Principles apply to a private Brisbane business?
If you are a contracted service provider to a Queensland agency, very likely through your contract. Under IPOLA, agencies must take reasonable steps to bind contracted service providers to the QPPs under sections 35 and 36. Your general privacy duties as a private business come from the Privacy Act 1988 if it applies to you. Where the two overlap we review both in one audit.
What did QAO find about third-party cyber risk, and what does it mean for suppliers?
QAO’s report of 26 March 2026 found that at entities which had not assessed their third-party risk, its auditors got past controls, reached corporate systems and extracted sensitive data. It made seven recommendations. Suppliers should expect more questions about access to agency systems, data handling and incident notice, and be ready to answer with evidence rather than assurances.
Is a SOC 2 readiness audit in Brisbane the same as a SOC 2 report?
No. A SOC 2 report can only be issued by a licensed CPA firm after its own examination. A readiness audit comes first: we check your controls against the trust services criteria you choose, identify gaps, help you fix them and confirm evidence will be available for the observation period. It reduces surprises once the CPA firm begins.
Should Queensland councils audit their readiness for mandatory breach notification?
It is worth doing. From 1 July 2026 Queensland local governments are covered by the mandatory notification of data breach scheme under the IPOLA reforms. A readiness audit checks how a council detects, assesses, contains and notifies a breach, and whether its contractors are bound to report incidents quickly enough for the council to meet its own obligations.
Do Brisbane 2032 tenderers need a cyber security audit?
It depends on the tender. With about 1,500 tenders across 37 venues over six years, published through ICN Gateway, tender documents commonly ask about information security, privacy and quality management. An audit against ISO 27001 or ISO 9001 before you bid shows where your evidence is thin before a buyer finds it.
Can you audit systems that are past vendor support?
Yes. QAO’s Information systems 2025 report found half of the audited finance systems were past their supported life, so this is a live issue in Queensland. We assess the compensating controls in place, such as isolation, restricted access and monitoring, record the residual risk, and help you build a replacement case your executives can approve.
Next step
Send us the clause, questionnaire or policy that prompted the audit and we will come back with a scope and a fixed price. Contact us or email info@secsolutionshub.com.