
Security Solution Consultants (SSC) provides the cyber security services Christchurch organisations use when a customer, a health buyer, a regulator or their own board wants evidence that systems and personal information are protected. We are based in Tarneit, Victoria 3029, and work remote-first with Canterbury clients, coming on site for workshops, plant and OT reviews, data centre visits and findings walkthroughs where being in the room adds value. The work ranges from ISO/IEC 27001 and SOC 2 readiness for exporters to HISO 10029 evidence for health suppliers, Privacy Act 2020 uplift and internal audits before an external assessor arrives.
Christchurch’s economy shapes what we are asked for. Business Canterbury described the city in May 2026 as New Zealand’s second largest manufacturing centre, and Canterbury produces about one fifth of the country’s agricultural GDP. The city is home to technology exporters such as Tait, Seequent and Lumin, and an aerospace cluster is forming around the Tāwhaki Kaitorete runway, opened in February 2024, with a regional target of $1 billion and 1,500 jobs by 2035. Each of these faces different questions, so our IT compliance services in Christchurch start with the questions you are actually being asked.
Which rules apply in Canterbury
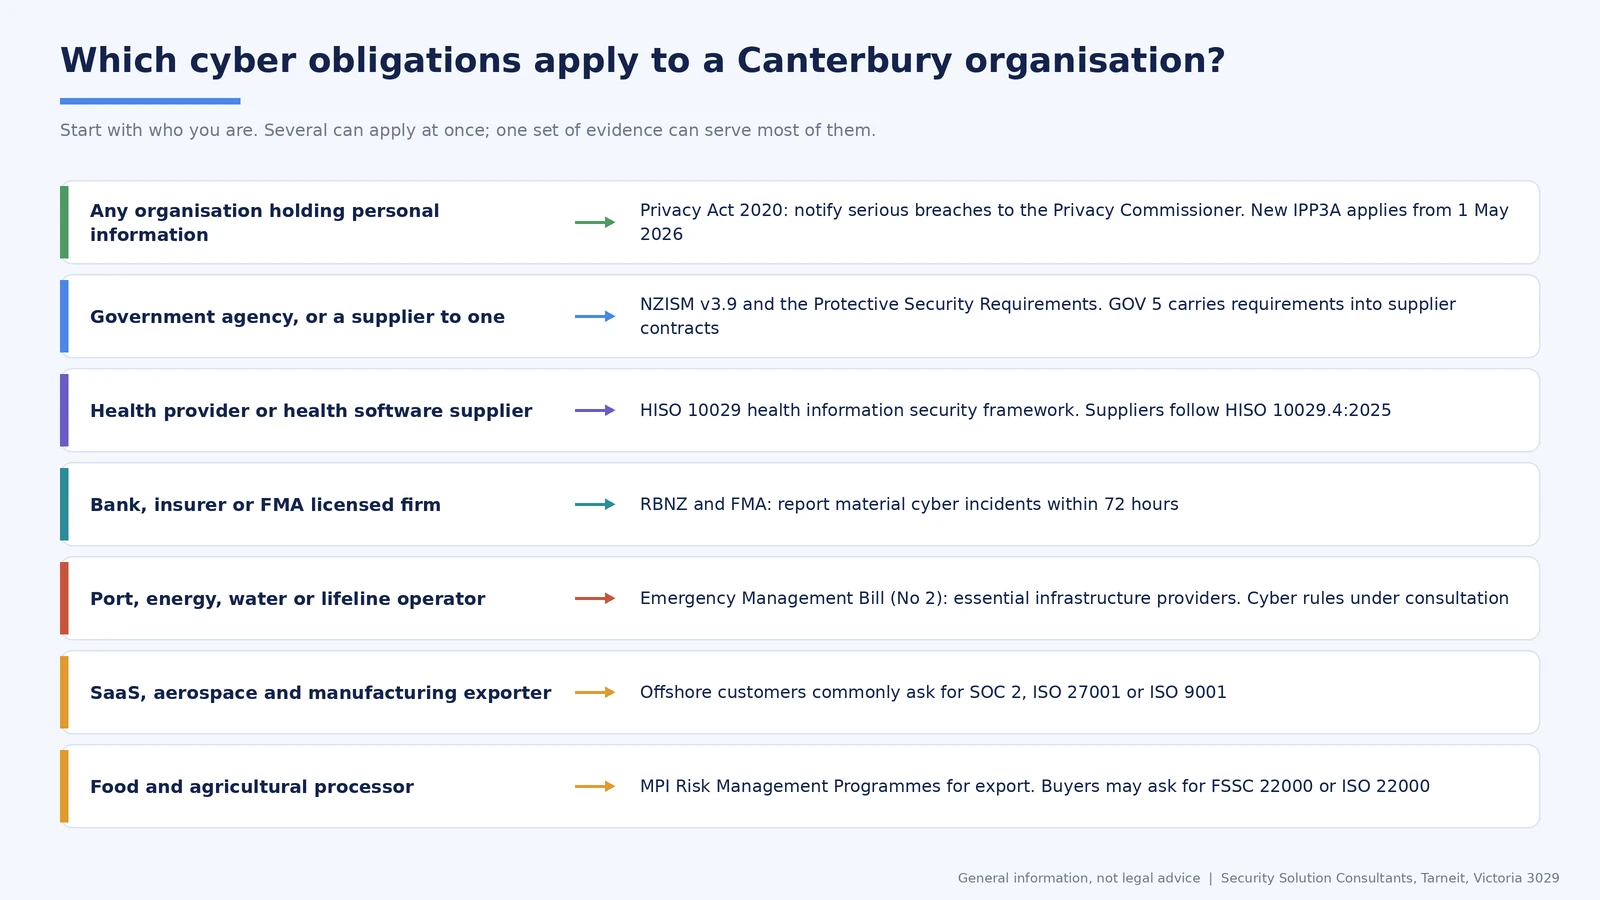
Canterbury has no regional cyber security law, so organisations here work to national rules. Which ones apply depends on what you are and who you sell to.
Councils and council organisations. Christchurch City Council, Environment Canterbury and the Selwyn and Waimakariri district councils are not among the agencies mandated to follow the Protective Security Requirements (PSR), but they hold large amounts of ratepayer and customer information under the Privacy Act 2020. He Puna Taimoana, the council’s hot pools, is the local reminder: on 24 August 2022 cloud-stored files containing identity documents for up to 20,000 people were accessed. A routine customer process at one facility created a privacy exposure far larger than the facility itself.
Agencies and their suppliers. Public service departments, NZDF, Police, NZSIS and the Parliamentary Counsel Office must follow the PSR and the New Zealand Information Security Manual (NZISM). Canterbury suppliers meet these second-hand: GOV 5 carries security obligations into contracts, and under GOV 6 agencies report incidents to the National Cyber Security Centre (NCSC), so expect a clause asking for prompt notice. Agencies must also risk-assess public cloud services, which is why SaaS vendors receive long questionnaires before signing.
Health providers and their suppliers. Health NZ Waitaha Canterbury, private hospitals, general practices and the firms that host or support their systems work to HISO 10029, the Health Information Security Framework, which now has a part for suppliers (see below).
Financial services and lifeline utilities. Reserve Bank-regulated entities and FMA licensees carry 72 hour incident reporting duties. Water, energy and telecommunications operators face new essential infrastructure duties, covered in the critical infrastructure section.
Every other organisation. The Privacy Act 2020 applies to businesses, charities and clubs of every size. A notifiable privacy breach must be reported to the Privacy Commissioner, ideally within 72 hours, and failing to notify can attract a fine of up to $10,000.
For boards, a useful benchmark is the Office of the Auditor-General’s April 2025 report Mind the gap: Governing cyber security risks: most organisations it examined carried more residual cyber risk than their appetite allowed, and incident response had not been tested enough. That makes a fair starting checklist for any Canterbury audit and risk committee.
Certifications Christchurch businesses ask us about
Six topics come up again and again, mostly driven by buyers and export markets rather than by law. We prepare you and run internal audits; certificates and attestation reports come from independent bodies.
- SOC 2. Software exporters selling into North America commonly hear the same first question from procurement: can we see your SOC 2 report? We scope the trust services criteria, close the gaps and get you ready for the observation period. The report itself is issued by a licensed CPA firm.
- ISO/IEC 27001. For Christchurch firms selling to government, health and overseas buyers at once, one certified information security management system answers most questionnaires, and its controls line up closely with NZISM and HISO 10029.4. Certification is by an accredited certification body; our guide to ISO 27001 certification in New Zealand explains the path.
- ISO/IEC 42001. Software and aerospace businesses adding machine learning to their products are starting to meet AI governance questions in enterprise due diligence. ISO/IEC 42001 sets up an AI management system beside ISO 27001 that answers them with records rather than reassurance.
- ISO 9001. A manufacturing centre of Christchurch’s size has a long supplier chain in which quality certification is a routine tender requirement. Aerospace buyers often expect AS9100, which is built on ISO 9001, so a sound quality system is the first step for suppliers hoping to join the region’s aerospace supply chain, including the firms around Kea Aerospace’s new 3,000 square metre hub (August 2026).
- ISO 22000. Canterbury’s share of national agricultural GDP makes food processing a major employer. Dairy and meat processors already run MPI Risk Management Programmes, and export customers commonly ask for ISO 22000 or FSSC 22000 on top. We align the food safety management system with the RMP so one set of records serves regulator and customer.
- Critical infrastructure security. Water, energy and telecommunications operators, and the contractors that maintain their systems, are preparing for essential infrastructure duties. See our energy sector security advisory and business continuity management services.
Critical infrastructure in Canterbury
Canterbury’s critical services are concentrated and closely connected. Lyttelton Port handled 427,462 TEU in FY26, and the region’s manufacturers and food exporters rely on it. Health NZ Waitaha Canterbury runs the hospital network, and council water networks serve Christchurch, Selwyn and Waimakariri.
New Zealand does not yet have a dedicated critical infrastructure security law. The Department of the Prime Minister and Cabinet (DPMC) consulted on a critical infrastructure cyber discussion document from 27 February to 19 April 2026, and no bill has been introduced. Separately, the Emergency Management Bill (No 2) passed its third reading on 28 August 2026; under it, lifeline utilities become essential infrastructure providers. The Cyber Security Strategy 2026 to 2030, published in February 2026, sets the wider direction.
The practical work need not wait for a bill: know which systems keep the service running, test the continuity plan against a cyber scenario, separate OT from corporate networks where you can, and control and log contractors’ remote access. Our critical infrastructure and OT security training gives engineering and operations staff a shared language for that work.
Our services in Christchurch
- Compliance gap assessment. One review against everything that applies to you, from the Privacy Act and NZISM to HISO 10029, ISO 27001 or a customer contract, ending in a single prioritised roadmap.
- IT security audits. Independent internal audits and readiness reviews before a certification body, customer or health buyer looks.
- ISO 27001, SOC 2 and ISO 42001 readiness. Management system design, risk assessment, policies and evidence, with support during the external audit.
- HISO 10029 supplier evidence. Mapping your product, hosting and sub-contractors to HISO 10029.4:2025.
- Privacy Act 2020 uplift. Breach response, IPP3A notices, retention of identity documents and privacy impact assessments.
- Incident response and risk management. Plans, tabletop exercises and risk registers a board can use.
- Compliance training and small business security. Courses for the staff who will run the system, and a proportionate programme for firms without a security team.
Health suppliers and HISO 10029
Health NZ Waitaha Canterbury sits at the centre of a regional network of private providers, practices, laboratories and technology suppliers, and the security expectations for that network are set by HISO 10029, the Health Information Security Framework. The 2022 core standard is supported by segment guidance published in 2023: HISO 10029.1 for hospitals, HISO 10029.2 for micro to small organisations and HISO 10029.3 for medium to large organisations.
The newest part matters most to Christchurch’s technology sector. HISO 10029.4:2025, published on 6 May 2025, is written for suppliers: SaaS providers, internet service providers, outsourced providers and their sub-contractors. If your software stores, processes or connects to health information, expect health customers to ask how you meet it.
We treat HISO 10029.4 as one more lens on a single control set. We map your product architecture, hosting and support model to the supplier requirements, work out which sub-contractors fall in scope, reuse evidence you already hold for ISO 27001 or SOC 2, and close the gaps that remain. The output is an evidence pack a procurement or clinical governance team can review without weeks of back-and-forth, plus a dated plan for anything still open.
National rules that changed in 2025 and 2026
IPP3A, added to the Privacy Act 2020 by the Privacy Amendment Act 2025, has applied since 1 May 2026: when you collect personal information about someone from a third party, you must take reasonable steps to let them know. NZISM v3.9, released in April 2025, is the current version, and the PSR keeps reaching suppliers through contract terms. Reserve Bank-regulated entities have reported material cyber incidents within 72 hours since 8 April 2024, and FMA licensees have carried a technology resilience condition with 72 hour notification since 1 July 2024. HISO 10029.4:2025 gave health suppliers a defined standard. For most Christchurch organisations the first action is a privacy one: list where you collect information indirectly, such as referrals, partner data or purchased lists, and update notices to match.
GRCLens: one evidence set, many reports
Canterbury organisations often answer to several requirements at once: a certification for export customers, a supplier standard for health buyers and the Privacy Act for everyone. GRCLens, the GRC platform we build, maps the frameworks you work to onto one shared control model, so evidence is captured once and reported many times, with audit findings and remediation kept in the same place for the next cycle.
Need an independent audit first?
If your customer or board wants an independent view before you invest, start with our IT security audit services for Christchurch organisations, which test controls against ISO 27001, HISO 10029, NZISM or the contract clause you have been given. We also work with organisations in Wellington, Auckland and across New Zealand.
Penetration testing and security testing in Christchurch
In 2022 files on a cloud server used by He Puna Taimoana, the council-run hot pools, were accessed, exposing proof of residency documents for up to 20,000 people. Exposed cloud storage and web applications are a common route to that kind of incident, which is why penetration testing in Christchurch often starts with internet-facing services and cloud configuration.
Christchurch’s software exporters, aerospace firms and manufacturers sell to customers who expect evidence: a recent penetration test, a SOC 2 report or ISO 27001 certification. We test web applications, APIs and mobile apps, review AWS, Azure and Microsoft 365 configuration, and run internal network tests for manufacturers whose engineering and production systems share a network with the office. Health software suppliers in Canterbury work to HISO 10029.4:2025, and secure code review and threat modelling help development teams meet it by design. See our penetration testing and security testing services, or an IT security audit in Christchurch.
Frequently asked questions
Should a Christchurch software exporter start with SOC 2 or ISO 27001?
Follow your buyers. If most revenue comes from North American enterprise customers, SOC 2 is usually the first request. If you sell to New Zealand government, health or European buyers, ISO 27001 tends to carry more weight. Many exporters end up with both, which stays manageable when one control set feeds both: build the ISO 27001 management system first, then add the SOC 2 criteria and observation period.
We supply a government department from Christchurch. Does the PSR apply to us?
Not directly. The Protective Security Requirements are mandated for public service departments, NZDF, Police, NZSIS and the Parliamentary Counsel Office. They reach you through GOV 5, which requires those agencies to manage security in their supply chain, usually through contract clauses that point to NZISM v3.9. Read your contract schedule: it, rather than the PSR itself, sets out what you must evidence and how quickly you must report incidents.
What does IPP3A mean for a Canterbury business in practice?
Since 1 May 2026, when you collect personal information about someone from another source, such as a referral, a partner organisation or a purchased list, you must take reasonable steps to let that person know, unless an exception applies. Start by listing every indirect collection route, then update privacy notices, onboarding messages and your agreements with the parties who pass information to you.
Our software is used by Canterbury health providers. Which HISO document covers us?
HISO 10029.4:2025, the supplier part of the Health Information Security Framework, published on 6 May 2025. It covers SaaS providers, internet service providers, outsourced providers and their sub-contractors. Your health customers still work to the core HISO 10029:2022 and their own segment guidance, so it also helps to know which of their obligations depend on your controls.
Where does critical infrastructure reform stand for a Canterbury lifeline utility?
Two tracks are moving. DPMC consulted on a critical infrastructure cyber discussion document from 27 February to 19 April 2026, but no bill has been introduced. The Emergency Management Bill (No 2) passed its third reading on 28 August 2026 and makes lifeline utilities essential infrastructure providers. Continuity planning, OT segmentation and supplier access control are sensible preparation under either track.
Should a Christchurch business keep copies of customers’ identity documents?
Only if you genuinely need them. The Privacy Act 2020 expects you to collect only what is necessary for a lawful purpose and not to keep it longer than required. Where you must verify identity, consider recording that you sighted the document instead of storing a scan. The 2022 He Puna Taimoana incident showed how stored ID files can expose thousands of people at once.
Will you come to Christchurch, or is everything done remotely?
Most work is remote: document review, evidence collection, interviews and reporting all run well over video. We come to Christchurch and wider Canterbury, including Selwyn, Waimakariri and further afield, when it adds value: management workshops, manufacturing and OT site reviews, data centre visits and the findings walkthrough with your leadership team.
Next step
Tell us what prompted the question, whether a SOC 2 request from an overseas buyer, a HISO 10029.4 questionnaire or a board asking about privacy risk, and we will suggest the smallest piece of work that answers it. Contact us or email info@secsolutionshub.com.

