
Security Solution Consultants (SSC) carries out the IT security audit Christchurch organisations commission when a buyer, a health agency, an insurer or their own audit and risk committee wants independent evidence that controls are in place and working. We are based in Tarneit, Victoria 3029, run most audit work remotely and come to Canterbury for site work, OT reviews and the findings walkthrough. Each cyber security audit in Christchurch is measured against the requirement you are actually held to, whether ISO/IEC 27001, HISO 10029, NZISM, the Privacy Act 2020 or a single clause in a customer contract.
Who in Christchurch is asking for audits, and why
Exporters facing customer due diligence. Christchurch’s software and technology exporters, and the aerospace firms gathering around Tāwhaki Kaitorete and Kea Aerospace’s new hub, are asked for proof before they are asked for prices. An internal audit against ISO 27001, or a SOC 2 readiness assessment, tells you what a customer’s assessor will find before they find it.
Health suppliers. Since HISO 10029.4:2025 was published, technology firms serving Health NZ Waitaha Canterbury, practices and private providers have a defined supplier standard to be measured against. A HISO 10029 assessment shows where your product, hosting and sub-contractors meet it and where they fall short.
Councils and their organisations. Christchurch City Council, Environment Canterbury and the surrounding district councils hold sensitive customer data in cloud services. The access to He Puna Taimoana’s cloud files on 24 August 2022, involving identity documents for up to 20,000 people, is a local example of why committees should ask what customer data each service collects, where it is stored and how long it is kept.
Manufacturers. In New Zealand’s second largest manufacturing centre, large customers commonly send supplier security questionnaires, and plants with automated lines need someone to look at operational technology as well as office IT.
Financial services. Reserve Bank-regulated entities and FMA licensees must notify material incidents within 72 hours. An audit of detection and escalation shows whether that clock can realistically be met.
Audit, technical assessment or penetration test?
These three are often sold as if they were interchangeable. They are not.
A compliance audit compares what you do with a written requirement, such as ISO 27001 clauses, HISO 10029.4 or a contract schedule, and records where practice and requirement differ. It produces evidence that someone else can rely on.
A technical assessment examines configuration: identity settings, patch levels, cloud storage permissions, backups and exposed services. It tells you how secure you are, regardless of any standard.
A penetration test has a tester actively try to break in within agreed limits. It shows what an attacker could achieve today, but says nothing about whether your management system works. If a penetration test is what you need, see our penetration testing and security testing services.
Most Christchurch clients need the first, sometimes informed by the second.
How an IT security audit runs
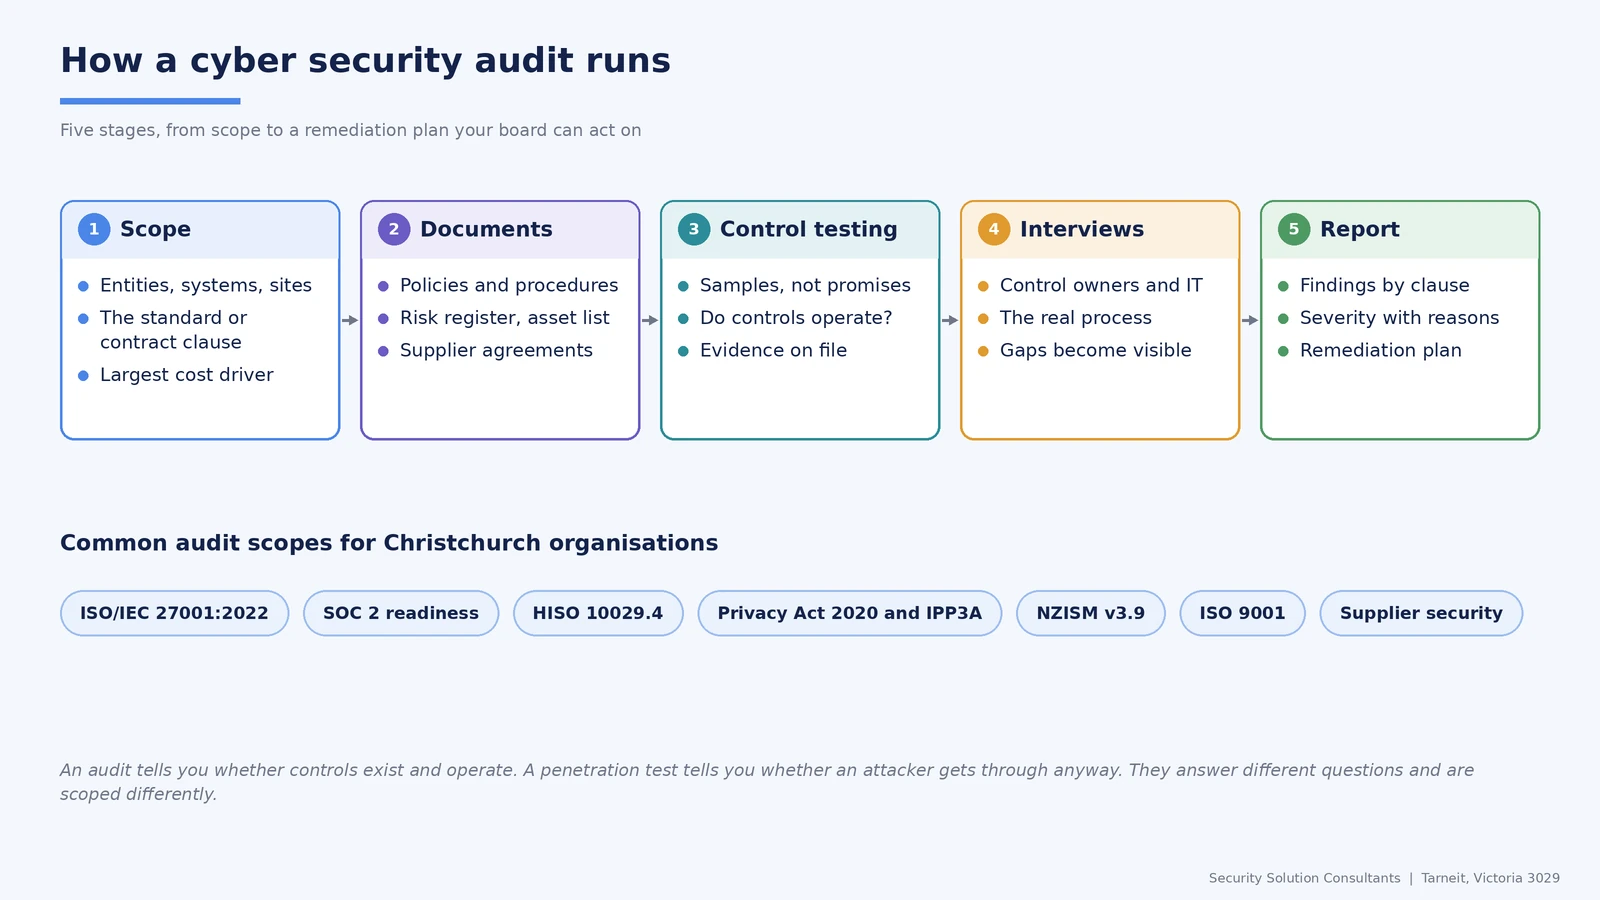
1. Scope. We agree the entities, systems, cloud services, sites and standard in scope. A tight scope tied to the actual requirement keeps the cost down; a vague one inflates it.
2. Documents. We read your policies, risk register, asset and data inventories, supplier contracts and previous findings. Gaps in the paperwork are recorded as findings in their own right.
3. Control testing. We sample records, settings and logs to confirm each control operates: access reviews that were completed, backups that were restored, accounts that were disabled on the day someone left.
4. Interviews. We talk to the people who own and perform the controls, from IT and the product team to whoever handles customer identity documents at the front desk.
5. Report. Findings are rated, mapped to the clause or requirement and paired with practical remediation. We walk your team through them so the report turns into work.
Which standard should a Christchurch audit use?
- ISO/IEC 27001:2022. An internal audit under clause 9.2, or a readiness review before the certification body’s stage 1 and stage 2 audits. See ISO 27001 implementation and advisory.
- HISO 10029 and HISO 10029.4:2025. For health providers working from the core standard and segment guidance, and for suppliers asked to show they meet the supplier requirements.
- NZISM v3.9 and the PSR. For suppliers whose agency contracts invoke GOV 5 or specific NZISM controls.
- Privacy Act 2020. A privacy controls review covering breach notification readiness, retention of identity documents and the IPP3A notice obligation in force since 1 May 2026.
- SOC 2 readiness. A pre-assessment against the trust services criteria before a licensed CPA firm begins its examination. See SOC 2 readiness consulting.
- ISO/IEC 42001. For software and aerospace firms that want their AI governance tested before a customer asks. See ISO 42001 consulting.
- Combined audits with ISO 9001 or ISO 22000. Manufacturers and food processors can fold information security into their existing quality or food safety internal audit, using our ISO 9001 and ISO 22000 consulting.
- Your customer’s clause. Bring the schedule. We audit to it and nothing wider unless you ask.
Deliverables, timing and price
What you receive. A report that ties every finding to a clause or requirement, explains the rating, names a practical fix and an owner, and opens with a one-page summary for directors. A walkthrough follows, and on request the findings are loaded into GRCLens so remediation can be tracked to closure.
How long. A single Christchurch organisation with a focused scope usually needs a few days of fieldwork, then reporting. Groups, several sites or OT add time. In practice the timetable is set by how quickly evidence arrives.
What it costs. Price follows scope, not headcount. We agree the scope and then quote a fixed fee, so there are no daily-rate surprises. If you need a certificate, only an accredited certification body can issue it, so budget for that audit separately from ours.
Canterbury specifics that change the scope
Cloud file stores holding identity documents. The He Puna Taimoana incident showed that a folder of scanned identity documents can be the most sensitive asset an organisation holds. For any Canterbury organisation that collects customer ID, we put SaaS and cloud storage permissions, sharing links and retention in scope by default.
Health supply chains run through local technology firms. When a Christchurch software company serves health customers, the audit has to follow data through hosting providers and sub-contractors, because HISO 10029.4 covers them too.
Plants and the port run operational technology. Manufacturing lines, food processing and the logistics chain around Lyttelton Port, which handled 427,462 TEU in FY26, depend on systems that cannot be patched or restarted on an office schedule. Where OT is in scope we test on site, alongside operations staff, and plan around production.
Audits across Canterbury
Most of each audit can be delivered remotely, so organisations in Selwyn and Waimakariri, Ashburton, Timaru and on the West Coast receive the same scope and report as those in central Christchurch. We travel for the parts that need it. We also run audits in Auckland and for organisations in Wellington.
For ongoing advice, certification readiness and HISO 10029 support beyond a single audit, see our cyber security services and compliance consulting in Christchurch.
Frequently asked questions
Do we need an ISO 27001 internal audit before our certification audit?
Yes. Clause 9.2 of ISO/IEC 27001 requires internal audits at planned intervals, and certification bodies expect to see at least one completed internal audit and management review before they recommend certification. Christchurch firms often ask us to run that first internal audit, because the people who built the system find it hard to audit their own work objectively.
What does a HISO 10029 assessment involve for a supplier?
We read your security documentation, test the controls that support your health customers, and map the results to HISO 10029.4:2025. Scope covers the product, hosting, support access and any sub-contractor that touches health information. You receive a gap list and an evidence pack for health buyers, with a remediation plan for anything outstanding.
Can the audit include our SaaS tools and cloud file storage?
It should. Shared drives, collaboration tools and cloud storage hold much of the personal information Canterbury organisations collect, often with sharing settings nobody has reviewed. We check permissions, external sharing, retention, logging and who administers each service, then flag which findings carry privacy breach risk under the Privacy Act 2020.
Will an audit from SSC satisfy a customer asking for SOC 2?
Not on its own. A customer asking for SOC 2 wants an examination report from a licensed CPA firm. Our readiness assessment tests your controls against the trust services criteria first, so you go into the CPA firm’s examination with fewer surprises. Some customers accept a readiness report and roadmap as an interim answer, so it is worth asking them.
Will the audit look at operational technology on our factory floor?
If production systems support the products or services in scope, they should be included. We review separation between office IT and the plant, remote access used by integrators and vendors, backups of controller configurations and who can change them. The work is observation and configuration review rather than live scanning, done on site with your engineers and timed around production.
Can our council-controlled organisation give the report to its audit and risk committee?
Yes. We write the summary for governors and relate findings to the issues the Office of the Auditor-General raised in its April 2025 report Mind the gap: residual cyber risk above appetite and untested incident response. That lets the committee see where your organisation stands and track remediation at each meeting.
What happens after the audit report is delivered?
We walk through the findings with the people who will fix them, agree priorities and owners, and leave you with a plan. If you want, we load the findings into GRCLens for tracking, return later to retest the high-severity items, or support your team while it remediates. You decide how much follow-up you need.
Next step
Send us the request that started this, whether a customer questionnaire, a HISO 10029.4 schedule, an ISO 27001 timetable or a board action item. We will reply with a proposed scope and a fixed fee. Contact us or email info@secsolutionshub.com.

