The Biometric Processing Privacy Code grace period ended on 3 August 2026. If your organisation scans faces, fingerprints or voices, the transitional relief you were relying on has now gone. Here is what the Code requires, who it covers, and what to check first. 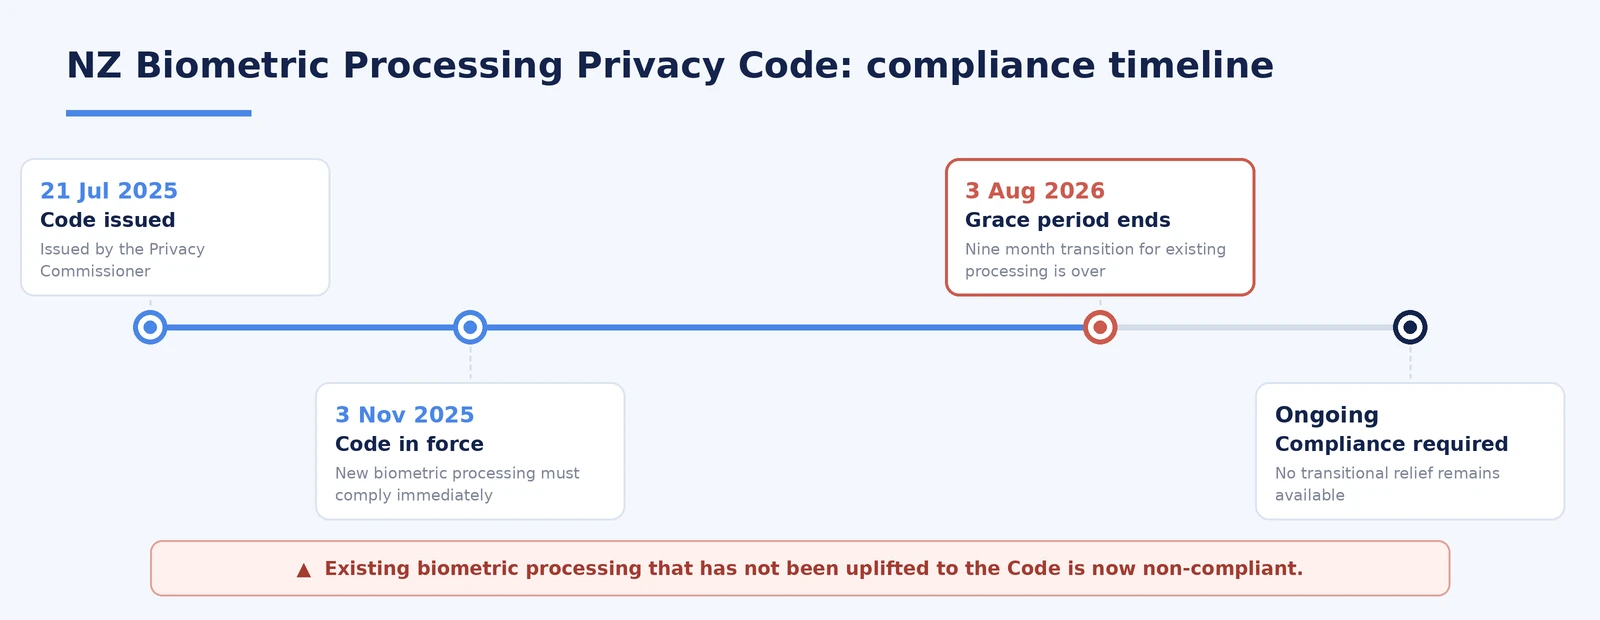
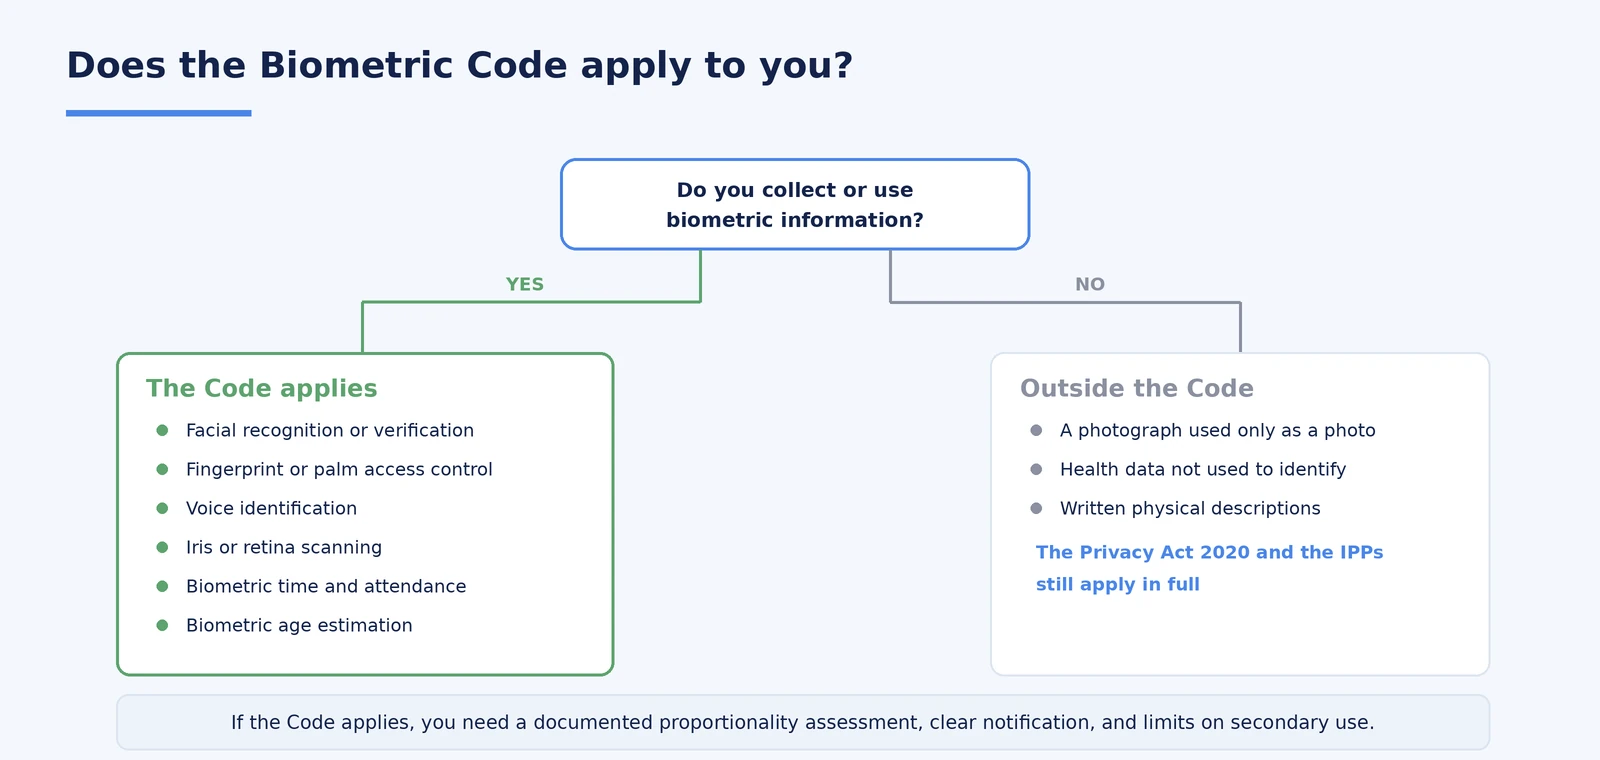 Broadly, you are in scope if you use an automated system to recognise or assess someone from a physical or behavioural characteristic. Facial recognition is the obvious case. Nevertheless, several less obvious systems also qualify.
The Biometric Processing Privacy Code is now fully in force
New Zealand has regulated biometrics for a while. However, the rules were general. They sat inside the Privacy Act 2020 and applied to biometric data the same way they applied to any other personal information. That changed in 2025. The Privacy Commissioner issued a dedicated code of practice under section 202 of the Act. It came into force on 3 November 2025. As a result, biometric processing now has its own specific rulebook. The Code did not land all at once, though. Organisations already running biometric systems received a nine-month transition period. That window closed on 3 August 2026. Consequently, every organisation in scope must now comply in full.Two commencement dates, and only one still matters
Plenty of Biometric Processing Privacy Code guidance published last year separated the timeline into two tracks. It is worth restating them clearly, because the distinction has now collapsed.- New biometric processing started after 3 November 2025. Compliance was required immediately, from the moment processing began.
- Biometric processing already underway on or before 3 November 2025. These activities had nine months to reach compliance. That grace period ended on 3 August 2026.
Does the Biometric Processing Privacy Code apply to you?
The Code covers biometric information used for biometric processing. That sounds circular, so it helps to look at real examples instead. Broadly, you are in scope if you use an automated system to recognise or assess someone from a physical or behavioural characteristic. Facial recognition is the obvious case. Nevertheless, several less obvious systems also qualify.- Fingerprint or palm readers used for building access
- Biometric time and attendance clocks
- Voice identification in a contact centre
- Iris or retina scanning
- Facial age estimation at a point of sale
- Facial matching against a watchlist in retail
What the Biometric Processing Privacy Code actually requires
The Code layers extra obligations on top of the existing principles. Three of them drive most of the work.A proportionality assessment, documented before you start
This is the centrepiece. You must be satisfied that biometric processing is proportionate in the circumstances. Therefore you need to weigh the benefits against the privacy impact, and you must consider whether a less intrusive option would work. Crucially, this has to be more than a private conclusion. Regulators expect a written record. If you cannot show the reasoning, you cannot show proportionality.Clear, specific notification
People need to know what is happening. The Code sets a higher bar than generic privacy policy wording. You must tell people that biometric processing is occurring, explain why, and describe how they can raise a concern. Signage matters here. A small notice at an entrance rarely does the job on its own.Limits on collection and secondary use
The Code restricts certain uses outright. For example, it constrains biometric classification that infers sensitive characteristics such as emotional state or health. In addition, you cannot quietly repurpose biometric data collected for one reason and use it for another.Biometric Processing Privacy Code gaps we see most often
Across our assessments, the same Biometric Processing Privacy Code gaps recur. None of them are exotic. Nobody owns the system. Biometric access control is often bought by facilities or operations. Privacy teams then discover it late. Because ownership is unclear, no proportionality assessment ever gets written. The vendor is treated as the compliance answer. Suppliers will say their product is compliant. That claim covers their product, not your deployment. You remain accountable for the decision to use it. Retention is indefinite by default. Many systems keep templates until someone deletes them. Consequently, organisations hold biometric data on people who left years ago. Old systems were never revisited. This is the direct consequence of the grace period ending. A fingerprint reader installed in 2019 was in scope from 3 November 2025 and had to be uplifted by 3 August 2026.Your Biometric Processing Privacy Code checklist
Start narrow and move fast. This Biometric Processing Privacy Code sequence works well.- Build the inventory. List every system that touches biometric information, including door access, payroll clocks and contact centre voice tools.
- Confirm scope for each one. Decide whether the Code applies, and write down why.
- Write the proportionality assessment. Do this for each in-scope system, not once for the organisation.
- Fix notification. Update signage, privacy statements and onboarding material.
- Set retention and deletion rules. Then actually delete the historical templates you no longer need.
- Review your vendor contracts. Check where templates are stored and who can access them.