
Security Solution Consultants (SSC) carries out the cyber security audit Dunedin organisations commission when they need an independent answer to a plain question: do our controls work the way we say they do? We are based in Tarneit, Victoria 3029, run most fieldwork remotely, and travel to Otago for site visits, workshops and the findings presentation. Every audit is measured against a named yardstick, whether that is ISO/IEC 27001, HISO 10029.4:2025, NZISM, the Privacy Act 2020 or a customer’s contract.
Who in Dunedin commissions audits, and why
Organisations with large user populations. The University of Otago alone has more than 4,000 full-time equivalent staff and nearly 19,000 full-time equivalent students. Its 2022 student database exposure, open to anyone with a university login from 23 August to 5 October 2022, showed how permissions inside a big environment can go wrong quietly. Universities, health services and large employers are natural candidates for access and permissions audits that look for the same problem in their own systems.
Health suppliers. Software, cloud and IT firms serving health providers are assessed against HISO 10029.4:2025. An independent audit gives them a report to share with health customers instead of answering every supplier questionnaire from scratch.
Food processors and exporters. Silver Fern Farms is headquartered in Dunedin, and meat and dairy together made up more than half of Otago’s $3.14 billion of exports in 2024. Processors under MPI Risk Management Programmes depend on records systems that must stay available and accurate, and export buyers commonly ask how those systems are protected.
Councils. Dunedin City Council and the Otago Regional Council report to elected members and fall within the Auditor-General’s mandate. The Auditor-General’s 2025 work on cyber governance pointed to incident response plans that had not been tested enough. An independent audit gives a council committee its own evidence rather than a management assurance.
Technology and data firms. From origin verification to game development, Dunedin firms sell to global customers who send security questionnaires. An audit ahead of an ISO 27001 certification or a SOC 2 examination shows the gaps while there is still time to close them.
Three kinds of security work, and which one you need
A compliance audit compares your controls with a stated benchmark and records, clause by clause, where you meet it and where you fall short. It is the right tool when someone outside the organisation wants evidence. A technical assessment inspects how systems are built and configured, for example privileged accounts, patching, cloud settings and exposed services, and ranks the weaknesses it finds. It answers how secure you are, not whether you comply. A penetration test is an authorised, time-boxed attempt to break in or escalate access, proving whether a specific weakness can actually be used. Each answers a different question and none substitutes for another. If a funder, a health customer or a certification body has asked for assurance, start with the audit. If a penetration test is what you need, see our penetration testing and security testing services.
How a cyber security audit in Dunedin runs
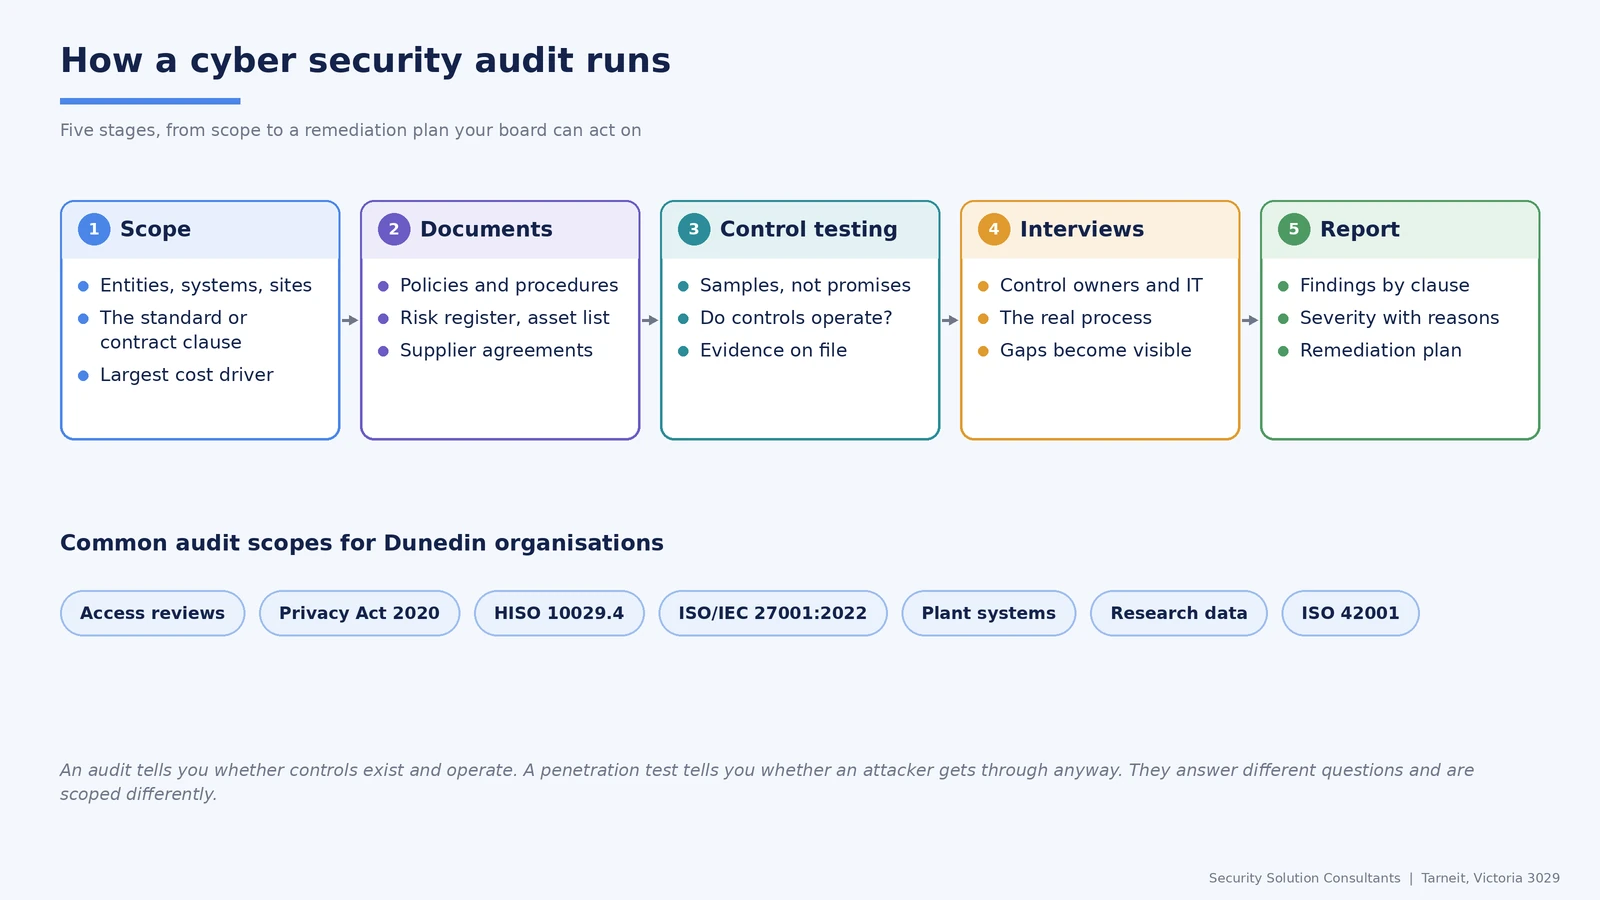
- Scope. We agree the yardstick, the systems and the boundaries. For a university department or research group, that means deciding which datasets, platforms and partner connections are in.
- Documents. We read what you have: policies, data inventories, access procedures, supplier agreements and incident plans. Missing documents become findings.
- Control testing. We pull samples: who can reach the most sensitive data, whether leavers were removed, whether backups restore, whether anyone reviews the logs.
- Interviews. We talk with data owners, system administrators, researchers and managers, because the real process often differs from the written one.
- Report. Findings ranked by risk and tied to the standard, each with a recommended fix and an owner, presented to the people who will act on them.
Standards we audit against in Otago
- Privacy Act 2020 and IPP3A. A privacy audit of collection, notices, indirect collection under IPP3A, storage, access, retention and breach notification to the Privacy Commissioner.
- HISO 10029.4:2025. Supplier assurance for SaaS, ISPs and outsourced providers to health, built on the HISO 10029:2022 core framework.
- ISO/IEC 27001:2022. Internal audits and certification readiness. See ISO 27001 implementation advisory.
- NZISM v3.9 and the PSR. For suppliers to mandated agencies, where GOV 5 brings security requirements into the contract and GOV 6 governs incident reporting to the NCSC.
- SOC 2 readiness. A pre-examination review against the Trust Services Criteria before a licensed CPA firm starts its work. See SOC 2 readiness consulting.
- ISO/IEC 42001. For research groups and companies building or deploying AI. See ISO 42001 consulting.
- ISO 9001, and ISO 22000 or FSSC 22000. Internal audits for manufacturers and food processors, aligned with Risk Management Programme records. See ISO 9001 and ISO 22000 consulting.
- Biometric Processing Privacy Code 2025. For organisations using facial recognition or fingerprints for access, attendance or identity checks.
Deliverables, duration and price
What you receive. A report that states scope and limits plainly, lists each finding against the relevant clause with a risk rating, and sets out a fix sequence your team can follow. A one-page summary for the council, board or senior leadership. A walkthrough session. If you want next year’s audit to begin where this one ended, the evidence and findings can go into GRCLens.
How long it takes. Fieldwork for a focused scope, such as one business unit or one platform, is normally measured in days. Faculty-wide, multi-site or multi-supplier audits take longer. The pace is set mostly by how quickly documents and samples arrive.
What it costs. A fixed figure, agreed after scoping. Price depends on the number of systems, datasets, sites and suppliers in scope and the standard used, not on how many people you employ. If you are heading for ISO 27001 certification, budget separately for the accredited certification body, which must be independent of us.
Otago specifics that change the scope
Inherited access in large institutions. Where thousands of staff and students share platforms, group-based permissions build up over years. We weight testing towards who can see what because, as the university’s 2022 exposure showed, a permissions problem can persist for weeks without looking like an incident.
Research data moves between organisations. Research projects often receive data from hospitals, other universities and overseas partners. We bring data sharing agreements, IPP3A notices and partner platforms into scope, since that is where responsibility tends to blur.
Processing sites are spread across the region. Meat, dairy and fruit operations stretch from coastal Otago to Central Otago. Remote sites often have thin IT support and long-standing vendor remote access, so we check how plant systems connect back to head office and who can reach them from outside.
Audits across Otago and the South
We audit organisations in Dunedin, Mosgiel and Port Chalmers, and across Otago in Oamaru, Balclutha, Alexandra, Cromwell, Queenstown and Wānaka. Most of the work runs remotely, so a Central Otago orchard business or a Queenstown tourism operator gets the same audit method and report as a Dunedin head office, with site visits added where they earn their cost. For ongoing compliance work, certification support and HISO 10029 readiness, see our cyber security services in Dunedin and Otago.
Frequently asked questions
What does a privacy audit in Otago check?
It tests how you handle personal information against the Privacy Act 2020: what you collect and why, what people are told, how indirect collection is handled under IPP3A, who can access records, how long you keep them and how you would assess and notify a breach. For health or research data we also look at supplier contracts and data sharing agreements.
How do you test who can see sensitive data in a large organisation?
We sample the most sensitive systems and datasets, export their permission lists and compare them with who should have access. Group memberships, shared drives, service accounts and former staff get particular attention. Where logging exists, we check whether anyone reviews it. The result is a list of over-broad access, ranked by sensitivity, that your administrators can work through quickly.
Is a HISO 10029.4 audit a form of certification?
No. HISO 10029.4:2025 is a New Zealand health standard rather than a certification scheme. An audit against it produces an independent report on how well a supplier meets the expectations for SaaS, ISP and outsourced services, which health customers can rely on in their own assurance. Some suppliers pair it with ISO 27001 certification, issued separately by an accredited body.
How long does an IT security audit in Dunedin take?
A focused audit of one system, business unit or supplier relationship usually needs only days of fieldwork, then reporting. Larger scopes covering several sites, faculties or suppliers take longer. You control much of the timeline: having policies, access lists and supplier contracts ready before we start is the easiest way to shorten it.
Do you audit food processors’ plant systems as well as offices?
Yes. For meat, dairy and fruit businesses we look at the systems that hold Risk Management Programme records, traceability and export documents, and at how plant networks connect to the office and to vendors. Site walkthroughs help here. We do not run intrusive tests on live processing equipment unless that is planned separately with whoever maintains it.
Can SSC’s audit report stand in for ISO 27001 certification?
No. If a customer specifies certification, only an accredited certification body can issue it. Our audit is still useful on that path: run as an internal audit, it meets the standard’s internal audit requirement and shows what to fix before the certification body visits. If the customer will accept independent assurance instead of a certificate, our report can serve on its own.
Can you audit organisations in Queenstown and Central Otago?
Yes. Distance makes little difference to most audit work, which runs remotely through document sharing, screen-shared testing and video interviews. We schedule site visits for the parts that need them, such as physical security or plant networks, and plan travel so the cost stays proportionate to the scope.
Next step
Share the request that started this, whether a health customer’s questionnaire, a certification timetable, a research partner’s data clause or a committee’s question, and we will suggest the narrowest audit that answers it. Contact us or email info@secsolutionshub.com. We also run audits in Auckland and across New Zealand.

